Attack Surface Cyber Security: Your Protection Guide
Every device you connect to your network creates another opportunity for attackers to break in. Your Windows PC, laptop, smartphone, printer, and even your smart TV each open a new door. Understanding attack surface cyber security helps you see these entry points clearly and take steps to close the ones you don't need. For home users, small business owners, and travellers, reducing your attack surface is one of the most effective ways to stay safer online without needing a technical background.
What attack surface cyber security means for you
Attack surface cyber security focuses on identifying and reducing all the ways an attacker might access your system. Think of it as every window, door, vent, and crack in your digital house. The NIST Computer Security Resource Center defines attack surface as the set of points where an unauthorised user can try to enter or extract data from your environment.
Your attack surface includes physical connections like USB ports, network interfaces such as Wi-Fi and Bluetooth, software applications you've installed, and online services you use. Each one represents a potential vulnerability.
When you work from a coffee shop in Johannesburg or connect to hotel Wi-Fi in New York, your attack surface expands dramatically. Public networks expose your PC to anyone on the same network who knows how to look for weaknesses.
Three types of attack surfaces you should know
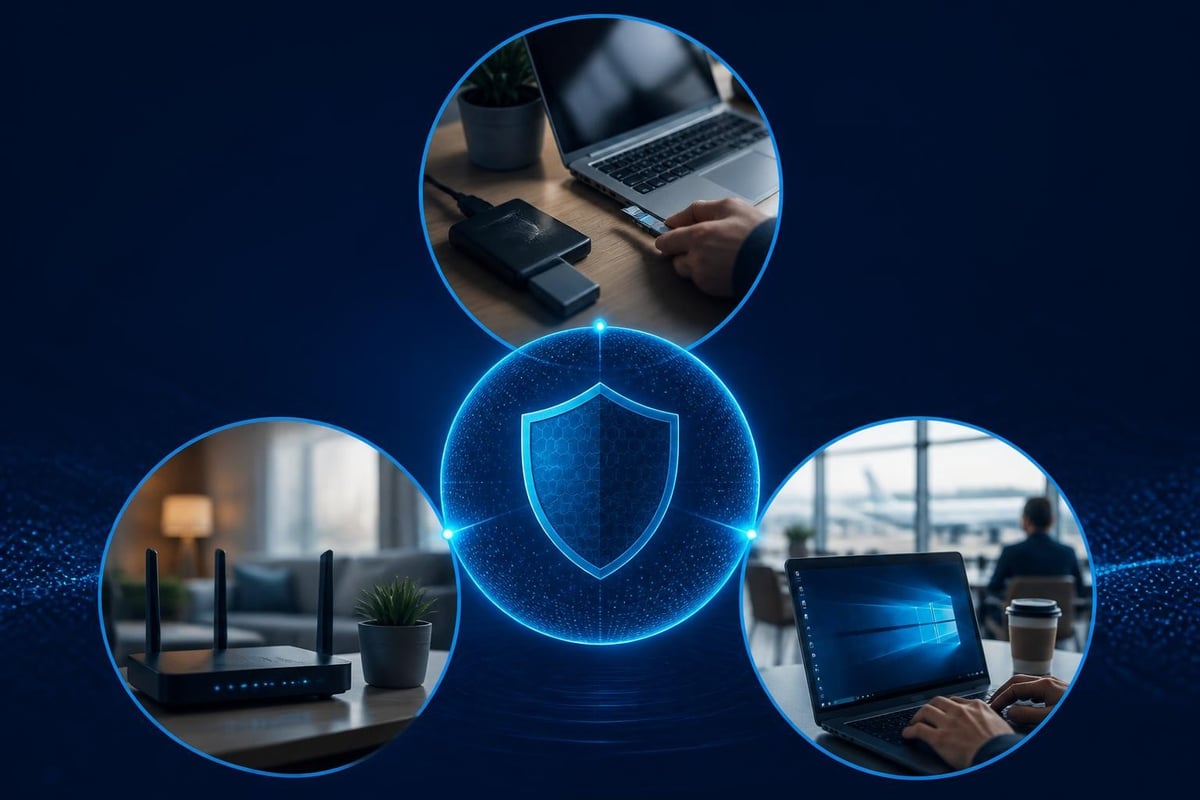
Physical attack surface covers hardware access points. USB drives can carry malware that installs the moment you plug them in. Someone with physical access to your laptop could boot from an external drive or install keylogging hardware.
Network attack surface includes all your network connections. Every open port on your Windows PC, every wireless network you join, and every Bluetooth device you pair creates an entry point. Attackers scan networks constantly looking for exposed services and weak configurations.
Software attack surface encompasses your applications, operating system, and all the code running on your machine. Outdated software with known vulnerabilities, unnecessary services running in the background, and excessive permissions granted to applications all expand this surface.
Why your attack surface grows without you noticing
Most people don't realize how quickly their attack surface expands. You install a new application to solve a problem, and it opens network ports to check for updates. You enable file sharing to transfer photos to your phone, and that service stays active for weeks. You connect a wireless printer, and it broadcasts its presence to the network indefinitely.
Each Windows update adds features you may never use, but those features often include services that listen for incoming connections. Legacy protocols stay enabled for compatibility even when you don't need them.
Common expansion points include:
- Remote desktop services left enabled after one-time use
- File and printer sharing active on public networks
- Bluetooth discoverable mode never turned off
- Browser extensions with broad permissions
- Cloud sync services running continuously
- Legacy SMB protocols enabled by default
Small businesses face additional challenges. When you add employees and devices, the multiplication effect is dramatic. Five people each using two devices, connecting to three networks daily, creates a complex web of exposure.
Practical steps to reduce your attack surface
You can take meaningful action today without specialized knowledge. Start by mapping what you have. List your devices, note which services they run, and identify which network connections they use regularly.
Turn off what you don't need. Windows 11 includes dozens of services and features most users never touch. Disabling unused components removes entire categories of potential vulnerabilities.
Prioritize these quick wins
Disable remote access features unless you specifically need them. Remote Desktop, Remote Assistance, and PowerShell remoting are powerful tools attackers love to exploit.
Review your network sharing settings for each network type. Windows distinguishes between private and public networks – make sure public networks have sharing disabled.
Audit your startup programs and background services. Many applications launch at boot and maintain network connections you don't need.
Remove software you don't use. Every installed application potentially contains vulnerabilities, and unused software never gets the attention it needs for updates.
Turn off Bluetooth and Wi-Fi when you're not actively using them. This simple step eliminates entire attack vectors during travel or when working offline.
The CISA exposure reduction guidance offers practical frameworks for discovering and evaluating exposed assets, particularly valuable when you're securing internet-facing services or running a small business network.
| Action | Impact | Difficulty |
|---|---|---|
| Disable unused services | High | Low |
| Remove old software | High | Low |
| Configure Windows Firewall | High | Medium |
| Segment network with VLANs | Very High | High |
| Implement least privilege | Medium | Medium |
| Regular software updates | Very High | Low |
Monitoring network connections on Windows PCs
You can't reduce what you can't see. Windows includes built-in tools to monitor active connections, but they're not designed for security-focused users who need clear, actionable information.
Resource Monitor shows active network connections in real-time. Press Windows+R, type "resmon", and navigate to the Network tab. You'll see which processes are sending and receiving data, but interpreting this information requires patience.
Windows Firewall with Advanced Security displays detailed rules controlling traffic. Many users never open this tool, yet it governs every network connection your PC makes.
The challenge is recognizing what's normal versus what's suspicious. A legitimate Windows update looks similar to malware calling home to its command server. Both involve background processes making outbound connections to IP addresses you don't recognize.
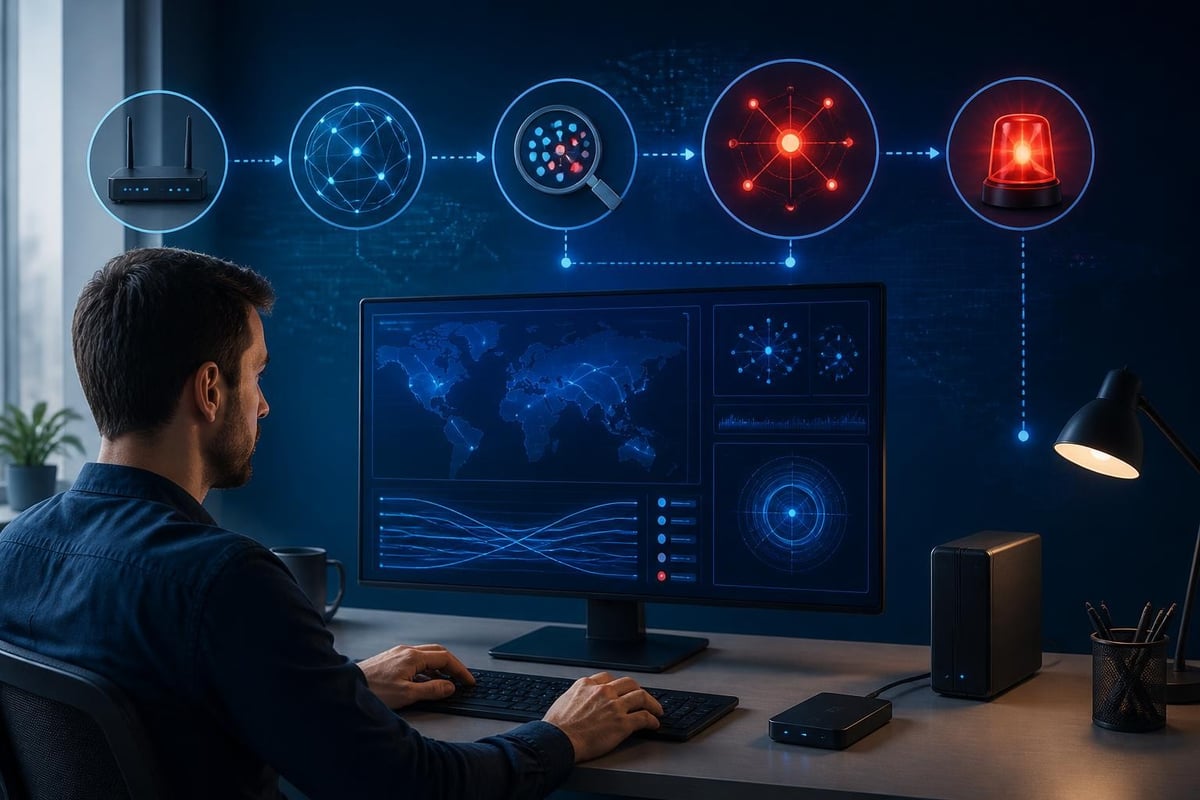
Attack surface cyber security tools that run locally on your Windows 11 machine give you visibility into these connections with context that helps you make decisions. They show you when a process you've never heard of suddenly starts communicating with servers in countries you don't do business with.
The role of segmentation and isolation
Network segmentation divides your network into separate zones, limiting how far an attacker can move if they breach one area. For home users, this might mean separating smart home devices from your work PC. For small businesses, it means isolating customer data systems from guest Wi-Fi.
PC isolation takes this concept to the device level. When you detect a threat, immediately cutting a compromised machine off from the network prevents lateral movement. Attackers often breach one vulnerable device then explore your network looking for valuable targets.
Windows 11 includes features to support isolation, but they require configuration:
- Windows Defender Application Guard isolates Edge browser sessions
- Windows Sandbox runs untrusted applications in a disposable environment
- Network isolation settings control which devices can communicate
The MITRE ATT&CK framework documents how segmentation and service limitation directly counter attacker techniques, providing a roadmap for prioritizing your defensive efforts.
Travellers face unique challenges. Hotel and airport networks put you alongside hundreds of unknown devices. A VPN encrypts your traffic but doesn't isolate your PC from network-based attacks. True isolation means your PC refuses local network connections entirely when you're on untrusted networks.
Understanding software vulnerabilities and patches
Every piece of software on your PC was written by humans, and humans make mistakes. These mistakes become vulnerabilities when attackers figure out how to exploit them. MITRE’s Common Weakness Enumeration categorizes excessive attack surface as a weakness in itself, highlighting how unnecessary code and features create exploitation opportunities.
Zero-day vulnerabilities are particularly dangerous. These are flaws attackers know about before the software vendor does. You can't patch what hasn't been disclosed, making attack surface reduction even more critical. Smaller surface means fewer potential zero-days affecting you.
Windows Update handles Microsoft software, but your attack surface includes every third-party application. PDF readers, media players, compression utilities, and productivity software all ship with vulnerabilities discovered months or years after release.
Building a practical update strategy
- Enable automatic updates for Windows and Microsoft applications
- Review installed software quarterly and remove what you no longer need
- Prioritize updates for network-facing applications like browsers, email clients, and communication tools
- Test updates on non-critical systems first if you're running a small business
- Track vendor security advisories for business-critical applications
The OWASP Infrastructure Security Risks project highlights how infrastructure misconfigurations and unpatched systems create the largest attack surfaces in modern environments.
Infrastructure risks for small businesses
Small businesses often outgrow home networking equipment without realizing their attack surface has become unmanageable. Consumer routers, default configurations, and shared administrator passwords create vulnerabilities that scale poorly.
When you have five Windows PCs, two printers, three smartphones, and a server in your office, you're running infrastructure that needs deliberate security architecture. Many small businesses discover they have no firewall between their payment processing system and the laptop their teenage employee's friend borrows to check email.
Common small business attack surface problems:
- Printers with default passwords accessible from the internet
- File shares visible to every device on the network
- Remote access portals with weak authentication
- Port forwarding rules from years ago nobody remembers creating
- Unencrypted wireless networks for "convenience"
- Backup systems connected permanently to production networks
The NIST SP 800-53 security controls include attack surface reviews as part of federal security requirements. While written for government agencies, the principles apply equally to small businesses that need structured approaches to managing risk.
Ransomware and attack surface cyber security
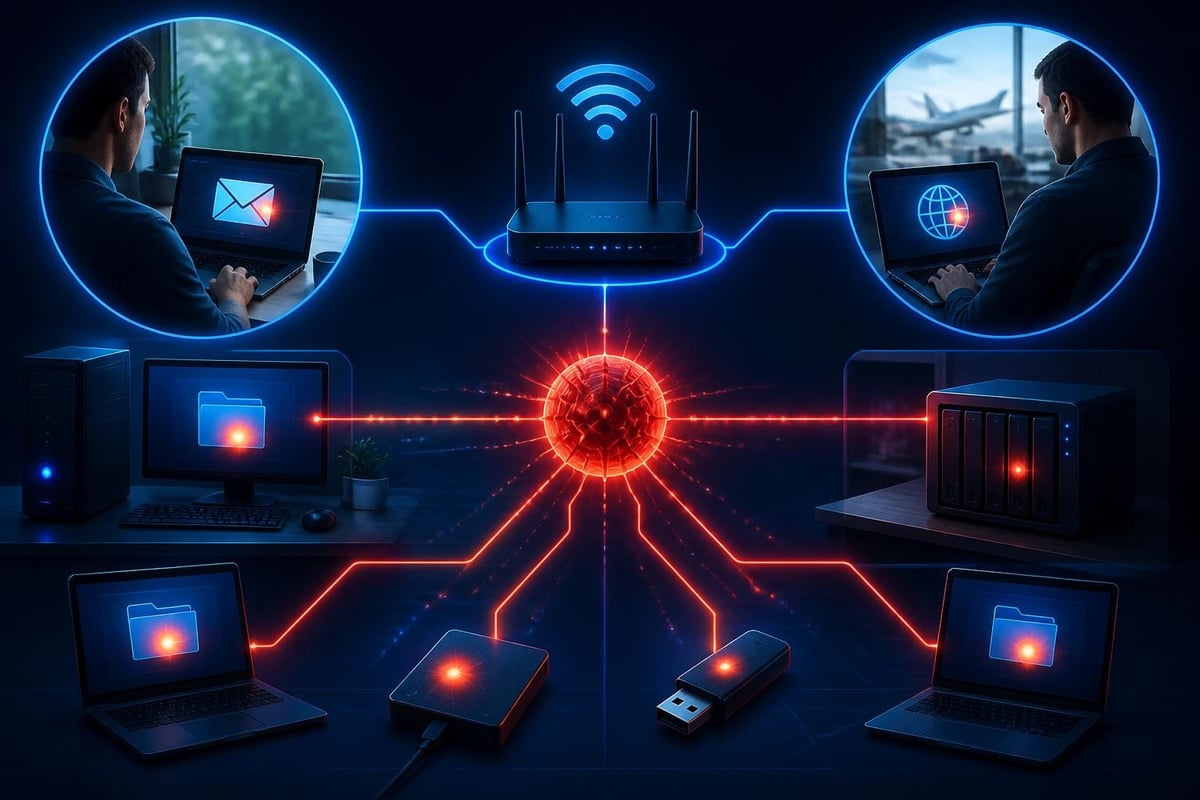
Ransomware needs access to your files before it can encrypt them. Reducing your attack surface directly reduces ransomware risk by limiting entry points and constraining what malware can reach if it gets in.
Ransomware typically enters through:
- Phishing emails with malicious attachments
- Compromised websites that exploit browser vulnerabilities
- Remote desktop services with weak or default credentials
- Network shares accessible without authentication
- USB devices carrying infected files
Traditional antivirus software tries to identify ransomware by its signature or behavior. This works for known threats but struggles with new variants. Attack surface reduction takes a complementary approach: assume something will get past your antivirus, then limit what it can do.
Behaviour monitoring watches for ransomware patterns like rapid file encryption. Combined with network monitoring that spots connections to known command-and-control servers, you create layers of defense that don't depend on recognizing specific malware.
NetGuardian Pro's approach focuses on detection at the network level, watching for the communication patterns ransomware exhibits when it tries to reach its controllers or spread across your network. By monitoring network connections continuously, it can alert you to suspicious activity before encryption begins, giving you the chance to isolate your PC and prevent disaster.
Detection strategies that work for non-technical users
You don't need a computer science degree to spot suspicious activity. Attack surface cyber security tools designed for regular users present information in plain language and focus on what you can act on.
Effective detection tells you:
- Which program is making the connection
- Where it's connecting to (country, company, reputation)
- Whether this connection is new or routine
- What data is being sent or received
- Whether it matches known threat patterns
Clear alerts beat technical logs. When something unusual happens, you need to know in terms you understand: "A program you installed yesterday is trying to connect to a server in a country you don't do business with." That's actionable. "TCP SYN packets detected on port 445" is not.
Threat intelligence feeds provide context. They map IP addresses and domains to known malicious infrastructure, so your detection system can warn you when a connection matches known attacker resources.
False alarms undermine security. If your tools cry wolf daily, you'll start ignoring alerts. Learning systems that understand your normal patterns significantly reduce false positives. When your PC always connects to certain servers for legitimate software updates, that shouldn't trigger warnings.
Building defense in depth
Attack surface reduction is one layer in a comprehensive security strategy. You still need antivirus software, regular backups, strong passwords, and security awareness. The goal is making each layer reinforce the others.
Your security stack should include:
| Layer | Purpose | Examples |
|---|---|---|
| Perimeter defense | Block known threats at network edge | Router firewall, DNS filtering |
| Endpoint protection | Detect and remove malware | Antivirus, anti-malware |
| Network monitoring | Spot suspicious connections and behavior | Intrusion detection, traffic analysis |
| Access control | Limit who can do what | Strong passwords, least privilege |
| Data protection | Secure data at rest and in transit | Encryption, VPN |
| Backup and recovery | Restore after incidents | Offline backups, disaster recovery |
This approach recognizes that perfect prevention is impossible. Attackers constantly develop new techniques. Your defense needs to detect and limit damage when prevention fails.
For travellers, VPNs encrypt your internet traffic but don't protect against local network attacks. You need both encryption for privacy and network-level protection that watches for attacks coming from devices on the same hotel or airport Wi-Fi.
Privacy and attack surface overlap
Reducing your attack surface often improves privacy simultaneously. When you disable unnecessary services and limit which applications can access the internet, you reduce both security vulnerabilities and data collection opportunities.
Many applications transmit telemetry, usage statistics, and personal information as part of their normal operation. From an attack surface perspective, each of these connections is a potential vulnerability. From a privacy perspective, they're sharing your data with third parties.
Windows 11 telemetry settings control how much diagnostic data Microsoft collects. Setting these to minimum levels reduces your attack surface by limiting outbound connections while also improving privacy.
The same principle applies to installed software. Applications that "phone home" create persistent network connections attackers might intercept or impersonate. Limiting telemetry reduces attack surface and privacy exposure together.
Advanced considerations for technical users
If you're comfortable with command-line tools and registry editing, you can reduce attack surface much further. PowerShell scripts can disable entire subsystems like SMBv1, which remains a frequent attack vector despite being legacy technology.
Windows hardening techniques include:
- Disabling NetBIOS over TCP/IP
- Removing PowerShell 2.0 (lacks security features)
- Configuring AppLocker to whitelist applications
- Enabling Credential Guard on supported hardware
- Restricting NTLM authentication
- Disabling LLMNR and WPAD
The SoK research on driver isolation frameworks examines how operating system design choices affect attack surface at the kernel level. While highly technical, it demonstrates that attack surface considerations extend deep into system architecture.
Attack surface management tools from enterprise vendors offer discovery, enumeration, and continuous monitoring features. Google’s approach illustrates how large organizations systematically catalog and assess their exposure, techniques you can adapt at smaller scale.
For small businesses, the SANS research on visibility and attack surface provides insight into how practitioners bridge the gap between discovering exposures and taking action to reduce them.
Making attack surface reduction sustainable
The actions you take today only help if you maintain them. Attack surfaces grow naturally as you add devices, install software, and enable new features. Sustainable security means building review and reduction into your routine.
Monthly reviews should check:
- Installed applications (remove what you haven't used in 90 days)
- Startup programs (disable anything non-essential)
- Windows Firewall rules (remove temporary exceptions that became permanent)
- Network sharing settings (verify public networks stay protected)
- Bluetooth and Wi-Fi settings (ensure you're not broadcasting unnecessarily)
Quarterly, dive deeper:
- Review all user accounts and remove old ones
- Audit file share permissions and network access
- Test your backup restore process
- Update your network map as devices change
- Research new hardening techniques for Windows 11
Annual reviews should cover:
- Major software upgrades (does that upgrade add features you don't need?)
- Hardware refresh planning (new devices mean new attack surface)
- Threat landscape changes (what are attackers focusing on in 2026?)
- Your security tool effectiveness (are you getting value from your protections?)
For small businesses, documenting your attack surface and reduction efforts supports compliance requirements and helps onboard new employees who need to understand your security posture.
Practical reality for home users and families
You want protection without becoming a full-time security administrator. The most sustainable approach prioritizes the actions with the biggest impact and the lowest maintenance burden.
Start with the fundamentals that Windows makes relatively easy: keep software updated, use Windows Defender, enable the built-in firewall. These foundational steps are free, require minimal configuration, and provide substantial protection.
Add tools that work continuously without requiring constant attention. Network monitoring that alerts you to problems but doesn't require hourly checking fits this model. You want protection that enhances your awareness without demanding expertise.
For families, attack surface cyber security extends to every device in your home. Children's devices need protection appropriate to their risk profile. Teenagers browsing social media, streaming video, and gaming online create different exposures than young children using educational apps on tablets.
The challenge is balancing protection with usability. Overly restrictive controls frustrate users who then find workarounds that bypass security entirely. Effective protection works with your family's actual behavior rather than against it.
Understanding and reducing your attack surface gives you meaningful control over your security without requiring deep technical knowledge. By focusing on the entry points that matter most, disabling what you don't need, and monitoring what remains, you build practical protection that fits your real-world needs. NetGuardian Pro brings attack surface cyber security principles to your Windows 11 PC with 14 detection modules that monitor network threats across Wi-Fi, USB and Bluetooth, clear alerts you can act on, and built-in VPN protection for travel. It complements your existing antivirus with network-level visibility and control, helping you spot and stop threats before they cause damage.
Related reading: Cyber Security Critical Infrastructure Protection 2026, Cloud Based Cyber Security Companies: A Practical Guide, Cyber Security IDS: Protection for Windows Networks.