Network Intrusion Detection Systems for Windows Users
Network intrusion detection systems watch your computer's connections for signs of attack or unauthorised access. They monitor traffic flowing in and out of your Windows 11 PC, alert you to suspicious behaviour, and help you act before damage occurs. Whether you're protecting a home network in Johannesburg, running a small business in Dallas, or connecting to public Wi-Fi in Cape Town, understanding how these systems work gives you control over your digital safety. This article explains what network intrusion detection systems do, how they differ from antivirus software, and how to choose protection that fits your needs.
How network intrusion detection systems work
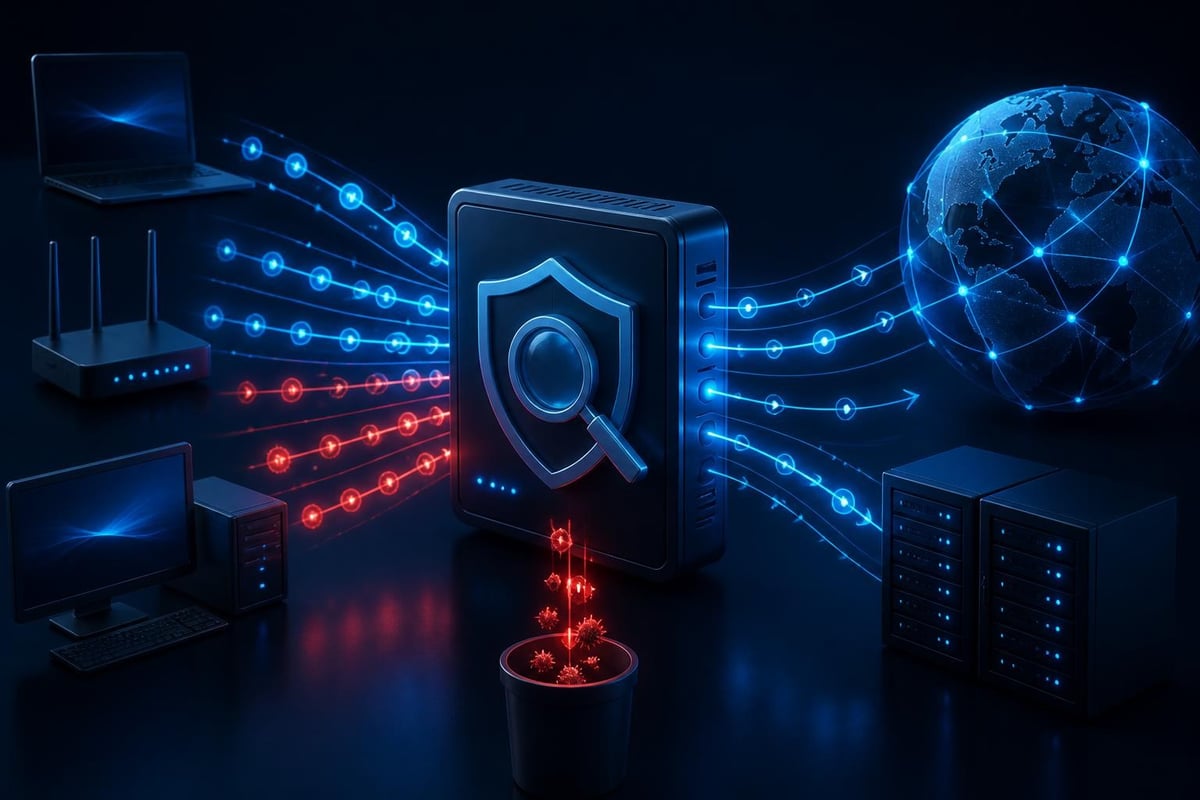
Network intrusion detection systems examine the data packets moving between your computer and the internet. Every time you browse a website, send an email, or use an app, your PC exchanges packets with servers and other devices. These systems inspect those packets for patterns that match known attacks or unusual behaviour that might signal a threat.
Signature-based detection compares network traffic against a database of known attack patterns. When a packet matches a signature for a specific exploit or malware communication, the system raises an alert. This method catches well-documented threats quickly and reliably. The official Snort documentation provides detailed guidance on how signature-based rules work in one of the most widely used open-source systems.
Anomaly-based detection learns what normal traffic looks like on your network, then flags deviations. If your laptop suddenly starts sending large amounts of data to an unfamiliar server at 3 a.m., that's anomalous. This approach can identify zero-day attacks and insider threats that lack known signatures, but it requires careful tuning to avoid false alarms.
Detection modules and monitoring scope
Modern network intrusion detection systems use multiple detection modules to cover different attack vectors. A comprehensive system monitors more than just your Wi-Fi connection.
- Wi-Fi monitoring watches wireless network traffic for man-in-the-middle attacks, rogue access points, and suspicious connections
- USB monitoring detects threats from USB devices that attempt network communication or data exfiltration
- Bluetooth monitoring identifies unauthorised Bluetooth connections and data transfer attempts
- Protocol analysis examines specific protocols (HTTP, DNS, SMB) for exploitation attempts
- Behaviour monitoring tracks application network behaviour to spot ransomware or spyware
The NIST Special Publication 800-94 offers foundational guidance on intrusion detection and prevention system architecture, helping you understand how different modules work together in enterprise and personal security contexts.
Differences between intrusion detection and antivirus software
Antivirus software and network intrusion detection systems serve different purposes, and you need both for complete protection. Antivirus scans files, emails, and downloads for malicious code that's already on your computer or trying to get in through file execution. It checks files against virus signatures and uses heuristics to catch new malware.
Network intrusion detection systems focus on connections rather than files. They watch who your computer talks to, what data moves in and out, and whether those conversations follow safe patterns. An intrusion detection system might catch an attacker scanning your network for vulnerabilities, a compromised application sending your data to a command-and-control server, or lateral movement attempts within your local network, even when no malicious file is present.
| Feature | Antivirus Software | Network Intrusion Detection Systems |
|---|---|---|
| Primary focus | Files and executable code | Network connections and traffic |
| Detection target | Malware, viruses, trojans | Network attacks, suspicious connections, data exfiltration |
| Monitoring scope | Disk, downloads, email attachments | All network traffic (Wi-Fi, Bluetooth, USB-to-network) |
| Threat examples | Ransomware executable, macro virus | Port scanning, C2 communication, lateral movement |
| Protection timing | Before file execution | During network communication |
Because these tools protect different attack surfaces, they complement each other rather than overlap. You should run both on your Windows 11 PC. Antivirus stops malicious files from executing; intrusion detection stops malicious network behaviour whether or not a file is involved.
Deployment options for Windows users
You have three main deployment approaches when implementing network intrusion detection systems, each with different technical requirements and coverage scope.
Host-based intrusion detection
Host-based systems run directly on your Windows 11 PC. They monitor network connections made by that specific computer, watching traffic at the network adapter level before it reaches or after it leaves your applications. This approach works well for laptops, home desktops, and small business PCs because it protects the device wherever it connects, whether on your home network, a coffee shop hotspot, or a hotel network while travelling.
Host-based systems see everything your PC sends and receives, including encrypted traffic before encryption or after decryption (depending on implementation). They consume some system resources but modern detection engines are efficient enough for daily use.
Network-based intrusion detection
Network-based systems sit at a central point on your network, usually between your router and the internet. They monitor all traffic crossing that point, protecting every device on your network from a single sensor. This approach suits small businesses with multiple computers, printers, and IoT devices on a shared network.
The challenge for home users and small businesses is deployment complexity. You need dedicated hardware or a compatible router, and the system can't inspect traffic that never crosses the central monitoring point (such as direct Bluetooth connections or USB network adapters).
Hybrid approaches
Some modern solutions combine host-based monitoring with centralised management and threat intelligence. Each PC runs its own detection engine while sharing alerts and updates with a management console. This gives you device-level visibility with network-wide coordination, but it requires more infrastructure than simple host-based protection.
Key features to look for
When evaluating network intrusion detection systems for your Windows 11 environment, focus on features that give you actionable protection without requiring deep technical expertise.
Clear, understandable alerts matter more than you might expect. An alert that says "TCP SYN flood detected from 192.168.1.47" means nothing to most users. Look for systems that explain what's happening in plain language: "A device on your network is trying to overwhelm your PC with connection requests, which might be an attack."
Blocking and response controls let you act on threats immediately. Detection alone tells you something is wrong; response capabilities let you block the connection, isolate your PC from the network, or stop a specific application's network access while you investigate.
Threat intelligence integration keeps detection signatures current. New attack patterns emerge daily, and your system needs regular updates to recognise them. Automatic updates without subscription fees give you ongoing protection without recurring costs.
False alarm reduction through machine learning helps separate real threats from normal behaviour variations. Systems that learn your typical network patterns flag fewer false positives over time, reducing alert fatigue.
The Suricata project features page describes how modern open-source intrusion detection systems incorporate these capabilities, though implementation varies significantly between enterprise tools and consumer-focused products.
Practical protection for common scenarios
Network intrusion detection systems address specific threats that Windows 11 users face in 2026. Understanding these scenarios helps you evaluate whether you need this layer of protection.
Detecting ransomware before encryption starts
Ransomware often communicates with command-and-control servers before encrypting your files. This communication fetches encryption keys, receives instructions, or reports back to attackers. An intrusion detection system can spot this unusual outbound connection pattern and alert you before the encryption phase begins, giving you time to disconnect and prevent damage.
Ransomware behaviour monitoring watches for specific network patterns associated with ransomware families. This includes connections to known malicious domains, unusual SMB traffic patterns suggesting lateral movement, and high-volume file access combined with external communication.
Identifying suspicious connections on public Wi-Fi
When you connect to public Wi-Fi at airports, hotels, or coffee shops, you share network space with strangers. An attacker on the same network might attempt to intercept your traffic, scan your PC for vulnerabilities, or inject malicious content into unencrypted connections.
Network intrusion detection systems alert you to port scanning, ARP spoofing attacks, and rogue access points designed to steal credentials. You'll see warnings about suspicious activity so you can disconnect or switch to a VPN before sensitive data is exposed. Solutions that include built-in VPN capabilities add another protection layer for travellers.
Catching unauthorised access attempts
Small businesses and home users sometimes face brute-force attacks against Windows network shares, Remote Desktop connections, or other services. If someone on your network or the internet repeatedly tries passwords against your PC, that's a clear sign of unauthorised access attempts.
Detection systems flag these patterns and can block the attacking IP address automatically. You'll know if someone is probing your defences, even if Windows Firewall is already blocking the attempts at the network level.
Monitoring IoT and smart device behaviour
Your home or small office network likely includes smart TVs, security cameras, printers, and other connected devices. These devices sometimes contain vulnerabilities that attackers exploit to gain network access. Some call home to manufacturers with more data than you'd expect.
Network intrusion detection systems help you see what your IoT devices are doing on the network. If your security camera suddenly starts uploading video to an unknown server, or your printer begins scanning other devices on the network, you'll get an alert.
Machine learning and modern detection techniques
The recent Frontiers survey on machine learning strategies reviews how artificial intelligence improves intrusion detection accuracy and speed. Modern systems use machine learning to identify attack patterns that signature-based rules miss and to reduce false alarms by understanding context.
Supervised learning trains detection models on labelled datasets of normal and malicious traffic. The model learns to classify new traffic based on features like packet size, timing, protocol usage, and connection patterns. This approach works well for detecting variants of known attack types.
Unsupervised learning finds anomalies without pre-labelled data. The system clusters traffic patterns and identifies outliers that don't fit any normal cluster. This catches novel attacks but requires careful tuning to avoid flagging legitimate unusual behaviour.
Adaptive baseline learning continuously updates its understanding of normal activity. As you add new applications, change usage patterns, or upgrade software, the system adjusts its baseline. This reduces false alarms without manual reconfiguration.
The arXiv paper on adversarial challenges highlights an emerging concern: attackers can craft traffic that evades machine learning detection. Robust systems combine multiple detection methods so that if machine learning fails, signature-based or rule-based detection still catches the threat.
Choosing protection for your Windows 11 PC
For home users, families, and small businesses running Windows 11, host-based network intrusion detection systems offer the best balance of protection, simplicity, and cost. You don't need network infrastructure changes, complex configuration, or ongoing subscription fees.
Look for solutions designed specifically for Windows 11 that complement your existing antivirus rather than trying to replace it. The system should run as a background service, consume minimal resources, and present clear alerts when threats appear.
When evaluating options, consider these practical factors:
- No subscription requirement: One-time payment models give you ongoing protection without recurring costs
- Automatic updates: Threat signatures and detection rules should update automatically
- Clear explanations: Alerts should tell you what's happening in plain language, not just technical codes
- Blocking controls: You should be able to stop suspicious connections immediately
- Support availability: Email or chat support helps when you need to interpret an alert or adjust settings
NetGuardian Pro provides network intrusion detection and prevention designed for Windows 11 users who want practical protection without IT expertise. Its 14 detection modules monitor Wi-Fi, USB, and Bluetooth connections, watch for ransomware behaviour, and deliver clear alerts when suspicious activity occurs. The system learns your normal network patterns to reduce false alarms, includes blocking controls for immediate response, and complements your existing antivirus software. A built-in WireGuard VPN adds protection when you're travelling or using public networks.
Configuration and ongoing management
After installing a network intrusion detection system, you'll go through an initial learning period. The system observes your normal network behaviour for a few days or weeks, building a baseline of legitimate activity. During this time, you might see more alerts as the system learns which applications you use, which servers they connect to, and what your typical traffic patterns look like.
Review alerts regularly during the first month. Each alert is a learning opportunity. When you see a warning, check whether it's a real threat or normal behaviour the system hasn't learned yet. Most systems let you whitelist legitimate connections so they don't trigger future alerts.
Keep your detection rules current. Automatic updates handle most of this work, but occasionally check that updates are applying successfully. New attack techniques emerge constantly, and outdated signatures leave gaps in your protection.
Adjust sensitivity settings based on your alert volume. If you're overwhelmed with false positives, increase the threshold for anomaly detection. If you're seeing no alerts at all, verify the system is actually monitoring traffic.
The Elastic blog on detection engineering offers practical guidance on tuning detection rules and building effective alert workflows, though much of the content targets enterprise security teams. The core principles apply at any scale: start with high-confidence detections, tune aggressively to reduce noise, and continuously refine based on what you learn.
Understanding detection performance and limitations
No security system catches every threat, and understanding the limitations of network intrusion detection systems helps you maintain realistic expectations and layer your defences appropriately.
Encrypted traffic poses challenges for signature-based detection. If an attacker uses HTTPS or another encrypted protocol, the intrusion detection system can't inspect packet contents for malicious patterns. It can still analyse metadata like connection timing, packet sizes, and destination addresses, but content-based signatures won't apply. This is why behaviour-based detection and anomaly detection matter, they work even when content is encrypted.
Zero-day exploits succeed until detection rules catch up. The time between exploit discovery and signature deployment creates a window where signature-based systems won't catch the attack. Anomaly detection provides some protection during this window, but it's not foolproof.
Insider threats are harder to detect when they use legitimate credentials and follow normal usage patterns. If someone with authorised access slowly exfiltrates data using approved applications, the traffic might look normal to automated detection systems.
Resource constraints can limit detection depth on lower-powered devices. Deep packet inspection requires processing power and memory. On older or resource-limited Windows 11 PCs, some systems reduce inspection depth to maintain performance.
The CISA Enhanced Visibility and Hardening Guidance provides recommendations for network visibility and monitoring that acknowledge these limitations while offering practical approaches to maximize detection coverage.
Integration with broader security practices
Network intrusion detection systems work best as part of a comprehensive security approach. They're not a silver bullet, but they fill important gaps that other tools miss.
Combine with Windows Firewall to block unwanted connections before they reach your applications. The firewall acts as your first line of defence, blocking connection attempts based on port and protocol. The intrusion detection system monitors allowed traffic for malicious behaviour.
Layer with VPN protection when using public or untrusted networks. The VPN encrypts your traffic end-to-end, preventing local attackers from intercepting data. The intrusion detection system still monitors connections, watching for malicious endpoints even when traffic is encrypted.
Maintain regular backups so that if an attack succeeds despite your detection systems, you can recover without paying ransom or losing data. Offline backups protect against ransomware that targets connected backup drives.
Keep Windows 11 and applications updated to close vulnerabilities that attackers exploit. Intrusion detection alerts you to exploitation attempts, but patching the vulnerability prevents successful exploitation entirely.
Use strong passwords and multi-factor authentication for your Microsoft account and other services. If credentials leak through a phishing attack or data breach, additional authentication factors prevent unauthorised access even when passwords are compromised.
You can explore additional security resources and guidance at NetGuardian Secure for Windows 11 protection strategies.
Selecting the right detection approach for your needs
Your choice of network intrusion detection systems depends on your specific situation, technical comfort level, and protection requirements.
Home users and families benefit most from host-based systems that run on each Windows 11 PC without network infrastructure changes. Look for solutions with clear explanations, simple controls, and automatic updates. You don't need enterprise-grade complexity; you need reliable alerts about real threats affecting your devices.
Small businesses with multiple PCs might choose host-based protection for each computer or a network-based system if you have someone comfortable with network configuration. Consider whether you need centralised management to monitor all devices from a single console, or if individual PC protection with standard settings meets your needs.
Travellers and remote workers require protection that travels with the device. Hotel networks, airport Wi-Fi, and coffee shop hotspots present different threats than your home network. Host-based detection with integrated VPN capabilities gives you consistent protection regardless of your connection point.
Users in high-risk regions or industries facing targeted attacks need more aggressive monitoring and faster response times. The MITRE ATT&CK resources help security teams understand adversary behaviours and map network detection capabilities to specific tactics, though this level of detail exceeds most small business needs.
Consider starting with basic intrusion detection that focuses on clear, actionable alerts about common threats. You can always expand coverage later as you gain confidence and understand your specific risk profile.
Interpreting alerts and taking action
When your network intrusion detection system alerts you to suspicious activity, you need to understand what you're seeing and decide how to respond. Most systems categorise alerts by severity: critical, high, medium, and low. Focus on critical and high alerts first, these represent immediate threats or behaviour strongly associated with attacks.
Read the alert explanation carefully. Good systems tell you what triggered the alert, which device or application is involved, and what the potential threat is. For example: "Your PC attempted to connect to a known command-and-control server used by ransomware. The connection was blocked."
Check whether the alert makes sense in context. If you just installed a legitimate application and it's connecting to its vendor's servers for updates, that's probably safe even if the detection system hasn't seen those servers before. If your PC is trying to connect to servers in countries you've never visited while you're asleep, that's suspicious.
Use blocking controls to stop suspicious activity immediately while you investigate. Most systems let you block a specific connection, an IP address, or an entire application's network access. Block first, investigate later when dealing with potential malware.
Document patterns if you see repeated alerts involving the same applications or destinations. This helps you identify compromised software, misconfigured applications, or aggressive adware that needs removal.
Seek support when you're unsure. Systems with included email support let you send alert details to security experts who can help you interpret what's happening and recommend next steps.
For ongoing updates on network security topics relevant to Windows 11 users, you can reference the NetGuardian Secure sitemap for additional articles and guidance.
Cost models and long-term value
Network intrusion detection systems come with different pricing models, and understanding total cost of ownership helps you make informed decisions.
Subscription-based services charge monthly or annually for software licenses, threat intelligence updates, and support. These costs continue indefinitely, increasing your total spending over time. A system costing twenty dollars per month costs two hundred forty dollars per year and twelve hundred dollars over five years.
One-time purchase models require an upfront payment and include ongoing updates and support at no additional cost. While the initial price might seem higher, total five-year cost is often lower than subscription equivalents. You also avoid budget uncertainty and price increases.
Open-source solutions are free to download and use, but they require significant technical expertise to deploy, configure, and maintain. For most home users and small businesses, the time cost of learning and managing open-source intrusion detection outweighs the license savings. The Suricata performance documentation illustrates the technical depth required to optimize open-source systems effectively.
Hardware costs vary by deployment type. Host-based systems run on your existing Windows 11 PC with no additional hardware. Network-based systems might require dedicated appliances or compatible routers.
Consider not just initial price but also ongoing costs, time requirements, and whether you'll actually use the system consistently. A sophisticated enterprise system with features you'll never use costs more than you need. A simple, clear system you check daily provides better protection than complex software you ignore.
Network intrusion detection systems give you visibility and control over your PC's connections, catching threats that antivirus software misses. For Windows 11 users in homes, small businesses, and on the road, host-based detection with clear alerts and simple controls offers practical protection without complexity. NetGuardian Pro delivers exactly that: fourteen detection modules monitoring Wi-Fi, USB, and Bluetooth connections, clear explanations of threats, immediate blocking controls, and built-in VPN protection, all with one-time payment and no subscription required.
Related reading: IDS in Cyber Security: Detection Systems Explained, Intrusion and Detection for Windows 11 Networks, Network Intrusion Systems for Windows 11: A Practical Guide.