IDS in Cyber Security: Detection Systems Explained
Intrusion detection systems form a critical layer of protection in modern cyber security, yet many Windows users don't fully understand what they do or how they complement existing security tools. IDS in cyber security refers to monitoring systems that watch network traffic and system behavior to identify suspicious activity, unusual patterns, or known attack signatures. Unlike antivirus software that focuses on malicious files, IDS watches how your device communicates across networks, helping you spot threats that slip past traditional defenses. Whether you're working from home, running a small business, or protecting your family's devices, understanding how IDS works helps you make smarter decisions about network security.
What intrusion detection systems actually do
An intrusion detection system watches network connections in real time, looking for patterns that suggest an attack or compromise.
Think of IDS in cyber security as a security camera for your network. While antivirus scans files and programs, IDS monitors the conversations your device has with the outside world through Wi-Fi, wired connections, and even USB or Bluetooth interfaces. It analyzes this traffic against known attack patterns (signatures) and normal behavior baselines to spot anomalies.
IDS typically detects:
- Unauthorized connection attempts from remote attackers
- Data exfiltration patterns suggesting information theft
- Port scanning and network reconnaissance activity
- Command and control traffic from malware
- Lateral movement attempts across your network
- Protocol anomalies that indicate exploitation attempts
The NIST Special Publication 800-94 provides comprehensive guidance on IDS deployment and operations, helping organizations understand the different types and their capabilities.
Signature-based versus behavioral detection
IDS in cyber security uses two primary detection approaches, often combined for better coverage.
Signature-based detection compares network traffic against a database of known attack patterns. When traffic matches a signature for a SQL injection attempt, port scan, or exploit kit, the IDS flags it immediately. This method catches known threats reliably but misses new attack variations.
Behavioral detection (also called anomaly detection) learns what normal activity looks like for your device, then alerts you when something deviates significantly. If your laptop suddenly starts uploading gigabytes of data at 3 AM, or connects to servers in countries you've never contacted before, behavioral detection notices even if no signature exists for that specific threat.
| Detection Method | Strengths | Limitations |
|---|---|---|
| Signature-based | Catches known attacks reliably, few false positives, clear threat identification | Misses zero-day attacks, requires frequent updates, ineffective against novel techniques |
| Behavioral | Detects unknown threats, identifies insider threats, adapts to environment | Higher false positive rate initially, requires training period, needs tuning |
| Hybrid | Best of both approaches, broader coverage, validates detections | More complex to configure, requires more processing power, needs skilled interpretation |
Most effective IDS implementations use both methods together. Signatures catch the known bad, while behavioral analysis spots the suspicious unusual.
Types of IDS and where they run
Understanding where IDS in cyber security operates helps you choose the right protection for your situation.
Network-based IDS (NIDS) sits on your network segment, watching all traffic flowing through. In enterprise environments, NIDS devices monitor traffic at network boundaries and key internal points. For home users and small businesses with Windows devices, NIDS functionality often runs as software on individual PCs, monitoring that device's network connections.
Host-based IDS (HIDS) runs directly on the protected device, monitoring not just network connections but also system logs, file changes, and running processes. This gives deeper visibility into what's happening on that specific machine.
Key differences:
- NIDS sees traffic across multiple devices but can't inspect encrypted connections easily
- HIDS provides detailed insight into one device, including local activity and encrypted traffic before it leaves
- NIDS works well for protecting network perimeters and server segments
- HIDS excels at protecting individual endpoints like laptops, particularly for remote workers
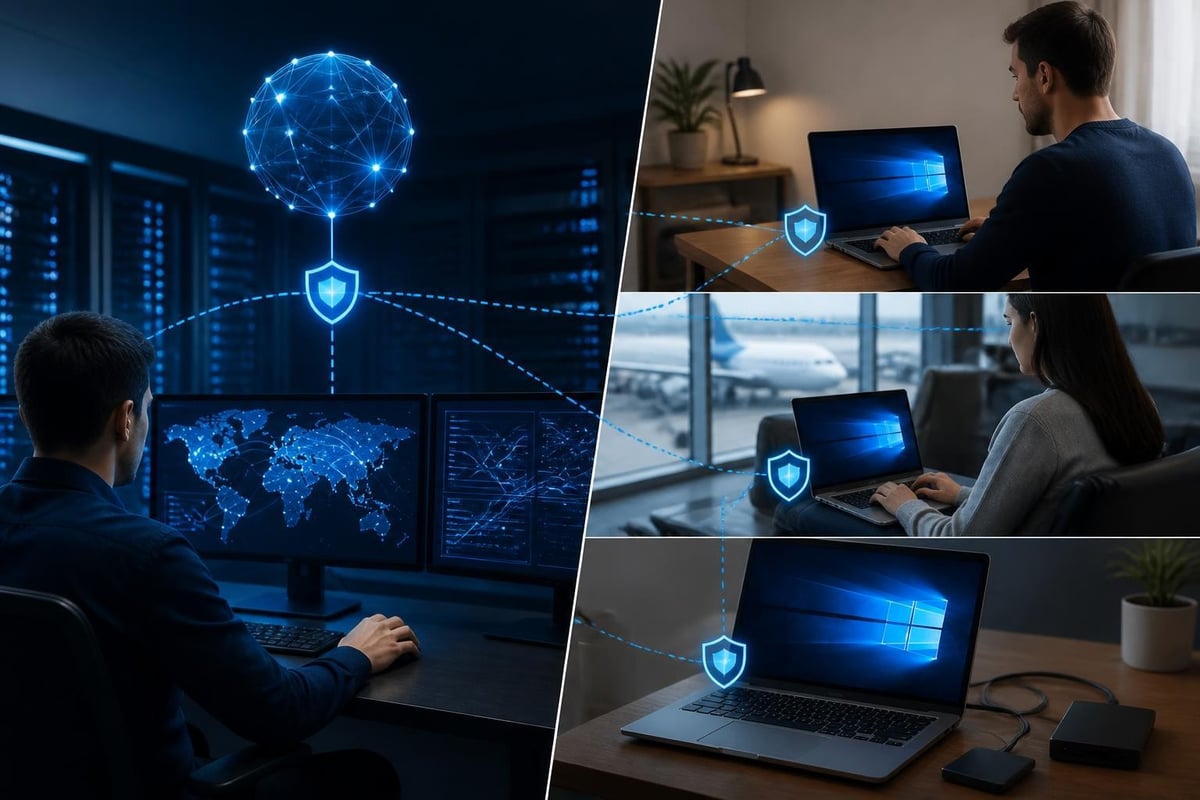
For Windows 11 users, particularly those working remotely or traveling, host-based IDS running on your PC provides protection regardless of which network you connect to. The detection travels with your device rather than depending on network infrastructure you don't control.
Cloud and hybrid deployments
The rise of cloud computing has expanded where IDS in cyber security can operate.
Cloud IDS solutions monitor traffic within cloud environments, protecting virtual machines and cloud services. Google Cloud’s intrusion detection system illustrates how cloud-native IDS integrates with cloud infrastructure, providing visibility that traditional network IDS can't achieve in virtualized environments.
For small businesses and home users, the practical question is whether protection runs on your local device or in the cloud. Local IDS on your Windows PC works without internet connectivity, doesn't send your traffic to third parties, and responds instantly. Cloud-based analysis can leverage threat intelligence from millions of devices but requires sending network metadata externally.
Hybrid approaches combine both: detection runs locally for privacy and speed, while threat intelligence updates come from cloud sources to keep signatures current.
How IDS detects modern threats
IDS in cyber security has evolved significantly to address today's sophisticated attack techniques.
Modern threats like ransomware, credential theft, and supply chain attacks use tactics that traditional security tools miss. IDS helps by watching for behavioral patterns associated with these attacks rather than just looking for malicious files.
Ransomware behavior monitoring
Ransomware typically follows predictable patterns even when the malware itself is new. IDS watches for:
- Rapid file modification patterns consistent with encryption
- Network connections to command and control infrastructure
- Attempts to delete shadow copies or backups
- Lateral movement to network shares
- Unusual process behavior like encryption activity from office applications
By detecting these behaviors early, IDS in cyber security can alert you before encryption spreads across your files. The MITRE ATT&CK framework documents adversary techniques like these, helping IDS designers know what to look for.
Threat intelligence integration
Effective IDS leverages external threat intelligence to recognize emerging threats faster.
Threat intelligence feeds provide updated lists of malicious IP addresses, known command and control servers, and indicators of compromise from recent attacks. When your IDS sees a connection attempt to a known malicious server, it can alert or block immediately rather than waiting for behavioral patterns to develop.
The ENISA Threat Landscape 2024 highlights how continuous monitoring and up-to-date threat intelligence have become essential for detecting current attack campaigns.
For home users and small businesses, this means your IDS should receive regular updates from reputable threat intelligence sources, keeping protection current against evolving threats.
Reducing false alarms without missing real threats
One of the biggest challenges with IDS in cyber security is balancing sensitivity against noise.
Too sensitive, and you'll receive constant alerts about harmless activity. Too relaxed, and real threats slip through unnoticed. Finding the right balance requires both smart technology and practical tuning.
Strategies that help:
- Learning periods where the IDS observes your normal activity before aggressive alerting
- Contextual analysis that considers whether unusual activity makes sense for your situation
- Alert prioritization ranking notifications by severity and confidence
- Whitelisting trusted connections and applications to reduce noise
- Correlation connecting multiple weak signals into higher-confidence detections
Machine learning approaches, sometimes called behavioral profiling, build a model of your normal network activity over time. Once the system understands that you regularly connect to specific work servers, video conferencing platforms, and cloud storage, it can focus alerts on genuinely anomalous connections.
| Approach | How It Helps | Consideration |
|---|---|---|
| Learning mode | Establishes baseline before alerting | Requires 1-2 weeks of normal activity |
| Whitelisting | Eliminates known-good traffic from alerts | Must be maintained as legitimate services change |
| Severity scoring | Focuses attention on high-risk alerts | Requires accurate threat classification |
| Alert grouping | Combines related events into single notifications | May delay notification slightly |
The technology behind this adaptive learning helps IDS in cyber security become more useful over time rather than overwhelming you with notifications you'll eventually ignore.
Understanding IDS alerts and taking action
When your IDS detects something suspicious, knowing how to interpret and respond to alerts makes the difference between effective protection and security theater.
IDS alerts should tell you what was detected, why it's suspicious, and what you can do about it. Technical jargon like "TCP SYN flood" or "SMB reconnaissance" doesn't help non-technical users make decisions.
Reading IDS notifications effectively
Clear alerts explain threats in plain language. Instead of "Outbound connection to known C2 infrastructure blocked," a helpful alert says "Blocked connection to a server associated with malware. This suggests a program on your PC may be compromised."
Good IDS implementations provide:
- Threat description in everyday language
- Risk level indicating urgency
- Source showing which program or connection triggered the alert
- Recommended actions specific to the threat
- Context like whether this is part of a larger pattern
For small business owners and home users, you shouldn't need a cyber security degree to understand whether an alert requires immediate action or is informational.
Response options and controls
IDS in cyber security becomes more powerful when it gives you control over how to respond.
Typical response actions include:
- Viewing details about the connection or threat
- Blocking the specific connection or IP address
- Isolating your PC from the network temporarily
- Allowing the connection if you recognize it as legitimate
- Viewing related alerts to understand patterns
Some threats require immediate blocking. Others need investigation before you decide. The IDS should make both paths clear without forcing you into risky decisions under pressure.
Network isolation capabilities prove particularly valuable when you suspect your device is compromised. The ability to disconnect from networks while maintaining access to local files and documentation helps you respond safely.
Understanding how IDS in cyber security works on your Windows devices helps you recognize threats earlier and respond more effectively. Whether you're protecting a small business network, securing devices for remote work, or defending your family's laptops, intrusion detection adds a layer of protection that complements your antivirus and firewall.
Deploying IDS on Windows networks
IDS in cyber security works most effectively when properly deployed and configured for your specific environment.
For Windows 11 users, deployment typically means installing host-based IDS software on each PC or laptop you want to protect. Unlike enterprise network appliances, endpoint IDS runs as software, monitoring that device's network activity regardless of location.
Installation and initial configuration
Setting up IDS shouldn't require networking expertise.
Modern IDS for Windows installs like standard software, then begins monitoring network connections immediately. The initial learning period helps the system understand your normal activity patterns before aggressive alerting begins.
Configuration priorities:
- Ensure the IDS monitors all network interfaces (Wi-Fi, Ethernet, VPN)
- Enable threat intelligence updates for current protection
- Configure alert preferences based on your technical comfort level
- Set up whitelists for known services you use regularly
- Test blocking and isolation features so you know how they work
The MITRE ATT&CK detection strategies provide guidance on mapping detection coverage to adversary techniques, though this level of detail matters more for security teams than individual users.
For traveling users, verify that IDS protection works across different network types. Your laptop should be protected whether you're on hotel Wi-Fi, mobile hotspots, or public networks.
Ongoing maintenance
IDS in cyber security requires minimal ongoing attention if properly configured, but some maintenance keeps protection effective.
Regular updates deliver new threat signatures and detection improvements. These should happen automatically in the background, similar to how Windows Update works. You shouldn't need to manually download and install security updates.
Periodically review your alert history to understand what's being detected. Patterns might reveal security issues with specific applications or websites, helping you make informed decisions about what you use.
Monthly maintenance tasks:
- Review significant alerts you might have missed
- Update whitelists if your regular activities changed
- Verify threat intelligence is updating successfully
- Check that blocking rules are still relevant
- Ensure the IDS is monitoring all active network interfaces
IDS limitations and complementary security
Understanding what IDS in cyber security cannot do helps you build complete protection rather than relying on any single tool.
IDS monitors network activity and system behavior, but it doesn't replace antivirus, patch management, or backup systems. Each security layer addresses different threat vectors.
What IDS doesn't protect against
IDS won't detect malicious files before they're opened or prevent you from downloading infected attachments. That's antivirus territory. IDS also can't patch vulnerable software or fix security misconfigurations on your Windows system.
If an attacker gains physical access to your device, IDS provides limited help. The same applies to social engineering attacks where you're tricked into providing credentials directly to attackers rather than through malware on your device.
Outside IDS scope:
- Malware in files before execution
- Software vulnerabilities and missing patches
- Weak passwords and credential reuse
- Physical security and device theft
- Social engineering and phishing targeting human judgment
- Data loss from hardware failure
This is why effective cyber security uses multiple tools together. Your antivirus catches malicious files, your firewall controls which programs can access the internet, your backup protects against data loss, and IDS watches for suspicious network behavior that other tools miss.
Building layered protection
IDS in cyber security works best as part of a layered defense strategy.
Start with fundamentals: keep Windows and applications updated, use strong unique passwords, enable Windows Defender, and maintain offline backups of important files. These basics address the most common threats.
Add IDS to catch threats that slip past basic defenses. Network-based attacks, command and control traffic, data exfiltration attempts, and lateral movement all show up in network monitoring even when file-based detection fails.
| Security Layer | Primary Purpose | What It Catches | What It Misses |
|---|---|---|---|
| Antivirus | Malicious file detection | Known malware, suspicious files | Zero-day exploits, fileless attacks |
| Firewall | Connection control | Unauthorized inbound connections | Allowed program misbehavior |
| IDS | Behavioral monitoring | Network-based attacks, C2 traffic | Offline threats, physical access |
| Patch management | Vulnerability remediation | Known security flaws | Configuration issues |
| Backup | Data protection | Ransomware recovery, hardware failure | Real-time protection |
For small businesses, consider which layers you can realistically maintain. Better to implement three layers well than five layers poorly.
Privacy considerations with network monitoring
IDS in cyber security necessarily sees your network traffic, raising valid privacy questions about what's collected and where it goes.
Understanding how different IDS implementations handle your data helps you make informed choices about which solutions fit your privacy requirements.
Local versus cloud analysis
Host-based IDS running entirely on your Windows device analyzes traffic locally without sending data externally. This keeps your browsing history, connection details, and network patterns on your device rather than in cloud databases.
Cloud-based IDS or cloud-assisted detection sends network metadata (connection details, domains contacted, traffic patterns) to external servers for analysis. This enables more sophisticated threat detection using global intelligence but requires trusting the vendor with information about your network activity.
Questions to ask IDS vendors:
- Does traffic analysis happen on my device or in the cloud?
- What network data is sent externally, if any?
- How long is data retained?
- Who has access to my network activity information?
- Can I opt out of cloud telemetry while maintaining protection?
For many users, particularly those handling sensitive business information or working in regulated industries, local processing offers better privacy guarantees than cloud-dependent solutions.
Encrypted traffic and privacy
Modern web traffic uses HTTPS encryption, protecting content from network eavesdroppers. This creates a challenge for IDS in cyber security: how do you detect threats in encrypted traffic without breaking encryption?
Effective IDS analyzes connection metadata (who you're talking to, when, how much data) rather than reading message content. An IDS can detect your device connecting to a known malicious server even when the traffic is encrypted, because the destination itself is suspicious regardless of what's being said.
Some enterprise IDS uses SSL/TLS interception, decrypting traffic for inspection then re-encrypting it. This technique raises significant privacy concerns and is generally inappropriate for small business or home use. Host-based IDS on Windows endpoints can see traffic before encryption anyway, making interception unnecessary.
Recent developments in IDS technology
IDS in cyber security continues evolving to address emerging threats and leverage new detection capabilities.
Recent research explores applying machine learning and artificial intelligence to IDS, aiming to improve detection accuracy and reduce false positives. An arXiv paper from December 2024 demonstrates using large language models to automatically label IDS rules with MITRE ATT&CK techniques, helping security teams understand what their detections actually catch.
Machine learning and adaptive detection
Traditional signature-based IDS relies on human experts writing rules for each attack variant. Machine learning approaches train models to recognize attack patterns automatically, potentially detecting threats that human analysts haven't explicitly defined.
Benefits of ML-enhanced IDS:
- Detects variations of known attacks without new signatures
- Identifies subtle correlations across multiple events
- Adapts to evolving attacker techniques automatically
- Reduces manual rule writing and maintenance
Challenges include:
- Requires significant training data
- Can produce opaque decisions that are hard to explain
- May inherit biases from training datasets
- Needs periodic retraining as environments change
For small business and home users, the practical impact is IDS that gets smarter over time and requires less manual tuning to remain effective.
Integration with broader security ecosystems
IDS in cyber security increasingly integrates with other security tools, sharing context and coordinating responses.
When your IDS detects suspicious network activity, it might automatically trigger deeper scans from your antivirus, update firewall rules to block the threat source, or send alerts to security dashboards. This coordination makes security layers work together rather than operating in isolation.
The IEEE survey on intrusion detection systems discusses emerging architectures that combine IDS with security information and event management (SIEM) systems, creating more comprehensive threat visibility particularly in enterprise environments.
For individual users and small businesses, simpler integration might mean IDS alerts appearing in the same interface as your antivirus notifications, making security easier to understand at a glance.
Practical tips for Windows users
Getting the most from IDS in cyber security on your Windows devices requires balancing security with usability.
Start by setting realistic expectations. IDS won't catch every threat, and it will occasionally alert on harmless activity. View it as an additional information source rather than perfect protection.
Pay attention to patterns in alerts rather than reacting to each one individually. If you see repeated connection attempts from the same source, or multiple alerts related to one application, that pattern deserves investigation even if individual alerts seem minor.
Keep a simple log of significant alerts and your responses. This helps you identify recurring issues and provides documentation if you later need to investigate a compromise or seek technical support.
For traveling users:
- Test IDS blocking features on familiar networks before relying on them while traveling
- Understand how to temporarily disable protection if you need to troubleshoot connection issues
- Know how to isolate your device from networks if you suspect compromise
- Verify that VPN connections are also monitored by your IDS
- Consider more aggressive blocking settings when using untrusted public Wi-Fi
For small businesses with multiple Windows devices, maintain consistent IDS configuration across machines. This makes alerts easier to understand and ensures even coverage across your team.
Don't ignore alerts entirely, but also don't panic at every notification. Learn which alert types genuinely require immediate action versus those that are informational. Your IDS should help you distinguish between these categories through clear severity ratings and descriptions.
Understanding IDS in cyber security helps you make informed decisions about network protection for your Windows devices. Intrusion detection complements antivirus and firewall protection by watching network behavior, catching threats that file-based security misses. NetGuardian Pro provides exactly this kind of network intrusion detection for Windows 11 PCs and laptops, with 14 detection modules monitoring Wi-Fi, USB and Bluetooth connections alongside ransomware behavior monitoring, threat intelligence, and clear alerts you can understand and act on without needing IT expertise. If you want practical network protection that travels with your device and helps you understand what's happening on your network, explore NetGuardian Pro today.
Related reading: Network Intrusion Detection Systems for Windows Users, Cyber Security IDS: Protection for Windows Networks.