Network Attacks: How to Detect and Stop Threats in 2026
Network attacks have become more sophisticated and frequent in 2026, targeting everyone from home users to small businesses. These threats exploit vulnerabilities in your internet connection, Wi-Fi network, and connected devices to steal data, install malware, or disrupt your work. Understanding how network attacks work and what you can do to stop them helps you protect your Windows 11 PC, family devices, and business assets without needing an IT degree. This guide explains the most common attack methods, shows you how to spot suspicious activity, and gives you practical steps to strengthen your defences.
What network attacks actually target
Network attacks focus on the pathways that connect your computer to the internet and other devices. Attackers scan for open ports, weak passwords, unpatched software, and misconfigured settings that let them slip past your defences. Once inside your network, they can monitor your traffic, redirect your connections, or move laterally to other devices on the same Wi-Fi network.
The MITRE ATT&CK® Enterprise matrix catalogues hundreds of techniques adversaries use to compromise networks. These range from simple credential theft to complex multi-stage attacks that persist for months.
Home networks often become targets because routers ship with default passwords, firmware updates get ignored, and users assume their antivirus software handles everything. Small businesses face similar risks, especially when employees work from home or connect through public Wi-Fi while travelling.
Common entry points attackers exploit
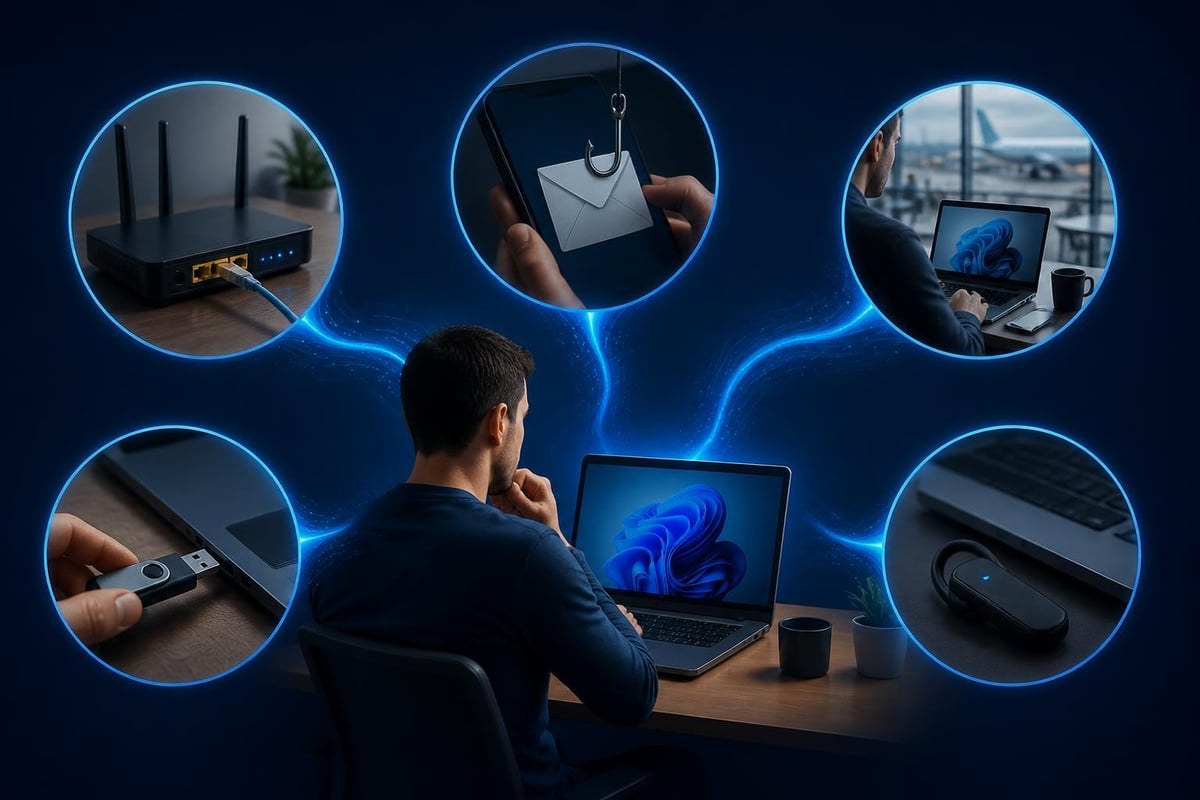
Attackers probe your network through several main channels:
- Weak or default router passwords that let them access your network settings
- Unpatched vulnerabilities in Windows 11 or installed applications
- Phishing emails that trick you into downloading malware or revealing credentials
- Public Wi-Fi networks where traffic interception is straightforward
- USB devices that auto-run malicious code when plugged in
- Bluetooth connections left in discoverable mode
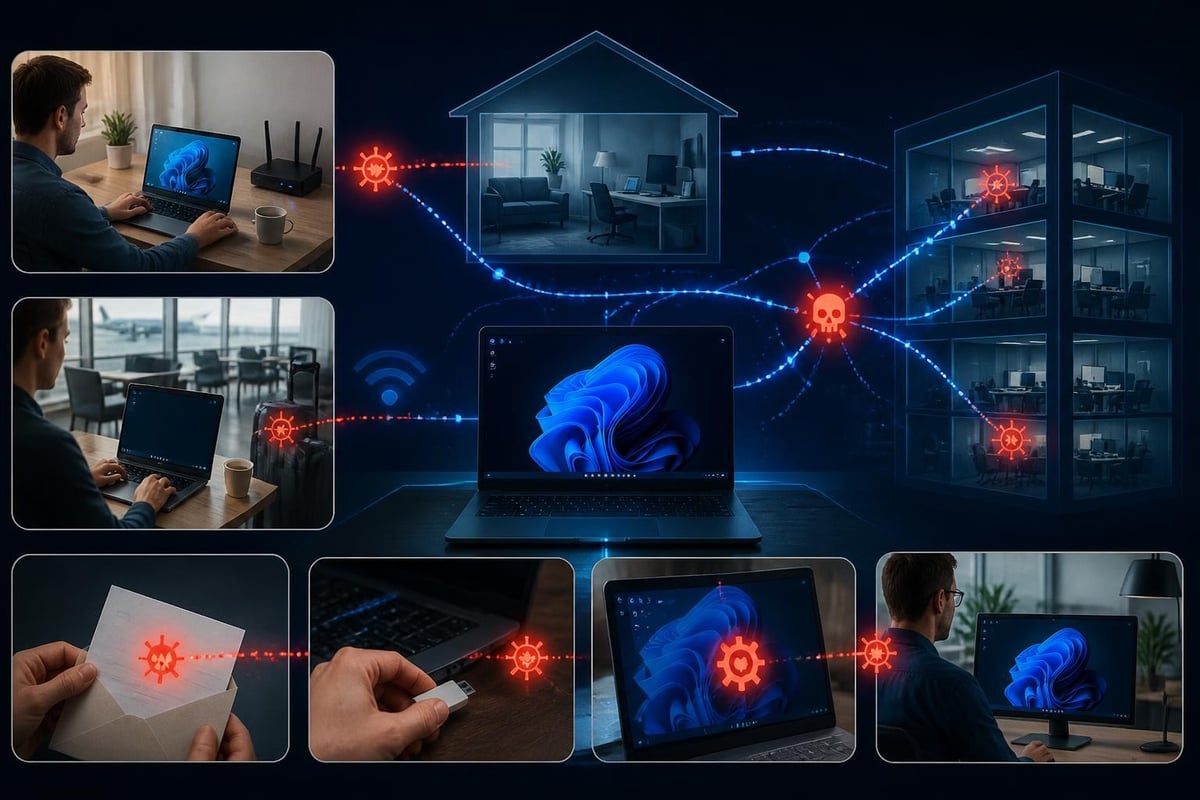
Each entry point offers a different level of access. A compromised router gives attackers control over your entire network. A phishing link might only affect one PC initially, but malware can spread to shared folders and other devices.
The ENISA Threat Landscape 2024 report highlights that availability attacks (including DDoS) and ransomware remain top threats to both businesses and consumers across Europe and beyond.
Types of network attacks you need to know
Understanding the main categories helps you recognise suspicious activity before serious damage occurs. Network attacks generally fall into a few broad types, each with distinct goals and methods.
Denial-of-service and distributed denial-of-service attacks
DoS and DDoS attacks flood your network or device with bogus traffic until legitimate connections can't get through. Your internet slows to a crawl, websites time out, and services become unreachable.
These attacks rarely target individual home users directly. Small businesses, however, face real risk if they host their own servers or rely on always-on connections for point-of-sale systems or remote access.
The Joint CISA/FBI/MS-ISAC Guide on Responding to DDoS Attacks provides coordinated U.S. guidance on detecting and recovering from denial-of-service incidents, useful for small business owners who need practical response steps.
Man-in-the-middle interception
MITM attacks occur when an attacker positions themselves between your device and the server you're trying to reach. They intercept, read, and potentially alter your traffic without you knowing.
Public Wi-Fi networks are prime locations for MITM attacks. An attacker sets up a rogue access point with a convincing name like "Airport_Free_WiFi" and anyone who connects routes their traffic through the attacker's device.
Signs you might be experiencing a MITM attack:
- Browser warnings about invalid security certificates
- Unexpected redirects to unfamiliar login pages
- Slow or intermittent connections on networks that should be fast
- Apps or websites behaving strangely or requesting unusual permissions
Using encrypted connections (HTTPS), verifying certificates, and avoiding public Wi-Fi for sensitive tasks reduces your MITM risk. A VPN encrypts your traffic end-to-end, making interception far less useful to attackers.
Port scanning and network reconnaissance
Before launching an attack, adversaries scan your network to map open ports, identify running services, and fingerprint operating systems. This reconnaissance is quiet and often goes unnoticed.
Port scans aren't attacks themselves but they signal that someone is probing your defences. Legitimate security tools also scan networks, so context matters. Unexpected scans from foreign IP addresses or at unusual hours warrant investigation.
NIST Special Publication 800-115 provides the standard technical guide on network scanning, penetration testing, and assessment methodologies, which helps you understand both offensive scanning techniques and defensive testing.
Malware delivery through network connections
Many network attacks aim to deliver malware. Once malware is installed, it can steal credentials, encrypt files for ransom, spy on your activity, or conscript your PC into a botnet.
Malware spreads through:
- Drive-by downloads from compromised websites
- Email attachments that exploit document vulnerabilities
- Infected USB drives that auto-execute when inserted
- Malicious software updates pushed through compromised servers
- Exploits targeting unpatched Windows 11 vulnerabilities
Ransomware behaviour monitoring watches for suspicious file encryption patterns, mass file modifications, and connections to known command-and-control servers. Detecting these behaviours early lets you isolate the infected device before ransomware spreads across your network.
How to spot network attacks on your Windows 11 PC
Recognising the warning signs early gives you time to respond before attackers achieve their goals. Network attacks leave traces if you know where to look.
Unusual network activity patterns
Your PC communicates constantly, but certain patterns indicate problems. Sudden spikes in network usage when you're not actively downloading or streaming suggest background processes sending or receiving data without your knowledge.
Check your network activity regularly:
| Activity | Normal behaviour | Suspicious behaviour |
|---|---|---|
| Idle traffic | Minimal, occasional updates | Constant high-volume transfers |
| Connection count | 10-20 active connections | 100+ simultaneous connections |
| Unknown processes | System updates, cloud sync | Unfamiliar executables accessing network |
| Outbound traffic | Expected uploads to services you use | Large uploads to unfamiliar foreign servers |
Windows 11 Task Manager shows network usage per application. Press Ctrl+Shift+Esc, click the Performance tab, then Resource Monitor to see which processes connect to which addresses.
Unexpected connection requests and alerts
If Windows Firewall starts blocking connection attempts you don't recognise, pay attention. Legitimate software occasionally triggers alerts, but repeated blocks from the same foreign IP address or unusual ports suggest scanning or attack attempts.
Your router logs also record connection attempts. Most routers let you view these logs through their web interface. Look for:
- Failed login attempts to your router admin panel
- Blocked inbound connections on uncommon ports
- DNS queries to suspicious domains
- Devices you don't recognise appearing on your network
Small businesses should audit their network device list weekly. Unauthorised devices on your Wi-Fi indicate either a security breach or an employee connecting personal devices against policy.
Performance degradation and crashes
Network attacks consume system resources. Your PC might slow down, applications crash unexpectedly, or your internet connection becomes unreliable even though your service provider reports no outages.
DDoS attacks targeting your connection cause timeout errors and make websites unreachable. MITM attacks sometimes introduce latency as traffic routes through the attacker's system. Malware running in the background uses CPU and network bandwidth, degrading performance across the board.
Practical steps to defend against network attacks
You don't need enterprise-grade equipment or a security team to protect yourself. These measures significantly reduce your vulnerability to network attacks.
Strengthen your router and network perimeter
Your router is the first line of defence. Change the default admin password immediately after setup. Use a strong, unique password with at least 16 characters mixing letters, numbers, and symbols.
Essential router security settings:
- Disable WPS (Wi-Fi Protected Setup) – convenient but vulnerable to brute-force attacks
- Enable WPA3 encryption – or WPA2 if your devices don't support WPA3 yet
- Turn off remote management – unless you specifically need it and understand the risks
- Update firmware regularly – manufacturers patch vulnerabilities but updates don't install automatically
- Change your Wi-Fi network name (SSID) – avoid names that identify your router model or address
Hide your SSID only if you're comfortable with the trade-offs. It provides minimal security and breaks some legitimate use cases.
Use a VPN for untrusted networks
Public Wi-Fi at airports, hotels, and cafes is convenient but inherently insecure. Anyone on the same network can potentially intercept your traffic.
A VPN encrypts your connection from your device to the VPN server. Even if an attacker intercepts your traffic on public Wi-Fi, they see only encrypted data they can't read or modify.
Travellers should use a VPN whenever connecting to networks they don't control. The CISA DDoS Guidance for federal agencies emphasises layered protection, and VPNs form one essential layer when working remotely.
Monitor network connections actively
Passive monitoring tools watch your network traffic and alert you to suspicious patterns. This visibility helps you catch attacks during the reconnaissance phase, before real damage occurs.
NetGuardian Pro provides real-time network intrusion detection specifically for Windows 11 PCs and laptops. Its 14 detection modules monitor Wi-Fi, USB, and Bluetooth connections, watching for ransomware behaviour, unauthorised access attempts, and suspicious network activity. Clear alerts explain what's happening in plain language, and blocking controls let you stop threats immediately. The system's Hawk Sense feature learns your normal network patterns over time, helping reduce false alarms while catching genuine threats.
For small businesses, monitoring every device individually becomes tedious. Start with critical systems: your server (if you have one), the PC that handles accounting, and any device that stores customer data.
Segment your network when possible
Network segmentation limits how far an attacker can move after compromising one device. Many modern routers let you create guest networks that isolate visitors from your main devices.
Recommended network segments for small businesses:
- Main network: Work PCs and printers
- Guest network: Visitors and customer Wi-Fi
- IoT network: Smart devices, cameras, thermostats (these often have weak security)
- Admin network: Network management tools (if you have the expertise)
Home users benefit from guest networks too. Put smart TVs, gaming consoles, and IoT devices on the guest network. If malware compromises your smart fridge, it can't reach the PC where you do your banking.
How to divide a network into main work devices, guest access, IoT smart devices and admin management to limit attack spread between segments
Responding when you detect suspicious activity
Detection is only useful if you know what to do next. Quick, calm action minimises damage when you spot signs of network attacks.
Immediate isolation steps
If you believe an attack is in progress, disconnect the affected device from your network. Unplug the Ethernet cable or turn off Wi-Fi. This stops the attacker's access and prevents malware from spreading to other devices.
Don't shut down the PC immediately. Malware sometimes triggers destructive payloads when it detects shutdown. Instead, disconnect network access and then assess the situation.
For businesses, isolating one PC might disrupt work. Weigh the disruption against the risk. If you're unsure whether the alert is genuine, disconnect anyway. False alarms are inconvenient but recoverable. Real attacks spread quickly.
Investigate and document
Once isolated, investigate what triggered the alert. Check which process was making suspicious connections, note the destination IP addresses, and record the time.
Windows Event Viewer logs security events including network connections, firewall blocks, and failed login attempts. Press Win+R, type eventvwr.msc, and review the Security and System logs.
Document everything:
- Time suspicious activity started
- Processes or applications involved
- IP addresses or domains contacted
- Error messages or alerts received
- Actions you've taken so far
This documentation helps you learn from the incident and assists support teams if you need professional help.
Remediation and recovery
If you've confirmed malware or an intrusion, clean the infected system. Run a full scan with your antivirus software. Consider a second opinion scan from a different vendor's tool.
Persistent malware sometimes survives basic scans. If suspicious activity continues after cleaning, backup your personal files and reinstall Windows 11. It's drastic but ensures a clean start.
Post-incident checklist:
- Change all passwords from a known-clean device
- Review connected accounts for unauthorised access
- Update all software and firmware
- Audit your network device list and remove unknowns
- Review and tighten security settings
- Monitor closely for two weeks to ensure the threat is gone
Small businesses should notify customers if client data might have been accessed. Check your local regulations-South Africa's Protection of Personal Information Act and various U.S. state laws mandate breach notifications in certain circumstances.
Staying ahead of evolving network attack techniques
Attackers constantly refine their methods. What works today might fail tomorrow. Staying informed and maintaining good security habits matters more than any single tool.
The SANS 2023 Attack and Threat Report offers practitioner-focused analysis on common attack vectors and detection techniques, giving you insight into trends security professionals see across industries.
Keep your systems updated
Patch Tuesday exists for a reason. Microsoft releases Windows 11 updates monthly, often fixing vulnerabilities actively exploited in network attacks. Enable automatic updates and install them promptly.
Third-party software requires attention too. Adobe, Java, browsers, and productivity tools all ship regular security updates. Unpatched software gives attackers easy entry points.
Your router firmware updates less frequently but matters just as much. Check your manufacturer's support site quarterly for new firmware releases.
Understand your specific risk profile
A home user streaming videos faces different threats than a small business handling customer payment information. An accountant working from a laptop in coffee shops has unique vulnerabilities compared to someone who only uses their PC at home.
Tailor your defences to your situation:
| User type | Primary risks | Priority defences |
|---|---|---|
| Home family | Malware, phishing, IoT device compromise | Router security, network monitoring, VPN for travel |
| Small business | Ransomware, data theft, availability attacks | Network segmentation, monitoring, regular backups, staff training |
| Mobile professional | Public Wi-Fi interception, physical device theft | VPN always-on, full-disk encryption, remote wipe capability |
| Self-employed from home | Credential theft, malware, targeted attacks | Strong passwords, 2FA everywhere, network monitoring, isolation of work devices |
Travellers face elevated risk. Public Wi-Fi and hotel networks see constant attack activity. Use VPN on all untrusted networks, avoid accessing sensitive accounts, and treat hotel networks as hostile by default.
Build security awareness in your household or business
The best monitoring tools can't stop you clicking a phishing link or using "Password123" on your router. Education matters.
For families, teach children that clicking random links or downloading programs without permission creates risk. Explain why you don't use public Wi-Fi without protection.
Small businesses should train staff on basic security: recognising phishing, reporting suspicious emails, not sharing passwords, and locking screens when stepping away.
Make security a shared responsibility, not just the owner's problem. Everyone using the network contributes to its security or vulnerability.
Resources and tools for deeper understanding
Government agencies, research institutions, and security organisations publish valuable guidance on network attacks and defences. These resources go beyond product marketing to explain underlying concepts.
The OWASP Server-Side Request Forgery documentation explains how network-oriented web attacks like SSRF let attackers reach internal services and what mitigations help.
Academic research also offers insight. An IEEE Communications Surveys & Tutorials paper on adversarial machine learning for network intrusion detection reviews how detection systems work and where they might fail. For those interested in how frameworks like MITRE ATT&CK apply to real-world detection, a recent ArXiv survey synthesises research directions and automation approaches.
You don't need to read academic papers to stay safe, but these sources provide the foundation for practical tools and guidance. Understanding the research helps you evaluate vendor claims and make informed decisions.
For home users and small businesses, focus on authoritative, practical sources like CISA, NIST, and SANS. These organisations publish guidance tested in real environments by people who respond to actual incidents.
Explore NetGuardian Pro’s features to see how network monitoring works in practice for Windows 11 users. The site explains each detection module, what threats it addresses, and how alerts appear in plain language.
Building your network security plan for 2026
Network attacks will continue evolving, but the fundamentals remain constant: know what's normal on your network, detect deviations quickly, respond decisively, and learn from each incident.
You don't need perfection. Attackers look for easy targets. Making your network moderately difficult to breach pushes them toward someone else. Combine router security, regular updates, network monitoring, and smart behaviour. Back up your data so ransomware becomes an inconvenience rather than a crisis.
Small businesses should document their security measures and review them quarterly. What worked when you had three employees might not suffice at ten. As you grow, threats grow too.
Home users: protect your network with the same care you'd lock your doors. Your personal information, family photos, financial records, and identity all flow through that Wi-Fi router. Treat it accordingly.
Understanding network attacks and taking practical steps to defend against them protects your data, privacy, and peace of mind in 2026. For Windows 11 users wanting real-time visibility into network connections and clear alerts when threats emerge, NetGuardian Pro provides 14 detection modules that monitor Wi-Fi, USB, and Bluetooth connections, watching for suspicious activity and giving you the controls to respond immediately. With one-time payment, no subscription, and support designed for people without IT backgrounds, it complements your antivirus to strengthen your overall protection.
Related reading: Computer Network Security Threats in 2026, Network Security Threats: What to Spot and How to Respond.