Active Defence: Practical Security for Your Network
Active defence represents a fundamental shift in how you protect your network. Instead of waiting for something bad to happen and then reacting, you take steps to detect threats early, understand what attackers are doing and stop them before they achieve their goals. For home users, small businesses and travellers who rely on Windows devices, this proactive approach makes the difference between catching a threat in time and dealing with ransomware or data theft after the fact.
What active defence actually means
The term "active defence" describes security measures that engage with potential threats rather than simply blocking known bad actors. Traditional antivirus software focuses on recognizing malware signatures. Active defence goes further by monitoring behavior, watching network connections and identifying suspicious patterns that suggest an attack is underway.
Key characteristics include:
- Real-time monitoring of network activity across Wi-Fi, USB and Bluetooth connections
- Behavioral analysis that spots unusual activity even without a known malware signature
- Automated responses that can isolate systems or block connections when threats emerge
- Threat intelligence feeds that provide up-to-date information about current attack campaigns
This approach complements your existing antivirus rather than replacing it. While antivirus handles known malware, active defence catches the novel attacks, suspicious behaviors and network-based threats that signature scanning might miss.
How it differs from passive protection
Passive security tools wait for you to scan files or rely on scheduled checks. They're essential, but they leave gaps. An attacker who gains access between scans has time to move laterally, escalate privileges or encrypt your files.
Active defence fills those gaps by maintaining constant vigilance. Network connections are monitored as they happen. Suspicious processes are flagged immediately. When your laptop connects to an unfamiliar Wi-Fi network at an airport, active defence can warn you about man-in-the-middle attempts or malicious access points before credentials are stolen.
Why small businesses and home users need this approach
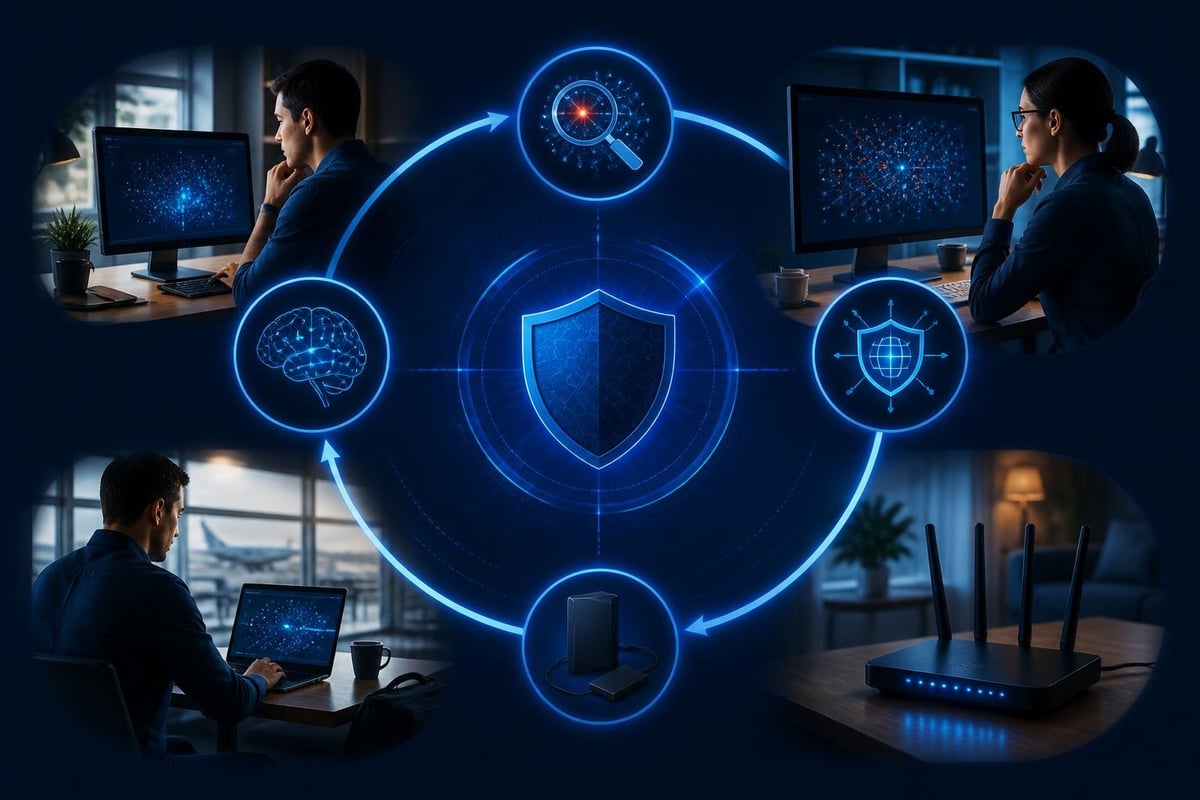
You might think active defence is only for large enterprises with dedicated security teams. That assumption leaves home offices and small businesses vulnerable. Attackers don't just target big companies. They go after whoever has weak defenses and valuable data.
Consider these real-world scenarios:
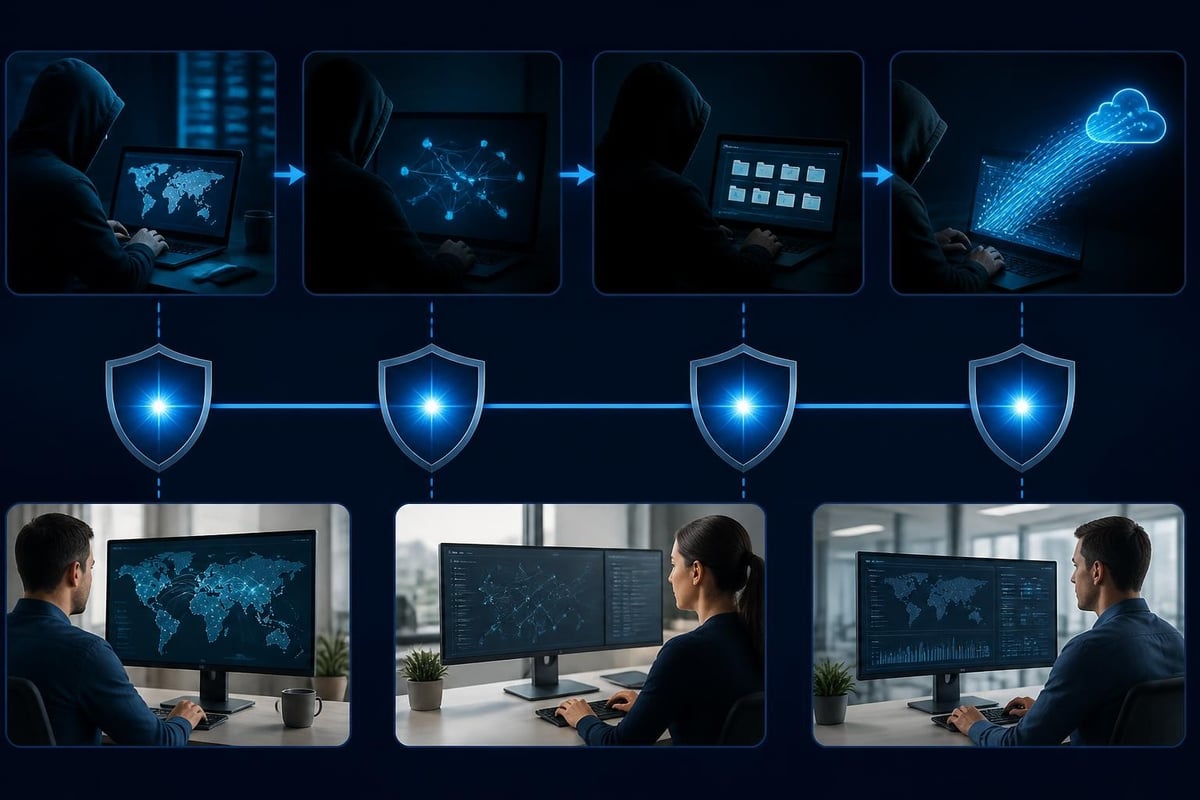
Ransomware deployment: An attacker sends a phishing email with a malicious attachment. Traditional antivirus might catch it if the malware is already catalogued. But if it's a new variant, it slips through. Active defence notices the unusual process behavior, the rapid file encryption pattern and the attempt to contact a command-and-control server. It blocks the connection and isolates the PC before encryption spreads across your network.
USB-based attacks: Someone finds a USB stick in a parking lot and plugs it into their work laptop out of curiosity. Active defence monitoring detects the unexpected executable launch, the attempt to modify system files and the outbound connection to an unfamiliar IP address.
Travel Wi-Fi risks: You connect to hotel Wi-Fi during a business trip. Active defence identifies the network fingerprint, warns about potential eavesdropping and can automatically route your traffic through a VPN to protect your communications.
These aren't hypotheticals. They happen daily to ordinary users who assumed basic antivirus was enough. The MITRE ATT&CK framework documents hundreds of adversary techniques that bypass traditional defenses. Active defence addresses many of these by focusing on attacker behavior rather than just malware signatures.
Core components of an active defence system
Building effective active defence requires several working parts. You don't need to understand every technical detail, but knowing the main components helps you evaluate security tools and make informed decisions.
Network intrusion detection
This monitors all traffic entering and leaving your PC. It looks for patterns associated with port scanning, brute force attacks, data exfiltration and command-and-control communications. When you browse legitimate websites, the traffic looks normal. When malware tries to phone home or an attacker probes your system, the patterns stand out.
What to look for:
- Monitoring across all connection types (Wi-Fi, Ethernet, USB tethering, Bluetooth)
- Integration with current threat intelligence feeds
- Clear alerts that explain what was detected and why it matters
- Options to block suspicious connections manually or automatically
Behavioral analysis
Ransomware behavior monitoring watches how programs interact with your files. Legitimate applications open files one at a time for specific purposes. Ransomware opens hundreds or thousands of files rapidly, encrypting each one. This distinctive pattern allows detection even when the specific malware variant has never been seen before.
Similarly, behavioral analysis can spot privilege escalation attempts, unusual registry modifications and processes that inject code into other programs. These techniques appear across different attacks, making behavior-based detection more resilient than signature matching.
| Traditional Detection | Behavioral Detection |
|---|---|
| Matches known malware signatures | Identifies suspicious activity patterns |
| Requires regular database updates | Learns normal baseline behavior |
| Misses zero-day threats | Catches novel attack techniques |
| Low false positive rate | Requires tuning to reduce false alarms |
| Fast scanning with minimal CPU use | More resource intensive |
Adaptive learning
False alarms undermine security. If you receive constant warnings about legitimate activity, you'll start ignoring alerts or disabling protection altogether. This is where adaptive learning becomes crucial.
Systems like Hawk Sense observe your normal patterns. They learn which applications you use regularly, which websites you visit and what network connections are typical for your environment. Over time, the system becomes better at distinguishing real threats from routine activity, reducing unnecessary alerts while maintaining vigilance against genuine risks.
Implementing active defence without an IT team
You don't need technical expertise to benefit from active defence. The key is choosing tools designed for everyday users rather than enterprise security teams. Look for software that provides clear explanations, straightforward controls and sensible defaults.
Practical setup steps
Start with these priorities:
Install network monitoring on every Windows PC and laptop: This includes home computers, business workstations and devices that travel. Consistent protection across all endpoints prevents attackers from targeting the weakest link.
Enable ransomware behavior monitoring: Make sure this runs continuously in the background. Check that it monitors document folders, desktop, downloads and any network drives or external storage you use regularly.
Connect to threat intelligence services: Many active defence tools include threat feeds that provide real-time updates about new attack campaigns, malicious IP addresses and emerging techniques. Enable these to benefit from global threat visibility.
Configure VPN for travel: When you work from cafes, airports or hotels, encrypted connections prevent eavesdropping and man-in-the-middle attacks. Built-in VPN options are simpler than managing separate services.
Review alerts weekly: Set aside time to check recent detections. This helps you understand what threats were blocked and identify patterns that might indicate a persistent threat or configuration issue.
Balancing security and usability
Active defence introduces some friction. You might receive alerts about unfamiliar connections or need to approve legitimate activities that look unusual. Finding the right balance takes a few weeks as the system learns your patterns.
Tips for smooth operation:
- Don't ignore all alerts just because some are false positives
- Keep brief notes about recurring false alarms so you can whitelist them if needed
- Update your security software regularly to benefit from improved detection logic
- Test your setup by checking that normal activities (browsing, email, video calls) work without constant interruptions
The 2024 ENISA report highlights the importance of combining technical controls with user awareness. Active defence gives you the tools, but understanding basic security principles helps you make better decisions when alerts appear.
Legal and policy considerations
Active defence raises questions about the legal boundaries of defensive actions. In some contexts, the term includes offensive countermeasures like hacking back against attackers. That's not what we're discussing here and it's generally illegal for individuals and businesses.
The active defence we're describing stays firmly within legal bounds. You monitor your own network, block incoming threats to your systems and gather evidence of attacks against your infrastructure. You don't access attacker systems, launch denial-of-service attacks or take any action beyond protecting your own assets.
The Congressional Research Service report from November 2024 clarifies U.S. policy on active cyber operations. Government agencies operate under different authorities than private citizens. For home users and small businesses, stick to monitoring, detection, blocking and isolation. Leave offensive operations to law enforcement.
Measuring effectiveness
How do you know if your active defence approach is working? Unlike antivirus software that reports "threats blocked" with specific counts, behavioral and network monitoring generates different metrics.
Key indicators to track
| Metric | What it tells you | Target range |
|---|---|---|
| Blocked connection attempts | External threats stopped before data exchange | 5-20 per week for typical users |
| Behavioral alerts | Suspicious process activity detected | 1-3 per week after tuning period |
| False positive rate | Alerts about legitimate activity | Below 10% after first month |
| Mean time to alert | How quickly threats are identified | Under 60 seconds |
| System performance impact | CPU and memory overhead | Below 5% on modern systems |
Research like the SANS whitepaper on validating MITRE Engage effectiveness provides empirical data about active defence performance. The findings consistently show that proactive monitoring catches threats that evade signature-based detection, with typical improvements of 40-60% in detection of novel attack techniques.
For home users and small businesses, the most meaningful metric is simpler: Have you avoided infections, data loss or system compromises? Active defence reduces those incidents by catching threats early in the attack chain before damage occurs.
Active defence for travelers
Business travelers and digital nomads face heightened risks. Public Wi-Fi networks, unfamiliar locations and varied connection environments create opportunities for attackers. Active defence becomes especially valuable when you can't control the network you're joining.
Travel-specific protections include:
- Automatic VPN activation on unfamiliar networks
- Detection of rogue access points and man-in-the-middle attempts
- Bluetooth monitoring to catch unauthorized pairing attempts
- USB connection analysis to prevent juice jacking and malicious peripherals
- Alerts about geolocation-specific threats based on threat intelligence
When you land in a new city and connect to airport Wi-Fi, your active defence system should automatically assess the network, warn about risks and encrypt your traffic. When you plug in your phone to charge at a public USB port, monitoring should verify that only power flows over the connection, not data.
These protections work seamlessly in the background. You don't need to remember security checklists or manually configure settings for each location. The system adapts to changing conditions and maintains protection wherever you work.
Building defense in depth
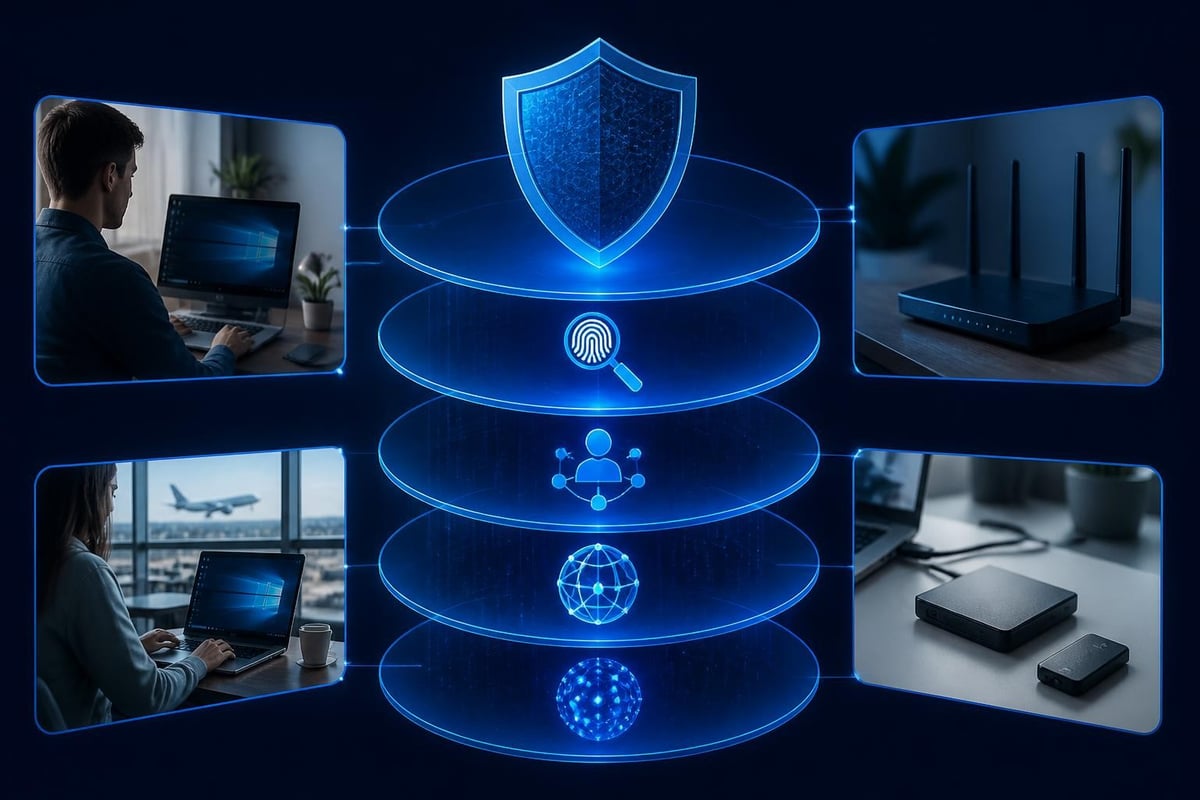
Active defence isn't a replacement for other security measures. It's one layer in a comprehensive approach. You still need antivirus software, regular updates, strong passwords and backup systems.
Your security stack should include:
- Traditional antivirus for signature-based malware detection
- Active network and behavioral monitoring for threats that evade signatures
- Regular Windows updates to patch vulnerabilities
- Strong, unique passwords stored in a password manager
- Automated backups to external storage or cloud services
- User awareness about phishing, social engineering and safe browsing
Each layer addresses different threats and failure modes. Antivirus catches known malware. Active defence spots suspicious behavior. Updates close security holes. Backups provide recovery if all else fails. Combined, they create resilient protection that doesn't depend on any single technology working perfectly.
For businesses working across different regions, consider that security resources are available in multiple languages. Whether you need information in English, Spanish, French or Portuguese, accessing guidance in your preferred language helps ensure you understand the protections you're deploying.
Common questions about active defence
Does active defence slow down my computer?
Modern systems running on Windows 11 with adequate RAM handle active monitoring with minimal performance impact. You might notice a 2-5% increase in CPU usage during heavy network activity, but normal browsing, office work and streaming remain unaffected. The protection value far outweighs the small resource cost.
Will I get bombarded with alerts?
Initially, you may see more notifications as the system establishes baseline behavior. After the first few weeks, adaptive learning reduces false positives significantly. You'll primarily receive alerts about genuine suspicious activity that warrants your attention.
Can active defence protect multiple computers?
Network-level active defence installed on a router can monitor all devices, but endpoint protection on each Windows PC provides deeper visibility into process behavior, file access patterns and application activity. For best results, protect each computer individually.
What happens if I ignore an alert?
The threat doesn't disappear. If you dismiss a warning about a blocked connection, the block remains in place and the threat can't proceed. However, understanding what was detected helps you recognize ongoing attack patterns and take additional steps if needed, such as changing passwords or updating software.
Is this the same as a firewall?
Firewalls control which connections are allowed based on rules about ports and applications. Active defence includes firewall functionality but adds behavioral analysis, threat intelligence and adaptive learning. Think of it as a firewall with intelligence and awareness.
Cost considerations and value proposition
Traditional security subscriptions create ongoing expenses that add up over time. Three years of antivirus subscriptions for a family with four devices can easily exceed several hundred dollars. Small businesses with a dozen computers face even higher recurring costs.
Active defence solutions that charge once and include free updates change this calculation. You pay upfront and receive ongoing protection without annual renewals. For budget-conscious homes and businesses, this model provides predictable costs and long-term value.
Compare total three-year costs:
| Approach | Year 1 | Year 2 | Year 3 | Total |
|---|---|---|---|---|
| Subscription security suite (per device) | £45 | £45 | £45 | £135 |
| One-time active defence (per device) | £60 | £0 | £0 | £60 |
| Family with 4 devices (subscription) | £180 | £180 | £180 | £540 |
| Family with 4 devices (one-time) | £240 | £0 | £0 | £240 |
Beyond direct costs, consider the value of avoiding security incidents. Ransomware recovery, data breach notification and system rebuilding consume time and money. Active defence that prevents these incidents provides ROI that's difficult to quantify but very real when you avoid even a single serious compromise.
Active defence gives you control over your network security through real-time monitoring, behavioral detection and automated threat response. Whether you're protecting a home office, managing devices for a small business or securing a laptop for international travel, this proactive approach catches threats that traditional antivirus misses. NetGuardian Pro delivers these active defence capabilities specifically for Windows 11 users, with 14 detection modules monitoring Wi-Fi, USB and Bluetooth connections, ransomware behavior analysis, threat intelligence and a built-in VPN for travel, all available with a one-time payment and no ongoing subscription.
Related reading: Active Defense: What It Means for Your Network Security, Network Security Solutions for Practical Protection, Protection Secure: Practical Windows Network Security.