Detection of Malware: A Guide for Windows 11 Users
Malware continues to evolve in 2026, targeting Windows 11 users through increasingly sophisticated methods. Whether you're working from home, running a small business, or travelling with your laptop, understanding how detection of malware works helps you make informed security decisions. This guide explains the core detection methods, how they complement each other, and what you should look for when protecting your PC and network.
How signature-based detection identifies known threats
Signature-based detection remains the foundation of most malware identification. This method works by comparing files against a database of known malware signatures. Each signature is a unique fingerprint that identifies a specific malware variant.
When you scan a file, the detection software calculates its hash value and checks it against millions of known malicious hashes. If there's a match, the file is flagged immediately. This approach is fast and reliable for known threats.
Key advantages of signature-based detection:
- Extremely low false positive rate
- Fast scanning with minimal system impact
- Effective against previously documented malware families
- Works well offline once signatures are updated
The main limitation is simple: signature-based detection can't identify brand-new malware variants. Attackers constantly modify their code to evade these fingerprints. That's why detection of malware requires multiple complementary approaches.
Why signature databases need constant updates
Malware authors release thousands of new variants daily. Your detection system needs fresh signatures to recognize these threats. Most antivirus tools update their databases several times per day.
For home users and small businesses, automatic updates are essential. A database that's even a few days old may miss current threats circulating in South Africa or the United States.
Behavioral detection monitors what programs actually do
Behavioral detection takes a different approach. Instead of looking for known signatures, it watches how programs behave. If a program starts encrypting files rapidly, contacts suspicious remote servers, or tries to disable security software, behavioral detection raises an alert.
This method catches zero-day malware that has never been seen before. According to ENISA’s Threat Landscape 2024, behavioral indicators help identify ransomware and advanced persistent threats before they cause damage.
| Detection Method | What It Monitors | Best For |
|---|---|---|
| Signature-based | File hashes and patterns | Known malware variants |
| Behavioral | Program actions and system calls | Zero-day and polymorphic threats |
| Network-based | Connection patterns and traffic | Command-and-control communication |
| Heuristic | Code structure and logic | Variants of known families |
Behavioral detection can generate false positives when legitimate software exhibits unusual but benign behavior. Modern systems use machine learning to reduce these false alarms by learning what's normal for your environment.
Ransomware behavior monitoring in practice
Ransomware has distinct behavioral patterns. It typically:
- Enumerates network shares and mapped drives
- Begins rapid file encryption across multiple directories
- Deletes volume shadow copies to prevent recovery
- Displays a ransom note after encryption completes
Detection systems that monitor these behaviors can catch ransomware during the early stages. The CISA StopRansomware Guide provides detailed guidance on detecting precursor malware activity and suspicious network connections that often signal an impending ransomware attack.
For Windows 11 users, behavioral monitoring runs continuously in the background. When it detects suspicious activity, you receive an alert explaining what the program tried to do and why it was blocked.
Network-level detection catches command-and-control traffic
Malware rarely works in isolation. Most variants communicate with command-and-control servers to receive instructions, exfiltrate data, or download additional payloads. Detection of malware at the network level identifies these suspicious connections before damage occurs.
Network detection systems monitor your Wi-Fi, Ethernet, USB tethering, and even Bluetooth connections. They look for:
- Connections to known malicious IP addresses and domains listed in threat intelligence feeds
- Unusual outbound traffic patterns such as large data transfers to unfamiliar locations
- Protocol anomalies that indicate tunneling or covert channels
- Domain generation algorithm (DGA) activity where malware generates random domain names to find its control server
NetGuardian Pro takes a network-first approach, running 14 detection modules directly on your Windows 11 PC to monitor all network activity. It complements your existing antivirus by watching what happens on your connections, providing clear alerts when suspicious activity is detected, and giving you blocking controls to prevent unauthorized access.
This approach is particularly valuable for small businesses and travellers. When you're on public Wi-Fi at a coffee shop or hotel, network monitoring helps detect man-in-the-middle attacks and malicious access points.
Heuristic analysis examines code structure and logic
Heuristic detection sits between signature-based and behavioral methods. It analyzes the structure, logic, and characteristics of code to identify potentially malicious files, even without an exact signature match.
A heuristic engine might flag a file that:
- Contains obfuscated code designed to hide its purpose
- Includes functions commonly used for keylogging or screen capture
- Attempts to modify system files or registry keys in suspicious ways
- Exhibits packing or encryption patterns typical of malware
The MITRE ATT&CK detection strategies provide a comprehensive framework for mapping detection techniques to adversary tactics and techniques. These strategies help structure heuristic rules to catch specific attack patterns.
Static versus dynamic heuristic analysis
Static heuristic analysis examines files without executing them. It's safe and fast, but limited in what it can discover. Malware that unpacks itself at runtime may hide its true behavior.
Dynamic heuristic analysis runs suspicious files in a sandbox environment and watches what they do. This catches more sophisticated threats but requires more system resources and time.
VirusTotal’s documentation explains how multi-engine scanning combines static and dynamic analysis from dozens of security vendors, along with behavioral metadata and community-contributed detection rules.
Machine learning enhances modern malware detection
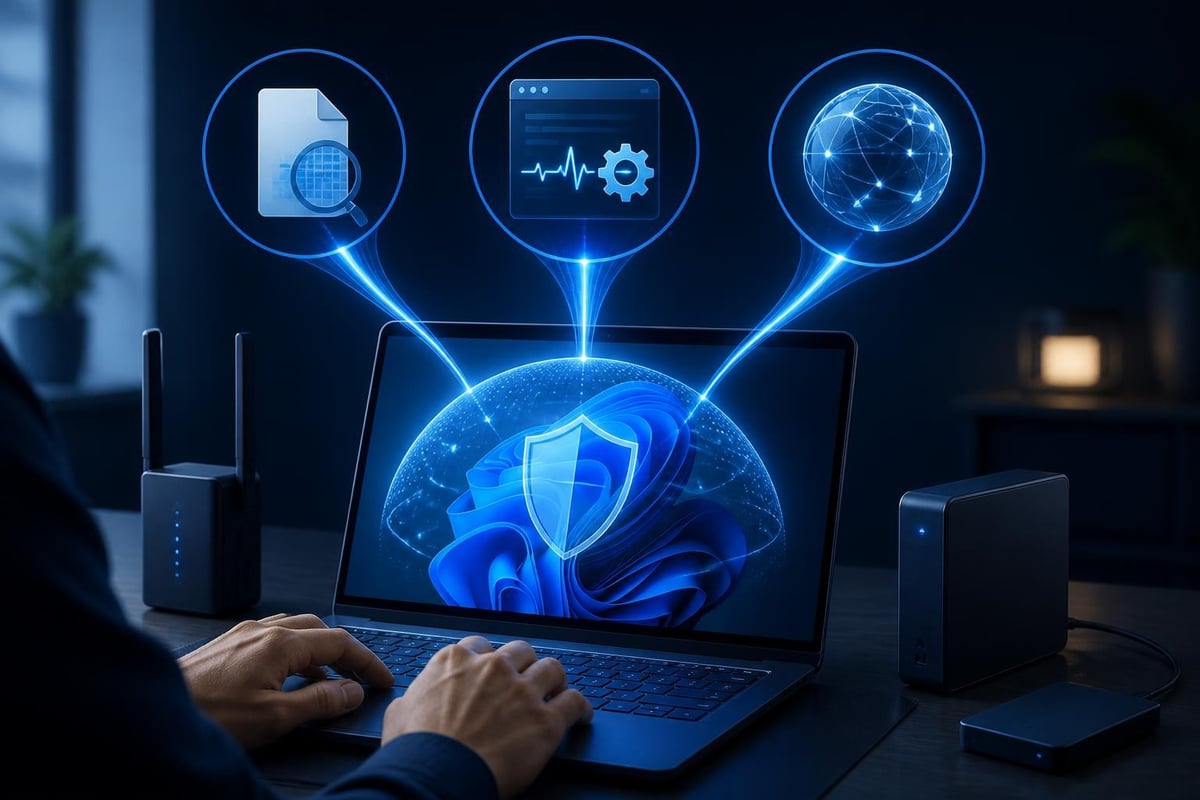
Machine learning has transformed detection of malware in recent years. Instead of relying solely on hand-written rules, ML models learn to distinguish malicious from benign software by analyzing millions of samples.
A recent survey of malware detection using deep learning published in 2024 covers current ML approaches, from traditional feature engineering to deep neural networks. These models examine file characteristics, API call sequences, network traffic patterns, and system behavior.
Common machine learning approaches for malware detection:
- Random forests that classify files based on extracted features like import tables, section characteristics, and string patterns
- Neural networks that process raw bytes or assembly instructions directly
- Graph-based models that represent malware behavior as graphs of system calls and process relationships
- Recurrent networks that analyze sequences of events over time
For home users and small businesses, the practical benefit is fewer false positives. ML models trained on your specific environment learn what's normal for your network and PC usage patterns, reducing unnecessary alerts.
The role of explainability in detection
Understanding why a file was flagged as malicious matters. According to recent research on graph learning and explainability published in early 2025, making detection decisions transparent helps security teams validate alerts and improve their detection rules.
For non-technical users, this means receiving alerts that explain what happened. Instead of a cryptic "threat detected" message, you should see details like "blocked connection to suspicious domain" or "program attempted to encrypt system files."
Threat intelligence feeds provide real-time context
Threat intelligence transforms detection from a local activity into a global effort. When malware is discovered anywhere in the world, threat intelligence feeds distribute indicators of compromise (IOCs) to protection systems globally.
These feeds include:
- IP addresses and domains associated with command-and-control infrastructure
- File hashes of known malicious samples and their variants
- Attack patterns and techniques observed in recent campaigns
- Vulnerability information about exploits actively being used
For Windows 11 users in South Africa and the United States, threat intelligence ensures your detection systems know about regional threats quickly. If a new banking trojan is targeting South African financial institutions, your protection receives updated IOCs within hours.
The NIST guidance on detection and analysis workflows published in 2025 provides frameworks for incorporating threat intelligence into detection processes, helping organizations structure their response to emerging threats.
How detection methods work together
No single detection method is perfect. The most effective approach combines multiple techniques into layers of defense. When signature-based detection misses a zero-day threat, behavioral monitoring may catch it. When behavioral detection generates a false positive, network monitoring can provide context.
Consider this scenario: A user downloads an infected document attached to a phishing email. Here's how layered detection responds:
Layer 1 – Signature scanning: Checks the file hash against known malware. If it's a brand-new variant, this check passes.
Layer 2 – Heuristic analysis: Examines the document for suspicious macros or embedded scripts. May flag it based on code structure.
Layer 3 – Behavioral monitoring: Watches when the document opens. If it attempts to download a payload or execute unexpected code, it's blocked.
Layer 4 – Network detection: If the payload tries to contact a command-and-control server, the connection is identified and prevented.
This defense-in-depth approach ensures that even sophisticated malware faces multiple obstacles.
Reducing false positives with contextual learning
False positives frustrate users and waste time. Advanced detection systems use contextual learning to understand your normal activity patterns. If you regularly transfer large files to a cloud backup service, the system learns this is legitimate, not data exfiltration.
This approach, sometimes called "adaptive detection" or "baseline learning," is particularly valuable for small businesses where the same users perform similar tasks daily. The system builds a model of normal behavior and only alerts when significant deviations occur.
Practical detection for home users and small businesses
For most people, detection of malware should be automatic and understandable. You need protection that works without requiring an IT degree to configure or interpret.
Key features to look for in malware detection:
- Clear, actionable alerts that explain what was detected and why
- Automatic updates for signatures and threat intelligence
- Low system impact so your PC remains responsive
- Blocking controls that let you stop threats immediately
- Compatibility with your existing antivirus software
Windows 11 includes built-in protections like Windows Defender, which provides signature-based and behavioral detection. However, network-level threats often operate outside the scope of traditional antivirus, making additional network monitoring valuable.
When travelling for work or leisure, your detection needs change. Public Wi-Fi networks may be malicious or compromised. USB charging stations can deliver malware. Hotel networks might have infected devices. Network-focused detection becomes essential in these scenarios.
Understanding detection alerts and taking action
When you receive a malware detection alert, you should immediately know:
- What was detected (file, connection, or behavior)
- Why it was flagged as suspicious
- What action was taken automatically
- What you should do next
Good detection systems provide this context without technical jargon. You shouldn't need to Google error codes or interpret hexadecimal addresses.
Detection limitations and realistic expectations
Even the best detection systems have limitations. New malware variants emerge constantly. Attackers specifically test their code against popular security tools to ensure it evades detection. Some threats use legitimate system tools and processes, making detection challenging.
Common detection challenges:
- Fileless malware that operates entirely in memory without dropping traditional executables
- Living-off-the-land attacks that use built-in Windows tools like PowerShell for malicious purposes
- Supply chain compromises where legitimate software is infected before distribution
- Encrypted traffic that hides malicious payloads from network inspection
Understanding these limitations helps you maintain realistic expectations. Detection of malware is not perfect, which is why you need multiple security layers, including regular backups, software updates, and cautious computing habits.
The role of user awareness in detection
Automated detection handles most threats, but user awareness remains important. If you receive an alert about a program you just installed, you can provide context. If your detection system flags unusual network activity during hours when no one is using the computer, you know to investigate.
For small business owners, training staff to recognize and report suspicious activity complements automated detection. When someone receives an unexpected alert, they should know whether to allow, block, or seek help.
Detection of malware requires multiple complementary methods working together to identify threats at different stages and locations. Whether you're a home user, small business owner, or frequent traveller, understanding these detection approaches helps you choose appropriate protection and respond effectively to alerts. NetGuardian Pro monitors your Windows 11 network connections in real-time with 14 detection modules, providing clear alerts about suspicious activity on your Wi-Fi, USB, and Bluetooth connections. It complements your existing antivirus with network-level detection and gives you the visibility and control to protect your PC at home and while travelling.
Related reading: Network Intrusion Detection Systems for Windows Users, Intrusion and Detection for Windows 11 Networks, Strong Passwords, Password Manager: A Windows User’s Guide.