Network Security and Monitoring for Modern Systems
Modern organizations face an escalating challenge as cyber threats grow more sophisticated and persistent. Network security and monitoring have become inseparable disciplines, working together to protect digital assets, detect intrusions, and maintain operational continuity. Understanding how to implement effective monitoring strategies alongside robust security controls determines whether businesses can defend against attacks or become the next breach headline. This comprehensive guide explores the essential components, methodologies, and practical approaches to building a resilient security posture.
Understanding the Fundamentals of Network Security and Monitoring
Network security encompasses the policies, practices, and technologies designed to protect network infrastructure and data from unauthorized access, misuse, or theft. Monitoring serves as the vigilant watchdog, continuously observing network activity to detect anomalies, policy violations, and potential security incidents before they escalate into full-scale breaches.
The relationship between these disciplines creates a defense-in-depth strategy. Security controls establish protective barriers, while monitoring validates their effectiveness and identifies when those barriers face compromise. Together, they form a feedback loop where observations inform policy adjustments and new controls address discovered vulnerabilities.
Core Components of Effective Network Monitoring
Traffic analysis forms the foundation of network visibility. By examining packet flows, protocols, and communication patterns, security teams gain insights into normal operations and quickly spot deviations that signal trouble.
Key monitoring elements include:
- Flow data collection using NetFlow, sFlow, or IPFIX protocols
- Packet capture for deep inspection of suspicious communications
- Log aggregation from firewalls, routers, switches, and endpoints
- Behavioral analytics that establish baselines and flag anomalies
- Threat intelligence integration to correlate observations with known attack patterns
The IETF RFC 9232 framework provides standardized approaches for collecting network telemetry across modern infrastructure. These standards ensure interoperability between monitoring tools and network devices, enabling comprehensive visibility regardless of vendor diversity.
Implementing Continuous Security Monitoring
Continuous monitoring transforms security from a periodic audit into an ongoing operational function. Rather than checking defenses quarterly or annually, organizations maintain persistent awareness of their security posture, detecting and responding to threats in real-time.
Building a Monitoring Architecture
Sensor placement determines what your monitoring systems can observe. Strategic positioning at network perimeters, between network segments, and on critical assets ensures comprehensive coverage without creating blind spots where attackers can operate undetected.
Modern architectures typically include:
- Perimeter sensors monitoring traffic entering and leaving the network
- Internal sensors watching east-west traffic between systems
- Endpoint agents providing host-level visibility
- Cloud monitoring tools for hybrid and multi-cloud environments
- Application performance monitoring tracking business-critical services
| Monitoring Layer | Primary Function | Key Metrics |
|---|---|---|
| Network Edge | External threat detection | Inbound connections, blocked attempts, geographic sources |
| Internal Segments | Lateral movement detection | Inter-segment traffic, privilege escalation, data transfers |
| Endpoints | Host-based threats | Process behavior, file changes, registry modifications |
| Applications | Business logic attacks | Authentication failures, input validation, API abuse |
The CISA guidance on logging emphasizes the importance of comprehensive log collection across all layers for effective incident response and forensic analysis.
Establishing Baselines and Detecting Anomalies
Behavioral baselines define what normal looks like for your network. Machine learning algorithms analyze historical data to understand typical traffic volumes, communication patterns, user behaviors, and application activities. Deviations from these baselines trigger alerts for security investigation.
Effective baseline establishment requires sufficient observation periods. Organizations should collect at least 30 days of data across representative business cycles to account for daily, weekly, and monthly variations in activity patterns.
Advanced systems employ self-learning algorithms that continuously update baselines as legitimate business operations evolve. This adaptive approach reduces false positives while maintaining sensitivity to genuine threats. For Windows environments specifically, monitoring normal process behaviors, network connections, and registry activities creates a behavioral fingerprint that highlights malicious deviations.
NetGuardian Pro exemplifies this self-learning approach by observing how your Windows PC normally operates and flagging unusual activity with plain-language alerts that don't require technical expertise to understand or act upon.
Threat Detection Strategies and Methodologies
Network security and monitoring effectiveness depends heavily on detection methodologies. Organizations combine multiple approaches to maximize threat discovery while minimizing analyst fatigue from excessive false positives.
Signature-Based Detection
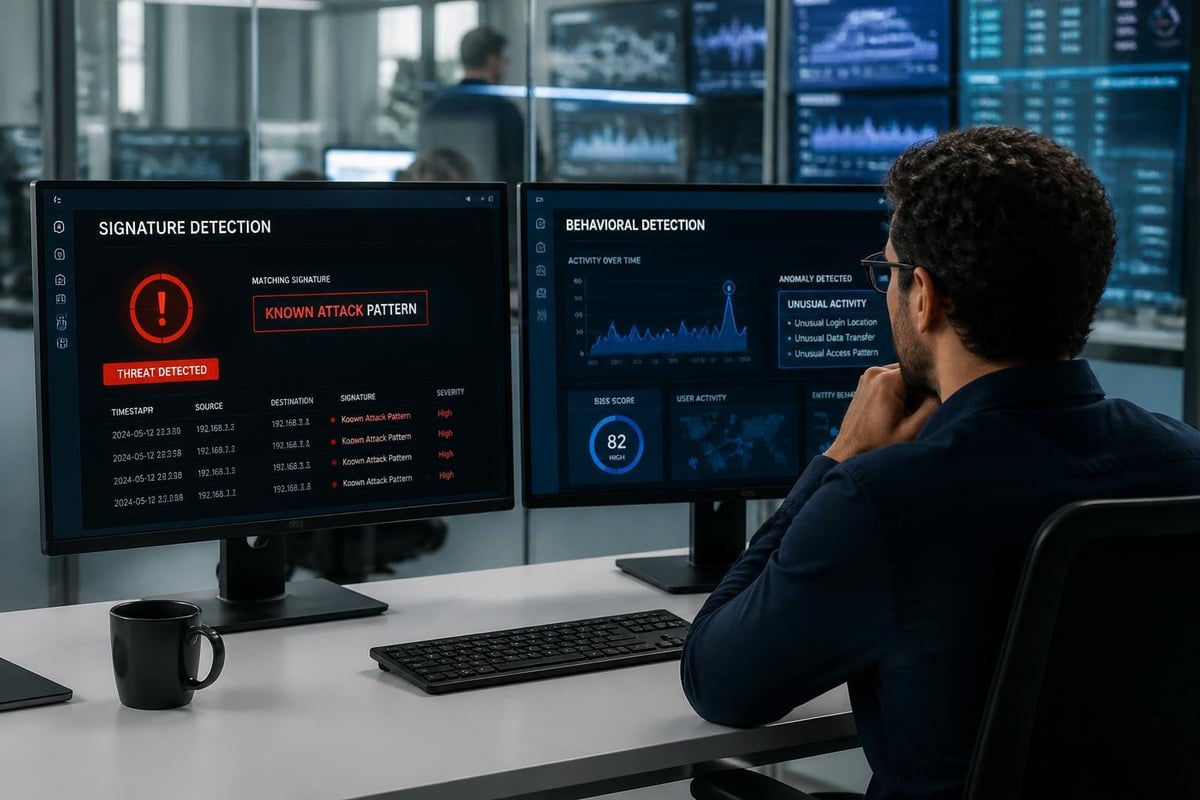
Signature-based systems compare observed traffic against databases of known attack patterns. This approach excels at identifying established threats with documented indicators of compromise (IOCs). Firewalls, intrusion detection systems, and antivirus solutions rely heavily on signature matching for rapid threat identification.
However, signature-based detection faces limitations:
- Zero-day exploits lack signatures until after discovery
- Attackers easily modify malware to evade known signatures
- Signature databases require constant updates to remain effective
- Polymorphic threats change appearance with each infection
Behavioral and Anomaly-Based Detection
Anomaly detection identifies threats based on deviations from established norms rather than matching known patterns. This approach discovers novel attacks, insider threats, and sophisticated adversaries who evade signature-based controls.
The MITRE ATT&CK framework provides structured knowledge about adversary tactics and techniques, enabling organizations to design detection analytics that identify attacker behaviors regardless of specific tools or malware variants used.
Key behavioral indicators include:
- Unusual authentication patterns or credential usage
- Unexpected network connections to external destinations
- Abnormal data transfer volumes or directions
- Process execution chains that deviate from normal application behavior
- Privilege escalation attempts or lateral movement between systems
Combining Detection Approaches
Hybrid detection strategies leverage both signature and behavioral methods to maximize coverage. Signatures provide rapid identification of known threats with minimal false positives, while behavioral analytics discover novel attacks that signatures miss.
Organizations often implement tiered detection:
- First tier: Signature-based filtering removes known threats automatically
- Second tier: Statistical anomaly detection flags unusual patterns for review
- Third tier: Advanced behavioral analytics identify sophisticated attack campaigns
- Fourth tier: Threat hunting teams proactively search for hidden adversaries
This layered approach balances automated efficiency with human expertise, ensuring both rapid response to common threats and deep investigation of complex incidents.
Log Management and Analysis for Security Operations
Centralized log management serves as the foundation for effective network security and monitoring. Logs from firewalls, routers, servers, applications, and endpoints provide the raw data that security teams analyze to detect incidents, investigate breaches, and demonstrate compliance.
Designing a Log Collection Strategy
The NIST SP 800-92 guidance provides comprehensive recommendations for log management planning, including what to collect, how long to retain data, and how to protect log integrity from tampering.
Critical considerations include:
- Scope: Which systems and applications generate security-relevant logs
- Granularity: The level of detail captured in each log entry
- Volume: Storage capacity and network bandwidth for log transmission
- Retention: How long logs remain available for analysis and compliance
- Protection: Securing logs against unauthorized modification or deletion
| Log Source | Key Information | Retention Period |
|---|---|---|
| Firewalls | Connection attempts, blocks, rule matches | 90-365 days |
| Authentication Systems | Login attempts, failures, privilege changes | 1-7 years |
| Network Devices | Configuration changes, interface status | 30-90 days |
| Endpoints | Process execution, file modifications | 30-180 days |
| Applications | Transactions, errors, security events | 90-365 days |
Correlation and Analysis Techniques
Security Information and Event Management (SIEM) platforms aggregate logs from diverse sources, normalize data formats, and apply correlation rules that identify patterns spanning multiple systems. A single failed login might be unremarkable, but 1,000 failed logins across different accounts within minutes indicates a credential-stuffing attack.
Effective correlation requires:
- Time synchronization across all log sources using NTP
- Data normalization converting vendor-specific formats to common schemas
- Contextual enrichment adding threat intelligence, asset criticality, and user information
- Rule optimization balancing detection sensitivity against false positive rates
Advanced analytics increasingly incorporate machine learning models that identify subtle attack patterns humans might overlook. These models excel at detecting insider threats, account compromise, and advanced persistent threats that unfold gradually over weeks or months.
Cloud and Hybrid Network Monitoring Challenges
Modern networks extend far beyond traditional perimeters, incorporating cloud services, remote workers, mobile devices, and Internet of Things (IoT) deployments. Network security and monitoring strategies must adapt to these distributed architectures while maintaining comprehensive visibility.
Cloud-Specific Monitoring Approaches
Public cloud platforms provide native monitoring capabilities that organizations must leverage effectively. Microsoft Azure monitoring and Google Cloud security practices offer frameworks for collecting flow logs, integrating with SIEM platforms, and implementing threat detection within cloud environments.
Virtual Private Cloud (VPC) flow logs capture metadata about traffic traversing cloud networks, providing visibility similar to NetFlow in traditional environments. However, cloud monitoring faces unique challenges:
- Ephemeral resources that exist briefly and disappear
- Shared responsibility models where visibility depends on service type
- API-based attacks that don't generate traditional network traffic
- Multi-tenancy concerns affecting data isolation and privacy
Organizations must implement cloud-native security monitoring tools alongside traditional network monitoring to maintain complete visibility across hybrid infrastructure.
Securing Remote and Mobile Access
Zero Trust Network Access (ZTNA) principles assume that networks are already compromised and verify every access request regardless of origin. This approach transforms monitoring requirements by emphasizing identity verification, device posture assessment, and continuous authentication throughout sessions.
Remote access monitoring should track:
- VPN connection sources and durations
- Authentication method strength and success rates
- Endpoint security compliance status
- Application access patterns and data transfers
- Behavioral anomalies during remote sessions
Incident Response and Forensic Investigation
Network security and monitoring systems generate value primarily through effective incident response. Detection without appropriate response leaves organizations vulnerable despite investments in monitoring infrastructure.
Building Incident Response Capabilities
Structured response processes ensure consistent, effective handling of security incidents. The ENISA incident trend analysis provides context on common incident types and response patterns across European organizations.
Response workflows typically include:
- Detection and triage: Identifying potential incidents and assessing severity
- Containment: Limiting attack spread and preventing further damage
- Eradication: Removing attacker access and cleaning compromised systems
- Recovery: Restoring normal operations and validating system integrity
- Lessons learned: Documenting incidents and improving defenses
Network Forensics and Evidence Collection
Packet capture provides the most detailed network forensics data, recording complete communications for deep analysis. Tools like Wireshark enable investigators to reconstruct attack sequences, extract malware samples, and identify all systems involved in incidents.
However, continuous full packet capture generates enormous data volumes. Organizations typically implement selective capture strategies: Our guide to threat intelligence feeds explains how to choose and use them effectively in 2026.
- Continuous metadata capture: Recording flow data for all traffic
- Triggered full capture: Storing complete packets when alerts fire
- Targeted capture: Deep inspection of specific protocols or systems
- Sampled capture: Recording representative portions of high-volume traffic
Forensic investigations require careful evidence preservation, maintaining chain of custody, and protecting data integrity to support potential legal proceedings.
Practical Implementation for Small and Medium Organizations
Large enterprises employ dedicated security operations centers with specialized teams monitoring networks 24/7. Small and medium organizations face resource constraints that require practical, efficient approaches to network security and monitoring.
Prioritizing Critical Assets and High-Risk Areas
Risk-based monitoring focuses limited resources on protecting the most valuable assets and monitoring the highest-risk attack vectors. Organizations should identify:
- Systems containing sensitive customer or financial data
- Internet-facing services vulnerable to external attacks
- Privileged accounts with administrative access
- Legacy systems lacking modern security controls
- High-value targets likely to attract attackers
This prioritization ensures monitoring investments deliver maximum security improvements rather than spreading resources thinly across all systems.
Leveraging Managed Services and Automation
Managed Security Service Providers (MSSPs) offer cost-effective monitoring for organizations lacking internal security expertise. These services provide 24/7 monitoring, threat intelligence, and incident response capabilities at predictable monthly costs.
Security automation and orchestration reduces manual workload by automating repetitive tasks:
- Automated blocking of confirmed malicious IP addresses
- Ticket creation and assignment for detected incidents
- Evidence collection and preservation during investigations
- Vulnerability scanning and patch verification
- User account deprovisioning when employees depart
The SANS Institute whitepapers offer practical guidance on implementing monitoring programs and operational security practices suitable for organizations with limited resources.
Emerging Technologies and Future Directions
Network security and monitoring continue evolving as new technologies reshape both threat landscapes and defensive capabilities. Organizations must stay informed about emerging trends to maintain effective protection.
Artificial Intelligence and Machine Learning
AI-powered analytics process massive data volumes that overwhelm human analysts, identifying subtle patterns and correlations that indicate sophisticated attacks. Recent research on using language models for security analysis demonstrates how machine learning can bridge traditional signature-based detection with behavioral frameworks.
These systems excel at:
- Detecting zero-day exploits based on behavioral anomalies
- Reducing false positives through contextual understanding
- Predicting attack progression and recommended responses
- Automating threat hunting and investigation workflows
However, AI systems also introduce new challenges including adversarial attacks that manipulate model predictions and the need for extensive training data to achieve accuracy.
Extended Detection and Response (XDR)
XDR platforms integrate monitoring across networks, endpoints, applications, and cloud services into unified visibility and response. Rather than managing separate tools with incompatible data formats, XDR provides correlated insights spanning the entire technology stack.
This integration enables:
- Cross-layer attack detection identifying campaigns across multiple systems
- Automated investigation that gathers evidence from all relevant sources
- Coordinated response actions across network and endpoint controls
- Simplified operations through consolidated management interfaces
Software-Defined Networking and Microsegmentation
Software-defined networking (SDN) separates network control planes from data planes, enabling dynamic security policies that adapt to changing threats. Organizations can implement automated microsegmentation that isolates compromised systems instantly when monitoring detects suspicious behavior.
This programmable infrastructure transforms network security and monitoring from reactive to proactive, automatically adjusting defenses based on observed threats and business requirements.
Effective network security and monitoring require comprehensive visibility, intelligent detection, and rapid response capabilities that adapt to evolving threats. Organizations that implement layered monitoring strategies, leverage behavioral analytics, and maintain disciplined incident response processes position themselves to detect and neutralize attacks before they cause significant damage. NetGuardian Pro brings enterprise-grade protection to Windows systems through self-learning behavioral analysis that monitors how your PC normally operates and delivers plain-language alerts with one-click remediation, making advanced network security accessible without requiring technical expertise. Explore how NetGuardian Pro can strengthen your security posture at https://www.netguardiansecure.com/.