Intrusion Prevention: Protect Your Windows 11 PC
You lock your doors and windows when you leave home. Your Windows 11 PC needs the same kind of boundary protection for network connections. Intrusion prevention monitors the traffic coming into and out of your computer, blocking suspicious activity before it can compromise your files, passwords or privacy. While antivirus software scans files and programs for malware, intrusion prevention watches the network connections themselves, catching attacks that slip past traditional defenses. This protection matters whether you're working from home in Cape Town, managing a small business in Dallas, or connecting to public Wi-Fi at an airport.
What intrusion prevention actually does
Intrusion prevention systems watch every network connection your PC makes. They analyse the patterns, destinations and behaviours of data packets flowing in and out. When something looks wrong-an attempt to exploit a vulnerability, connect to a known malicious server, or send data in an unusual pattern-the system can block it immediately.
The difference from detection alone:
- Intrusion detection identifies threats and alerts you
- Intrusion prevention actively blocks threats in real time
- Prevention systems include detection capabilities, plus enforcement
Think of detection as an alarm that sounds when someone tries your door handle. Prevention is a deadbolt that stops them from getting in. Both matter, but prevention adds the enforcement layer.
Network-based systems protect the perimeter. They sit between your PC and the internet, examining every connection request. Host-based systems run directly on your computer, giving them visibility into application behaviour and system calls that network tools miss. The NIST guidance on intrusion detection and prevention systems outlines how organisations choose between network, host, wireless and behaviour-based approaches depending on their threat model and environment.
For Windows 11 users, host-based intrusion prevention offers practical advantages. It travels with your laptop when you leave home. It sees encrypted traffic after your VPN decrypts it. It understands which applications should connect to the internet and which should not.
Common threats intrusion prevention catches
Ransomware attacks often start with network reconnaissance. The attacker scans your PC for open ports, tries to exploit vulnerabilities, then moves laterally if they gain access. Intrusion prevention can spot these scanning patterns and block the connection before encryption begins.
| Threat type | How intrusion prevention responds |
|---|---|
| Port scanning | Detects rapid connection attempts to multiple ports, blocks the source |
| Exploit attempts | Identifies malformed packets or payloads targeting known vulnerabilities |
| Command and control traffic | Recognises communication patterns with botnet servers, blocks the connection |
| Data exfiltration | Flags unusual upload volumes or destinations, can pause the transfer |
| Lateral movement | Detects internal network scanning from compromised devices |
Phishing emails that slip past spam filters often contain links to credential-harvesting sites. When you click the link, intrusion prevention can check the destination against threat intelligence feeds and block access to known phishing domains. The CISA StopRansomware guidance explicitly recommends intrusion detection and prevention as part of a layered defense against ransomware attacks.
USB-based attacks represent another common vector. An attacker leaves an infected USB drive in a car park, hoping someone will plug it into a work PC. Modern intrusion prevention systems monitor USB connections for suspicious network activity that starts immediately after insertion.
Wi-Fi threats intensify when you travel. Public networks at coffee shops, hotels and airports often lack proper isolation between devices. An attacker on the same network can attempt man-in-the-middle attacks, injecting themselves between your laptop and the legitimate access point. Intrusion prevention detects the duplicate MAC addresses and suspicious ARP traffic that signal these attacks.
How intrusion prevention learns what's normal
Early intrusion prevention systems relied entirely on signatures-predefined patterns of known attacks. If the attack pattern matched the signature, the system blocked it. This approach caught known threats but missed new variations.
Modern systems add behavioural analysis. They learn what normal looks like for your PC: which applications connect to the internet, typical data volumes, regular connection times, trusted destinations. When behaviour deviates significantly, the system flags it even without a matching signature.
Behaviour-based detection looks for:
- Applications that suddenly start network connections they never made before
- Data transfers to geographic regions you've never contacted
- Connection attempts during unusual hours
- Protocols or ports inconsistent with the application's purpose
This adaptive approach reduces false alarms over time. The system stops alerting you about routine software updates or legitimate cloud sync activity. It focuses your attention on genuine anomalies that need investigation.
The MITRE ATT&CK framework maps intrusion prevention techniques to specific attacker tactics, helping you understand which threats your defenses address and where gaps remain. The framework shows that no single control stops everything-you need layers.
Setting up intrusion prevention on Windows 11
Windows 11 includes basic network protection through Windows Defender Firewall. You configure rules for inbound and outbound connections, specifying which applications can access the network and on which ports. This provides foundational control but lacks the active threat detection of dedicated intrusion prevention.
To review your Windows Firewall settings:
- Open Windows Security from the Start menu
- Navigate to Firewall & network protection
- Click on your active network (private, public or domain)
- Review which apps can communicate through the firewall
- Check notification settings for blocked connections
The built-in firewall operates on a rule basis. It allows or blocks based on your configuration. It doesn't analyse packet contents for exploit payloads, check destinations against threat intelligence, or adapt to behavioural patterns.
For enhanced protection, dedicated intrusion prevention software adds these capabilities. Tools like NetGuardian Pro run alongside your antivirus, specifically monitoring network connections through Wi-Fi, USB and Bluetooth. The 14 detection modules include ransomware behaviour monitoring and threat intelligence feeds, providing alerts you can understand without technical expertise.
Small businesses face additional considerations. You need consistent protection across multiple PCs without requiring dedicated IT staff. Look for solutions that:
- Deploy easily on Windows 11 Pro or Home editions
- Provide centralised visibility when needed
- Alert users directly rather than requiring a security operations centre
- Include clear documentation in plain language
- Offer reliable support without premium pricing tiers
Reducing false alarms without missing real threats
False positives frustrate users and reduce security. When legitimate activity triggers constant alerts, people start ignoring warnings. They disable protection or click through alerts without reading them. The real threat slips past in the noise.
Signature-based detection tends toward false positives when signatures are too broad. A pattern that catches one attack family might also match legitimate traffic with similar characteristics. Tuning requires adjusting signature sensitivity and adding exceptions for known-safe applications.
Behaviour-based systems need a learning period. During the first week or two, they establish baselines for normal activity. If you install new software or change work patterns during this period, the baseline shifts. Some systems let you mark changes as expected, preventing future alerts.
Practical tuning steps:
- Review alerts daily during the first week to establish patterns
- Mark trusted applications and destinations when alerts are clearly false
- Check that legitimate software updates don't trigger exfiltration warnings
- Verify business tools with cloud components get appropriate exceptions
- Document what you whitelist so you can review decisions later
The SANS guidance on IPS signature management provides detailed operational advice for teams running intrusion prevention deployments, including strategies for balancing detection sensitivity with operational impact.
For home users and small businesses, the key is finding tools that handle this complexity automatically. Systems that learn your normal patterns and apply threat intelligence to prioritise alerts let you focus on genuine risks without becoming a security analyst.
Integrating intrusion prevention with your existing security
Intrusion prevention complements other security tools rather than replacing them. Your antivirus scans files for malicious code. Your firewall enforces connection rules. Intrusion prevention adds real-time threat detection and blocking for network activity.
This layered approach matters because attacks evolve. Ransomware attackers know that most PCs run antivirus software. They use fileless attacks that operate in memory, never touching disk where antivirus scans. They encrypt their communications to evade basic firewall inspection. They move laterally through networks rather than triggering endpoint alerts.
| Security layer | Primary function | What it misses |
|---|---|---|
| Antivirus | Scans files and applications for malware | Network-based attacks, zero-day exploits, fileless threats |
| Firewall | Controls which connections are allowed | Malicious traffic within allowed connections, encrypted payloads |
| Intrusion prevention | Analyses connection behaviour and content | Malware already installed locally, social engineering |
| VPN | Encrypts traffic to protect privacy | Threats from the destination server, malware before encryption |
The CIS Controls framework recommends boundary defense including network-based intrusion detection and prevention as a fundamental security control. The framework prioritises controls by impact, helping smaller organisations allocate limited resources effectively.
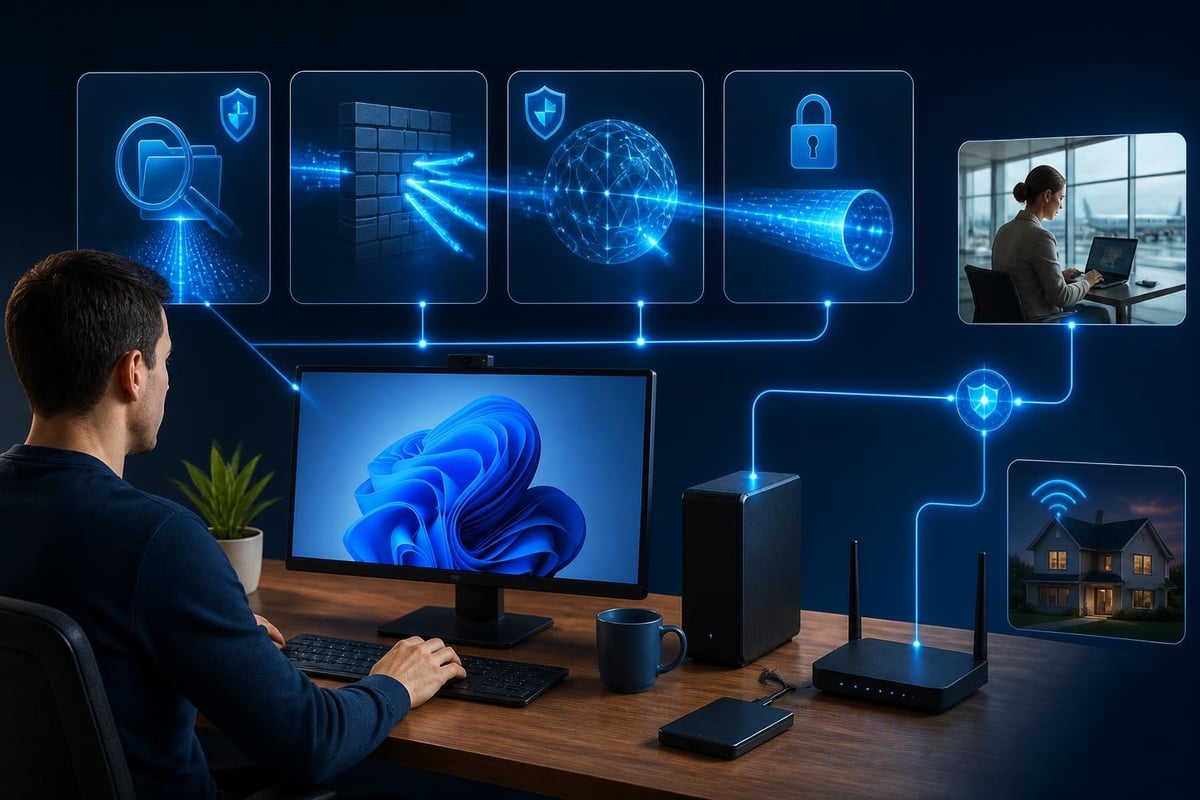
When travelling, intrusion prevention becomes especially valuable. Public Wi-Fi networks lack the basic security of your home router. Other users on the network can potentially see your traffic or attempt attacks. A VPN encrypts your data, preventing eavesdropping. Intrusion prevention adds protection against attacks targeting your PC directly.
What intrusion prevention can't do
No security tool provides complete protection. Understanding limitations helps you maintain appropriate caution and avoid false confidence.
Intrusion prevention cannot stop you from intentionally disabling security, entering credentials on a fake website, or running malware you explicitly chose to execute. If you click through warnings and grant permissions, the system assumes you know what you're doing.
Encrypted traffic presents challenges. When connections use strong encryption, intrusion prevention sees only metadata-the source, destination, timing and size of packets. It cannot inspect the actual content. This limits detection to behavioural patterns rather than payload analysis.
Zero-day exploits targeting unknown vulnerabilities sometimes slip through. Signature-based detection by definition cannot match patterns for threats that didn't exist when signatures were written. Behaviour-based systems have better odds of catching anomalous activity, but sophisticated attackers study detection systems and craft attacks to blend in.
Known limitations:
- Social engineering attacks that manipulate you directly
- Compromises that occurred before intrusion prevention was installed
- Insider threats from legitimate users with authorised access
- Physical attacks that bypass network controls entirely
- Vulnerabilities in the intrusion prevention software itself
The ENISA threat landscape research documents how attackers adapt to defensive measures, developing new techniques specifically designed to evade detection systems. Security requires ongoing adaptation rather than one-time setup.
Recent academic research on advanced persistent threat detection discusses the challenges of detecting sophisticated attackers who move slowly, use legitimate tools, and carefully blend their activity with normal operations. The research emphasises that intrusion prevention works best as part of a broader detection and response strategy.
Practical deployment for different users
Home users and families:
Your priority is protecting personal data, banking information and family photos without needing technical expertise. Choose intrusion prevention that explains threats in plain language. Look for tools that run quietly during normal operation but alert you clearly when action is needed. Automatic updates matter-you shouldn't need to manually download signature updates or adjust settings frequently.
Small businesses:
You need protection for multiple Windows 11 PCs without hiring dedicated IT staff. Consistency matters so that every employee has the same baseline security. Look for solutions that can be deployed across your organisation but still alert individual users about threats to their specific PC. Email support should include straightforward advice rather than assuming deep technical knowledge.
Travellers:
Whether you're working remotely across multiple locations or travelling for leisure, your threat exposure increases significantly on public networks. Intrusion prevention that includes a built-in VPN offers combined benefits: encrypted traffic for privacy and active monitoring for threats. Offline protection matters too-the system should function even when threat intelligence updates are delayed.
The CISA TIC 3.0 Security Capabilities Catalog provides federal guidance on intrusion detection and prevention deployment, including operational considerations that inform commercial implementations. While aimed at government agencies, the technical guidance applies to any organisation evaluating intrusion prevention systems.
Maintaining protection over time
Installing intrusion prevention represents the starting point, not the endpoint. Threats evolve constantly. New attack techniques emerge. Software vulnerabilities are discovered. Your protection needs regular maintenance to remain effective.
Monthly maintenance tasks:
- Review any alerts you dismissed to spot patterns you might have missed
- Check that automatic updates are functioning correctly
- Verify backup systems are working in case ransomware bypasses prevention
- Test that blocked connections stay blocked and allowed connections still work
- Review any new applications to ensure they have appropriate network permissions
Annual reviews help you step back and assess whether your security approach still matches your risk profile. Did your work patterns change? Are you travelling more or less? Have new family members started using devices on your network? Do new business requirements affect which connections need to be allowed?
Security awareness matters as much as the tools themselves. Understanding why intrusion prevention blocked a connection helps you make informed decisions about whether to override the block or investigate further. Training doesn't require formal courses-just attention to the alerts you receive and willingness to learn what they mean.
Intrusion prevention gives your Windows 11 PC an active defense that complements your antivirus and firewall, monitoring network connections for threats that traditional security tools miss. The combination of signature-based detection, behavioural analysis and threat intelligence helps protect your data whether you're working from home, managing a small business, or connecting from a coffee shop in another country. NetGuardian Pro provides this protection through 14 detection modules that monitor Wi-Fi, USB and Bluetooth connections, delivering clear alerts you can understand and act on without an IT background. The one-time purchase includes free updates and email support, giving you professional-grade network security designed for real people facing real threats.