IDS Detection: How It Protects Your Network in 2026
Network security can feel overwhelming when you're managing devices at home or in a small business. You might wonder what's really happening behind the scenes when your laptop connects to Wi-Fi, or whether someone could be probing your network without your knowledge. IDS detection gives you visibility into these activities by monitoring traffic patterns, identifying suspicious behaviour and alerting you to potential threats before they escalate. It works alongside your existing security tools to create an extra layer of defence that doesn't require specialist knowledge to understand or act on.
What IDS detection actually does
IDS stands for intrusion detection system. IDS detection is the process of examining network traffic and system activity to spot patterns that indicate unauthorised access, malware communication or other security threats. Think of it as a vigilant observer that watches every connection attempt, data transfer and network request flowing through your devices.
The detection process works in real time. As packets of data move across your network, IDS detection compares them against known threat patterns, behaviour baselines and rule sets. When something doesn't match what's expected, the system flags it for your attention.
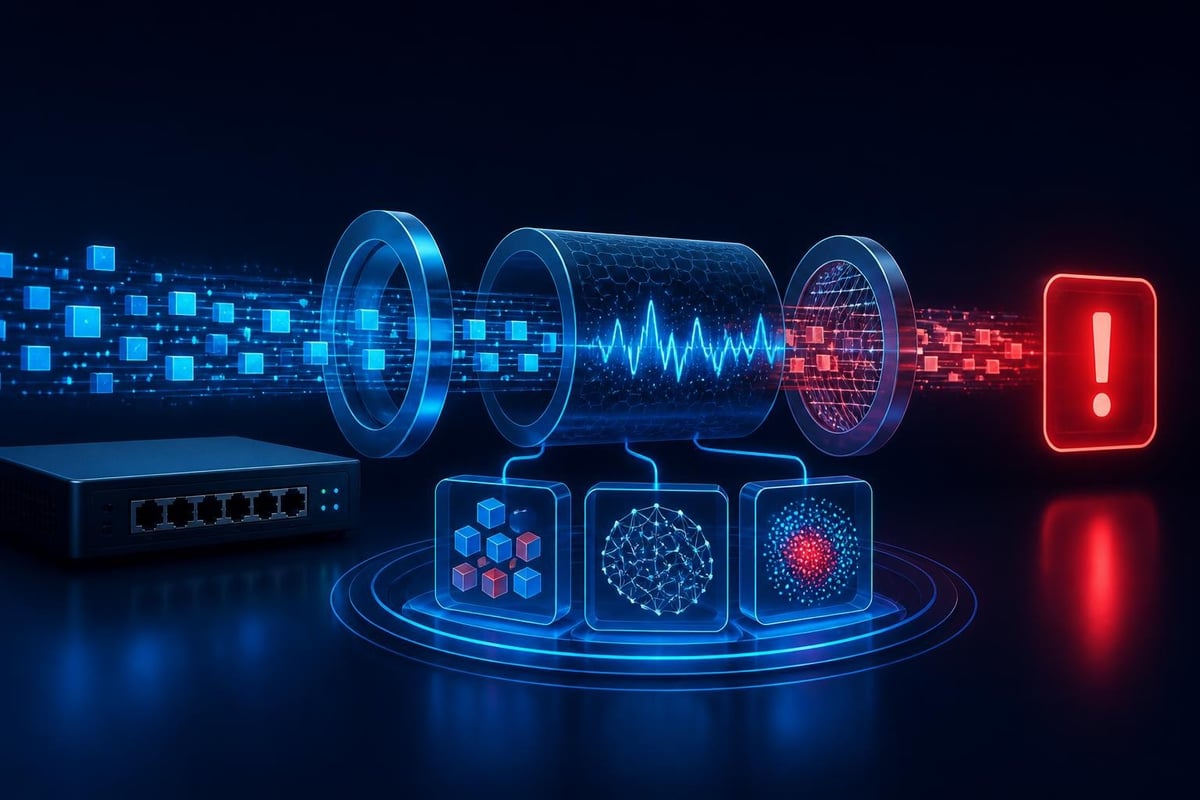
This monitoring happens at different layers. Some IDS detection focuses on network traffic itself, watching for port scans, unusual connection patterns or data exfiltration attempts. Other types examine what's happening on the device, tracking process behaviour, file system changes and registry modifications that might indicate compromise.
Signature-based versus behaviour-based detection
IDS detection uses two main approaches to identify threats. Understanding both helps you appreciate why modern systems combine them.
Signature-based detection compares network traffic and system activity against a database of known threat patterns. These signatures describe specific characteristics of malware, exploit code or attack techniques. When the IDS spots an exact or close match, it raises an alert.
The strength of signature-based IDS detection is accuracy. False positives are rare because the system only alerts on patterns that match documented threats. The limitation is that it can't catch brand-new attacks that haven't been catalogued yet. That's why threat intelligence feeds matter – they keep signature databases current as new threats emerge.
Behaviour-based detection takes a different approach. Instead of looking for known bad patterns, it establishes what normal activity looks like on your network and devices. When something deviates significantly from this baseline, the system flags it as potentially suspicious.
This method catches zero-day threats and novel attack techniques because it doesn't rely on prior knowledge of specific malware. The trade-off is that legitimate but unusual activity can sometimes trigger false alarms. Good behaviour-based systems use machine learning to refine their understanding of normal over time, reducing unnecessary alerts as they learn your environment.
Modern IDS detection typically combines both approaches. Signatures catch known threats quickly and reliably, while behaviour analysis guards against new attack methods. For detailed technical approaches to behaviour detection, MITRE ATT&CK provides practical detection guidance tied to real attacker techniques.
How detection modules work together
Most comprehensive IDS solutions don't rely on a single detection method. Instead, they deploy multiple specialised modules, each focused on a particular aspect of network or system security.
| Module Type | What It Monitors | Typical Threats Detected |
|---|---|---|
| Network traffic analysis | Packet inspection, connection patterns | Port scans, data exfiltration, C2 communication |
| Protocol analysis | Wi-Fi, USB, Bluetooth behaviour | Rogue access points, malicious USB devices |
| Ransomware behaviour | File system activity, encryption patterns | Rapid file modification, shadow copy deletion |
| Threat intelligence | Connection destinations, IP reputation | Known malicious servers, botnet C2 infrastructure |
Each module operates independently but feeds into a unified alert system. This layered approach means that even if one detection method misses something, another module might catch it from a different angle.
Consider a ransomware infection as an example. Network traffic analysis might spot unusual outbound connections. Protocol monitoring could flag suspicious file-sharing activity. Ransomware behaviour detection would notice the rapid encryption of documents. Together, these signals paint a clear picture of what's happening, even if no single module has definitive proof on its own.
Reducing false positives through learning
One of the biggest frustrations with IDS detection is false alarms. You don't want to be interrupted constantly by alerts about legitimate activity, but you also can't afford to ignore warnings that might indicate real threats.
Smart IDS systems address this through adaptive learning. They observe your normal patterns – the websites you visit regularly, the devices you connect, the applications that communicate over your network. Over time, the system builds a profile of what's typical for your environment.
When activity matches your established patterns, confidence is high that it's legitimate. When something genuinely unusual happens, the alert carries more weight because it represents a real deviation from your norm. This approach reduces alert fatigue while maintaining sensitivity to actual threats.
The learning period matters. During the first few weeks with a new IDS, you might see more alerts as the system calibrates itself. Review these alerts to help the system understand what's normal for you. Mark false positives when appropriate, and the detection accuracy improves steadily.
Setting up effective ids detection on Windows 11
Windows 11 provides a solid foundation for network security, but the operating system alone doesn't offer comprehensive IDS detection. You need additional tools to monitor connections, analyse traffic patterns and alert you to suspicious activity.
Start by understanding what you want to protect. For home users, priorities typically include:
- Preventing unauthorised access to personal files and devices
- Detecting ransomware before it encrypts your documents
- Spotting suspicious connections that might indicate malware
- Monitoring devices connected via Wi-Fi, USB and Bluetooth
Small businesses add concerns about customer data, business communications and regulatory compliance. Travellers need protection on public Wi-Fi networks where threats are more prevalent.
Choosing between host-based and network-based detection
Host-based IDS detection runs directly on your Windows 11 device. It monitors local system activity, network connections made by that specific PC or laptop, and behaviour of processes running on the machine.
The advantage is visibility into what's happening on the device itself. Host-based systems can see process-level activity, file modifications and registry changes that network-based tools miss. They work even when you're travelling and connecting through different networks.
Network-based IDS detection monitors traffic flowing across your entire network. It's typically deployed at the network perimeter or key choke points, watching all devices simultaneously.
This approach excels at spotting attack patterns that target multiple devices or lateral movement after initial compromise. For small businesses with several computers, network-based detection provides centralised visibility. The limitation is that it can't see encrypted traffic easily and doesn't monitor offline devices.
For most home users and small businesses, host-based IDS detection makes more practical sense. Each Windows 11 device gets its own protection that travels with it. When you're working from a café or hotel, your IDS continues monitoring regardless of the underlying network.
Understanding IDS detection alerts
When your IDS detection system raises an alert, you need to know what it means and what to do about it. Good systems provide clear information without requiring you to decode technical jargon or analyse packet captures.
Effective alerts include several key elements:
- What was detected – The specific activity or pattern that triggered the alert
- Severity level – How serious the threat appears to be
- Source information – Which device, connection or process is involved
- Recommended action – What you should do in response
Not every alert demands immediate action. Some represent low-risk events worth noting but not blocking. Others indicate active threats that need intervention right away.
Triaging and responding to detections
When you receive an IDS detection alert, follow a systematic approach to decide how to respond.
Check the severity. High-severity alerts about ransomware behaviour, data exfiltration or known malware connections deserve immediate attention. Medium-severity alerts about unusual but not definitively malicious activity can be investigated when convenient. Low-severity informational alerts simply keep you aware of network events.
Review the context. Did the alert trigger during activity you initiated? If you just installed new software or connected a new device, some alerts might reflect legitimate changes. If the alert appeared while you were away from your computer, that raises suspicion.
Look for related alerts. Multiple alerts from different detection modules about the same connection or process strengthen the case that something is wrong. A single isolated alert might be a false positive.
Take appropriate action. Options typically include:
- Block the connection – Prevent communication with a suspicious server or device
- Isolate the device – Disconnect from networks to contain potential threats
- Monitor closely – Watch for additional suspicious activity before taking action
- Mark as false positive – Help the system learn when alerts don't represent real threats
For small businesses, document your responses to build an incident history. This helps you spot patterns and refine your security approach over time.
Advanced detection techniques in modern IDS
IDS detection has evolved significantly beyond simple signature matching. Modern systems incorporate sophisticated analysis methods that improve detection accuracy while reducing false alarms.
Machine learning and deep learning approaches
Machine learning enables IDS detection to recognise complex patterns that would be impractical to define through manual rules. The system analyses large volumes of network traffic and system behaviour, learning to distinguish normal activity from anomalies.
Deep learning takes this further by using neural networks that can identify subtle patterns across multiple dimensions of data. These approaches excel at detecting attack variations and previously unseen threats. Research published in ArXiv surveys deep learning algorithms used in modern intrusion detection systems.
The practical benefit for you is fewer missed threats and more accurate alerts. The system doesn't just match static patterns – it understands context and adapts to evolving attack techniques.
Protocol-specific detection
Different network protocols require different detection approaches. Wi-Fi traffic looks different from USB communications, which differ from Bluetooth connections. Effective IDS detection includes specialised modules for each protocol.
Wi-Fi monitoring watches for rogue access points, evil twin attacks and unauthorised devices on your network. It can detect when someone attempts to intercept your wireless communications or when malware tries to create ad-hoc connections.
USB detection tracks what devices connect to your ports. It can spot malicious USB drives that attempt to run code automatically or devices that masquerade as keyboards to inject commands.
Bluetooth monitoring identifies unauthorised pairing attempts and suspicious device behaviour. This matters as more devices use Bluetooth for connectivity, creating new attack surfaces.
For technical details on how modern detection engines handle different protocols, Suricata’s documentation provides in-depth reference material on deployment modes and protocol analysis.
Integrating IDS detection with your security stack
IDS detection works best as part of a layered security approach, not as a standalone solution. Understanding how it fits with your other defences helps you build comprehensive protection.
Antivirus software focuses on malware signatures and known threats at the file and process level. It scans downloads, monitors running programs and quarantines malicious files. Your IDS detection complements this by watching network behaviour and identifying threats that don't rely on malware files – things like unauthorised access attempts, suspicious connections and abnormal system activity.
Firewalls control what traffic is allowed in and out of your network based on rules you configure. They're about access control. IDS detection monitors allowed traffic for suspicious patterns, catching threats that slip through firewall rules.
VPNs encrypt your connection to protect privacy and prevent interception. A VPN doesn't detect threats – it makes your traffic harder to snoop on. IDS detection watches for suspicious activity both inside the encrypted tunnel and on the local device, identifying threats regardless of whether you're using a VPN at the time.
NetGuardian Pro demonstrates this integrated approach. Its 14 detection modules run directly on your Windows 11 device, monitoring Wi-Fi, USB and Bluetooth connections while also tracking ransomware behaviour and consulting threat intelligence. It includes a built-in WireGuard VPN for travel, creating layered protection that works alongside your antivirus without duplication.
Configuring detection sensitivity
Most IDS systems let you adjust how sensitive the detection should be. Higher sensitivity means more potential threats get flagged, but also more false positives. Lower sensitivity reduces false alarms but might miss subtle threats.
The right balance depends on your risk tolerance and how much time you can spend reviewing alerts. Home users typically prefer moderate sensitivity with strong detection of high-severity threats and fewer alerts about low-risk activity. Small businesses might choose higher sensitivity to ensure nothing slips through, accepting that IT staff will need to review more alerts.
You can often configure sensitivity separately for different detection modules. Set ransomware detection high, because false positives are preferable to missed infections. Network scanning detection might be moderate, since some scans are routine network maintenance.
IDS detection for travellers and remote work
When you work away from your home or office network, IDS detection becomes even more important. Public Wi-Fi networks in cafés, hotels and airports are favourite hunting grounds for attackers.
Common threats on public networks include:
- Man-in-the-middle attacks where someone intercepts your connection to steal credentials or inject malicious content
- Rogue access points that mimic legitimate networks to capture your traffic
- Lateral attacks where compromised devices on the same network target yours
- Malicious USB charging stations that attempt to install malware when you connect
Your IDS detection should travel with you. Host-based systems that run on your Windows 11 laptop continue monitoring regardless of which network you connect to. They can alert you immediately if something suspicious happens, giving you time to disconnect before damage occurs.
When travelling, pay special attention to alerts about:
- Unexpected inbound connection attempts (someone scanning for vulnerable devices)
- Your device communicating with unfamiliar servers (possible malware command-and-control)
- USB devices behaving suspiciously (malicious charging stations or accessories)
- Unusual Wi-Fi behaviour (potential evil twin or man-in-the-middle attack)
Keeping IDS detection current
Threat landscapes evolve constantly. New vulnerabilities emerge, attackers develop novel techniques, and malware variants appear daily. Your IDS detection system needs regular updates to remain effective.
Signature updates deliver new threat patterns as they're discovered. Most systems check for these automatically, downloading fresh signatures daily or even hourly. This ensures you're protected against the latest documented threats.
Detection engine updates improve how the system analyses behaviour and identifies suspicious patterns. These come less frequently than signature updates but can significantly enhance detection capabilities. They might introduce new detection modules, refine machine learning models or improve alert accuracy.
Rule updates from threat intelligence providers keep your system aware of newly identified malicious servers, botnet infrastructure and attack campaigns. These updates typically happen automatically in the background.
For guidance on how detection rules work in modern security systems, Elastic Security’s documentation provides authoritative details on rule types and management.
Plan for regular reviews of your IDS detection configuration. Every few months, check whether your alert settings still make sense, review false positive patterns and adjust sensitivity if needed. As you add new devices or change how you use your network, update your baseline expectations so the system continues distinguishing normal from suspicious accurately.
| Maintenance Task | Frequency | Purpose |
|---|---|---|
| Signature updates | Daily | Catch newly documented threats |
| Engine updates | Monthly | Improve detection capabilities |
| Configuration review | Quarterly | Adjust for environment changes |
| Alert pattern analysis | Quarterly | Reduce false positives |
| Training refinement | As needed | Help system learn your normal activity |
Evaluating IDS detection effectiveness
How do you know whether your IDS detection is actually working? Regular testing and evaluation ensure you're getting the protection you expect.
Monitor alert quality. Are you receiving alerts about genuine suspicious activity? Or are most alerts false positives about normal behaviour? High-quality detection produces relatively few alerts, but those it generates represent real concerns worth investigating.
Test detection coverage. Periodically verify that your IDS would catch known attack techniques. This doesn't mean launching actual attacks, but rather confirming that detection modules are active and monitoring the right areas. Check that Wi-Fi monitoring is running, USB detection is enabled and behaviour analysis is functioning.
Review missed detections. If you discover a security incident after the fact, investigate whether your IDS should have detected it. This helps identify gaps in coverage or configuration issues. Learning from near-misses improves your security posture.
Compare to benchmarks. Security frameworks like NIST provide guidance on intrusion detection evaluation. NIST Special Publication 800-31 offers foundational concepts on IDS architecture and operational considerations.
For small businesses, consider an annual security assessment that includes reviewing your IDS detection effectiveness. For home users, informal quarterly checks usually suffice – verify you're seeing some alerts (showing the system is active) but not so many that you ignore them.
Practical deployment considerations
Getting IDS detection running effectively requires some planning. Whether you're protecting a home network or a small business, several practical factors influence success.
Resource requirements matter on Windows 11. IDS detection uses CPU cycles to analyse traffic and memory to store baselines and signatures. On modern laptops with adequate RAM, the impact is minimal during normal use. Older or resource-constrained devices might experience slight slowdowns when detection is actively scanning heavy traffic.
Storage needs vary based on logging detail. If you keep extensive logs of all detected events, storage requirements grow over time. Most systems offer configurable logging that balances detail with disk space usage. Critical alerts stay permanently, while routine informational logs age out after a few weeks.
Network performance impact is typically negligible with host-based IDS detection. The system monitors traffic as it flows but doesn't add significant latency. Network-based systems that inspect all traffic centrally can become bottlenecks if undersized for your traffic volume.
Alert management workflow needs thought upfront. Who receives alerts? How quickly must you respond? What's the escalation path if something serious appears? For home users, alerts go to whoever manages the devices. Small businesses should designate someone responsible for security alerts and define clear response procedures.
User training shouldn't be overlooked. Everyone using protected devices should understand that security alerts might appear and know the basics of how to respond. They don't need to become security experts, but they should know not to dismiss alerts without reading them and to ask for help when uncertain.
IDS detection provides essential visibility into what's happening on your network and devices, catching threats that other security tools might miss. It works best when combined with antivirus, firewalls and good security practices, creating layers of defence that protect your data and privacy. NetGuardian Pro brings this protection directly to your Windows 11 devices with clear alerts you can understand and act on, whether you're at home, running a small business or travelling abroad.
About the author. Published by Joel Papenfus, founder of NetGuardian and creator of NetGuardian Pro. The sources this post draws on are linked in the post. Reviewed and checked by Joel on 1 October 2026.