IDS Cyber Security: Protect Your Windows 11 PC at Home
Network threats don't announce themselves with flashing lights or warning sirens. They creep through your Wi-Fi connection, probe your home network for weaknesses, and sometimes slip past your antivirus before you know something's wrong. That's where ids cyber security becomes essential for Windows 11 users. An intrusion detection system watches your network connections, learns what normal looks like, and alerts you when something suspicious happens. Whether you're working from home in Johannesburg, running a small business in Texas, or connecting to public Wi-Fi at a coffee shop, understanding how IDS technology works helps you make better security decisions.
What IDS cyber security actually does
An intrusion detection system monitors network traffic flowing to and from your PC. It examines connection patterns, data packets, and communication behaviours to spot signs of attack or unauthorised access. Unlike antivirus software that scans files for known malware signatures, ids cyber security focuses on network-level threats – the connections and communications that happen before malicious code reaches your hard drive.
The NIST Computer Security Resource Center defines an IDS as software that automates the process of monitoring events in a computer system or network and analysing them for signs of security problems. This definition covers everything from simple port scans to sophisticated multi-stage attacks.
Detection methods that matter for Windows 11
Modern ids cyber security uses several detection approaches simultaneously:
- Signature-based detection matches network patterns against known attack signatures
- Anomaly-based detection flags behaviour that deviates from your normal baseline
- Stateful protocol analysis tracks how network protocols are being used and spots violations
- Behavioural monitoring watches for suspicious sequences that suggest ransomware or data theft
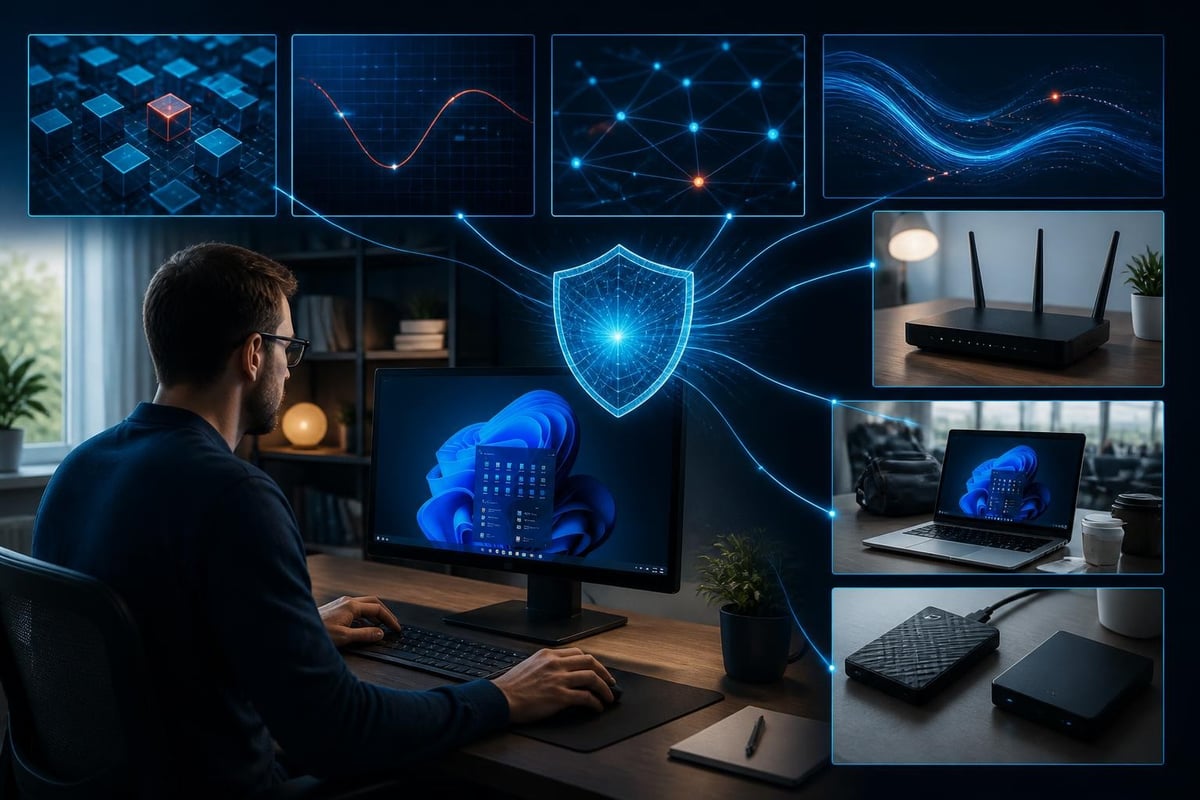
The most effective systems combine these methods. A port scan might match a signature. An unusual spike in outbound connections at 3 AM triggers anomaly detection. A program attempting to encrypt hundreds of files activates behavioural monitoring. Together, they provide layered protection.
Why Windows 11 users need IDS protection
Your antivirus software excels at catching malware on your hard drive. But many threats operate at the network layer, establishing connections, exfiltrating data, or communicating with command-and-control servers before any file hits your disk. IDS cyber security fills this gap by monitoring what your PC communicates with and how.
Network-based attacks Windows users face:
| Threat type | What happens | Why antivirus misses it |
|---|---|---|
| Port scanning | Attackers probe for open services | No malicious file to scan |
| Lateral movement | Compromised device spreads across network | Legitimate protocols used maliciously |
| Data exfiltration | Files uploaded to external servers | Outbound traffic often unrestricted |
| C2 communication | Malware phones home for instructions | Encrypted traffic looks normal |
| Ransomware preparation | Mapping network shares before encryption | Reconnaissance uses normal tools |
According to the ENISA Threat Landscape 2025, network-based reconnaissance and lateral movement remain top attack vectors. Detecting these early requires monitoring network behaviour, not just scanning files.
How IDS cyber security works on your PC
Traditional IDS solutions ran on network appliances or servers, analysing traffic for entire organisations. Modern endpoint-based ids cyber security runs directly on your Windows 11 PC, giving you visibility into your own network activity without needing enterprise infrastructure.
What happens when you're protected
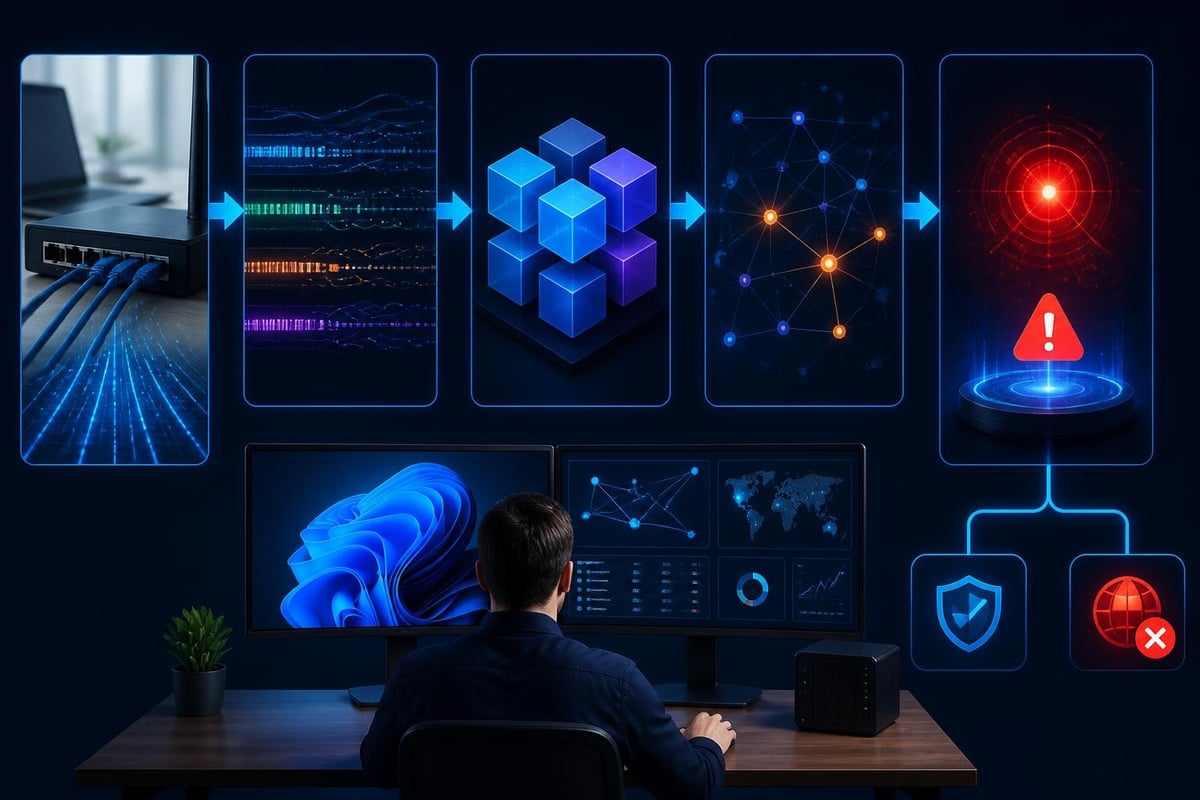
When ids cyber security is active on your Windows 11 machine, it captures and analyses network packets in real time. Detection modules examine different aspects simultaneously – one watches Wi-Fi connections, another monitors USB network adapters, a third tracks Bluetooth communications. Each module applies its detection rules and feeds alerts to a central engine.
The detection workflow:
- Traffic capture – Network drivers pass copies of packets to the IDS
- Protocol decoding – The system identifies what type of traffic it is (HTTPS, DNS, SMB, etc.)
- Analysis – Detection modules apply signatures, check against baselines, and evaluate behaviour
- Correlation – Related events are linked together to identify attack patterns
- Alerting – Suspicious activity generates clear, actionable alerts
- Response – Blocking rules can stop connections or isolate the PC
The MITRE ATT&CK detection strategies framework provides structured approaches for mapping detection techniques to specific attack behaviours. This helps ensure ids cyber security covers the tactics attackers actually use.
Learning normal to spot abnormal
Static rules alone generate too many false alarms. Your usage patterns differ from your neighbour's. A graphic designer uploads large files regularly. A writer rarely sends anything bigger than documents. Effective ids cyber security adapts to your baseline.
Machine learning algorithms analyse your network activity over days and weeks, building a profile of normal behaviour. They track which servers you connect to, typical data volumes, usual connection times, and regular protocols. When something falls outside this baseline – a midnight connection to an unfamiliar IP address, sudden encryption traffic, or unusual protocol usage – the system flags it.
This approach reduces false positives while catching novel attacks that don't match any signature. It's particularly valuable for detecting zero-day exploits and customised malware that antivirus databases haven't seen yet.
Practical protection scenarios for home and business
Understanding theory helps, but what does ids cyber security actually protect you from in daily life? Here are scenarios where network-level detection makes the difference.
Home network security
Your home Wi-Fi connects phones, tablets, smart TVs, printers, and PCs. If one device gets compromised, attackers often use it as a stepping stone to reach others. IDS cyber security on your Windows 11 PC monitors for lateral movement attempts.
Signs IDS detects in home networks:
- Another device scanning your PC's open ports
- Unusual file-sharing protocol traffic from IoT devices
- Unexpected authentication attempts from local IP addresses
- New devices joining your network and immediately probing others
Small businesses face similar challenges. A compromised laptop brought from home can spread ransomware across your office network. IDS alerts you before encryption begins.
Travel and public Wi-Fi protection
Public Wi-Fi networks are inherently untrusted. You share them with strangers, and sometimes attackers deliberately set up rogue access points with legitimate-sounding names. IDS cyber security helps you spot man-in-the-middle attacks and suspicious network behaviour.
When you connect to airport or hotel Wi-Fi, ids cyber security monitors for:
- ARP spoofing attempts (someone impersonating the router)
- Unexpected proxy redirects
- SSL stripping attacks that downgrade HTTPS to HTTP
- Port scans from other devices on the network
Combined with VPN protection, network monitoring gives you visibility into threats your VPN alone wouldn't catch.
Ransomware behaviour detection
Modern ransomware often follows predictable patterns before encryption starts. It maps network shares, tests file access, and sometimes exfiltrates data as leverage. IDS cyber security spots these preparation stages.
| Ransomware stage | Network behaviour | What IDS detects |
|---|---|---|
| Reconnaissance | SMB share enumeration | Unusual volume of share access requests |
| Privilege escalation | LDAP queries, authentication attempts | Abnormal credential traffic |
| Lateral movement | Admin share connections | Unexpected inter-PC traffic patterns |
| Data staging | Large file transfers to temp folders | Unusual internal data movement |
| Encryption | Simultaneous access to many files | Rapid sequential file modification |
Catching ransomware during reconnaissance or staging gives you time to disconnect, isolate, and respond before encryption destroys your data. That's the practical value of ids cyber security working alongside your antivirus.
Choosing and using IDS protection
Not all intrusion detection systems suit home users or small businesses. Enterprise solutions assume you have IT staff to interpret alerts and tune detection rules. You need ids cyber security designed for people without technical backgrounds.
Features that matter for non-technical users
Clear, understandable alerts – Technical jargon helps nobody. Alerts should explain what happened, which program or connection triggered it, and suggest what to do next.
Built-in threat intelligence – The system should automatically update its signature databases and threat indicators so you don't need to research threats yourself.
False positive reduction – Learning algorithms that adapt to your usage reduce the noise of irrelevant alerts that cause people to ignore genuine threats.
Simple blocking controls – When something suspicious appears, you should be able to block it with one click, not navigate complex firewall rules.
PC isolation capability – If you suspect compromise, quickly disconnecting from the network prevents spread while you investigate.
The NIST Special Publication 800-94 provides comprehensive guidance on IDS deployment and management, though much of it targets enterprise environments.
For Windows 11 users seeking network-level protection without complexity, endpoint-based ids cyber security offers practical advantages. NetGuardian Pro runs directly on your PC with 14 detection modules covering Wi-Fi, USB, Bluetooth, ransomware behaviour, and more. It complements your existing antivirus by monitoring network threats that file-based scanning misses.
Getting started with IDS protection
- Install and baseline – Let the system observe your normal activity for several days
- Review initial alerts – Understand what it's detecting and why
- Adjust sensitivity – If legitimate activity triggers frequent alerts, tune detection thresholds
- Enable blocking – Once confident in detection accuracy, activate automatic blocking for high-severity threats
- Check alerts regularly – Make reviewing security alerts part of your weekly routine
Don't expect perfection immediately. IDS cyber security improves as it learns your patterns and as you learn to interpret its alerts. The goal is practical protection that fits into your daily workflow, not a security system that demands constant attention.
Advanced considerations for small businesses
Small businesses need the same network visibility as enterprises but rarely have dedicated security staff. IDS cyber security levels the playing field by automating detection that would otherwise require expert analysis.
Multiple-device protection
If you're protecting several Windows 11 laptops or desktops, consider how alerts are managed. Some businesses designate one technically-inclined person to review alerts from all protected machines. Others prefer each user to see only their own device's alerts and escalate concerns.
Deployment models for small teams:
- Individual protection – Each employee runs IDS independently and responds to their own alerts
- Designated reviewer – One person monitors alerts from all protected devices
- Hybrid approach – Critical alerts go to the reviewer; minor ones stay with individual users
The Carnegie Mellon SEI report on AI for APT detection explores how machine learning enhances detection of sophisticated, multi-stage attacks. While focused on advanced persistent threats, the principles apply to any network-based attack detection.
Compliance and evidence collection
Some industries require logging and monitoring of network activity. IDS cyber security provides audit trails showing what was detected and when. If you suspect a breach, these logs become evidence for forensics or insurance claims.
Even without formal compliance requirements, detailed logs help you understand security incidents. What did the attacker access? When did the compromise begin? Which other devices might be affected? IDS logs answer these questions.
Complementing your existing security
The most important thing to understand about ids cyber security is what it doesn't replace. It's not antivirus, not a firewall, and not a complete security solution on its own. It's a specialised tool focused on network-level threat detection.
How IDS fits your security stack:
| Security layer | What it protects | What it misses |
|---|---|---|
| Antivirus | Files, executables, email attachments | Network-based attacks, zero-days |
| Firewall | Blocks unauthorised inbound connections | Doesn't analyse allowed traffic |
| IDS | Network behaviour, lateral movement, C2 | Doesn't scan files for malware |
| VPN | Encrypts traffic, masks IP address | Doesn't detect malicious encrypted traffic |
Used together, these tools provide defence in depth. Your firewall blocks most inbound attacks. Your antivirus catches malware that reaches your disk. Your VPN protects traffic confidentiality. Your ids cyber security monitors everything else – the connections, behaviours, and patterns that other tools don't examine.
Research from organisations like SANS Institute on optimising intrusion detection demonstrates how combining detection methods improves overall security posture. No single tool catches everything, but layered detection dramatically reduces risk.
When to investigate alerts
Not every IDS alert demands immediate action. Learning to prioritise helps you focus on genuine threats without alert fatigue.
High-priority alerts requiring immediate investigation:
- Ransomware behaviour detection (rapid file modifications, encryption patterns)
- Outbound connections to known malicious IP addresses
- Lateral movement from other network devices
- Unusual administrative activity or privilege escalation attempts
Medium-priority alerts worth reviewing:
- Port scans from external addresses
- Unexpected protocol usage
- Connections to newly-registered domains
- Unusual connection volumes
Low-priority alerts you can batch review:
- Minor deviations from baseline during unusual but legitimate activities
- Known-safe programs making unexpected but harmless connections
- Transient network anomalies that don't repeat
Over time, you'll develop intuition for what matters in your environment. The key is not ignoring alerts entirely but reviewing them proportionally to their severity.
Future developments in IDS technology
IDS cyber security continues evolving as attacks become more sophisticated. Emerging trends worth understanding include deeper integration of artificial intelligence, better handling of encrypted traffic, and IoT device monitoring.
AI and machine learning advances
Current anomaly detection uses relatively simple statistical models. Next-generation systems apply deep learning to identify subtle attack patterns humans and traditional algorithms miss. These systems will better distinguish between genuine threats and false positives.
However, attackers also use AI to make their attacks look more like normal traffic. This creates an ongoing arms race between detection systems and evasion techniques.
Encrypted traffic analysis
More than 90% of web traffic now uses HTTPS encryption. This protects your privacy but also blinds traditional IDS approaches that rely on inspecting packet contents. Modern ids cyber security increasingly relies on metadata analysis – connection timing, packet sizes, traffic volumes – rather than content inspection.
Techniques like encrypted traffic fingerprinting allow detection of malicious patterns even when you can't read the actual data. This preserves privacy while maintaining security visibility.
IoT and smart home integration
Your Windows 11 PC isn't the only network-connected device in your home. Smart TVs, cameras, thermostats, and door locks all communicate over your network. Comprehensive ids cyber security needs to monitor these devices for compromise and misuse.
Expect future systems to provide unified visibility across all network-connected devices, not just your PC. This whole-network approach better detects lateral movement and coordinated attacks.
Measuring IDS effectiveness
How do you know if your ids cyber security is working? Unlike antivirus that displays obvious malware detections, IDS protection operates quietly until something suspicious happens.
Indicators your IDS is functioning properly:
- Regular baseline updates showing it's learning your patterns
- Occasional low-severity alerts during routine activity (shows it's watching)
- Immediate alerts when you intentionally do something unusual (validates detection)
- Updated threat intelligence databases (confirms it's receiving security updates)
Consider periodically testing your detection by performing safe but unusual activities. Connect to a new VPN server, access an unusual website, or transfer large files at odd hours. If your IDS doesn't notice or adapt, something may need adjustment.
Professional penetration testing provides more rigorous validation, though it's often overkill for home users and small businesses. The IEEE conference survey on IDS status and trends discusses evaluation methodologies and effectiveness metrics in depth.
Making IDS work for you
Implementing ids cyber security successfully means adapting it to your specific needs and environment. Cookie-cutter approaches rarely work well.
Questions to answer before deployment:
- What are you most worried about – ransomware, data theft, unauthorised access, or all three?
- How much time can you realistically spend reviewing alerts each week?
- Do you prefer aggressive detection with more false positives, or conservative detection with potentially missed threats?
- Which network interfaces need monitoring – just Wi-Fi, or also Bluetooth and USB?
- Do you travel frequently and need protection on public networks?
Your answers shape how you configure detection sensitivity, which modules to enable, and how alerts are prioritised. Someone running a home business with client data needs different settings than a casual user primarily concerned about ransomware.
The beauty of modern ids cyber security for Windows 11 is its flexibility. You're not locked into one-size-fits-all enterprise policies. You control what's monitored, what's blocked, and how you're alerted.
Network threats targeting Windows 11 users continue growing in sophistication and volume, but ids cyber security provides practical visibility and protection when implemented thoughtfully. Understanding how intrusion detection complements your antivirus and firewall helps you build layered security appropriate for your risk level. Whether you're protecting your family's home network, a small business, or your laptop while travelling, network-level monitoring detects threats other tools miss. NetGuardian Pro brings this protection to your Windows 11 PC with 14 detection modules, clear alerts, and one-time pricing – no security expertise required.