Cyber Security Monitoring: Essential Strategies for 2026
In today's digital landscape, threats evolve faster than ever before. Organizations and individuals face a relentless barrage of attacks ranging from ransomware to sophisticated phishing campaigns. Effective cyber security monitoring has become the cornerstone of modern digital defense, providing the visibility and rapid detection capabilities necessary to identify threats before they cause irreparable damage. This comprehensive guide explores the essential components, strategies, and best practices that define successful monitoring programs in 2026.
Understanding the Foundation of Cyber Security Monitoring
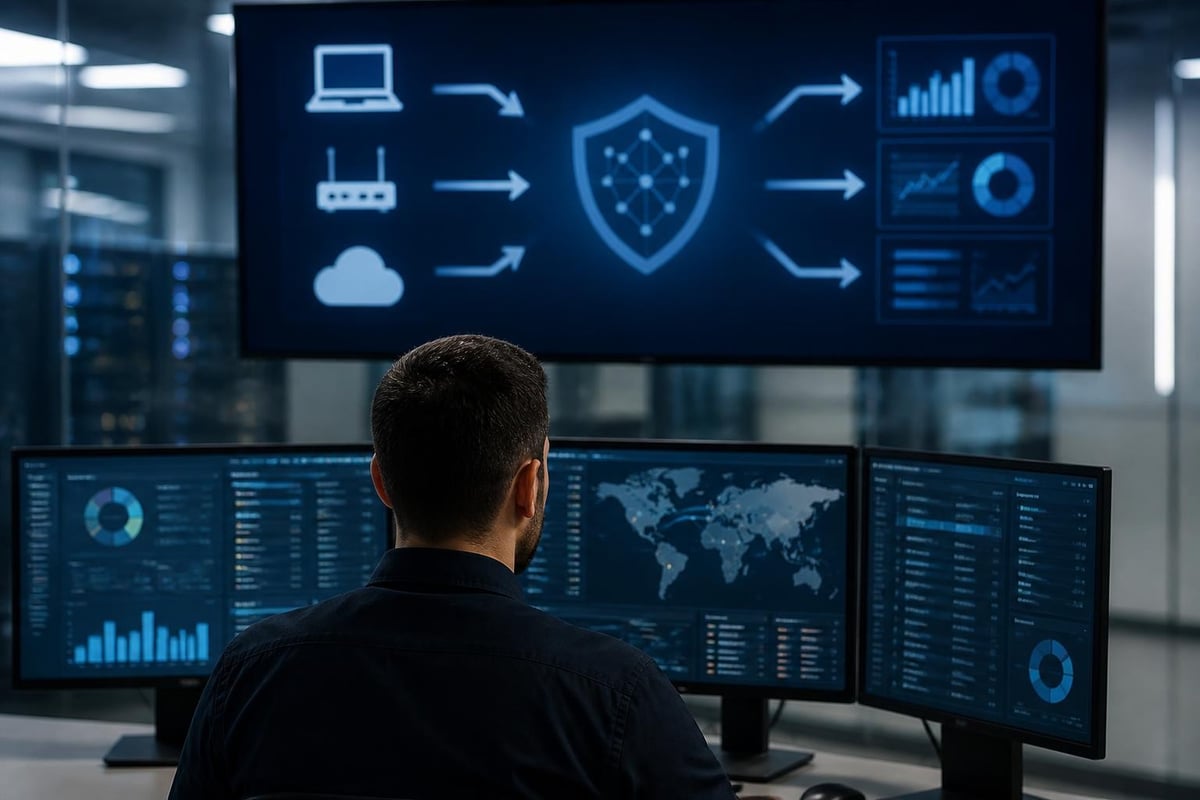
Cyber security monitoring encompasses the continuous observation, analysis, and response to security events across an organization's entire digital infrastructure. This practice extends far beyond simple antivirus scans or firewall logs. It involves comprehensive surveillance of networks, endpoints, applications, and cloud environments to detect anomalies, unauthorized access attempts, and potential security breaches.
The primary objective centers on early threat detection. Modern monitoring systems analyze millions of events daily, correlating data from disparate sources to identify patterns that signal malicious activity. This proactive approach reduces dwell time (the period attackers remain undetected in a system) from weeks or months to hours or even minutes.
Core Components of Effective Monitoring
Building a robust monitoring infrastructure requires several integrated elements working in harmony:
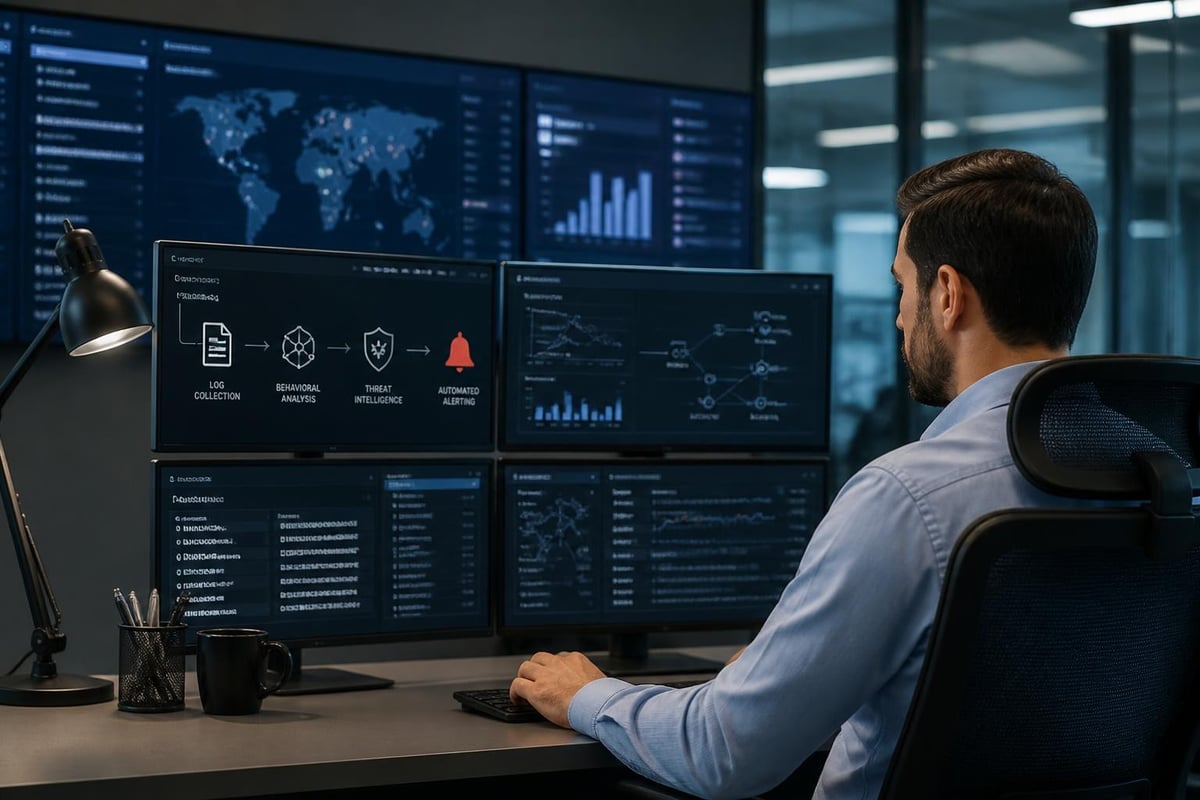
- Log collection and aggregation from all network devices, servers, endpoints, and applications
- Real-time event correlation that connects related activities across different systems
- Behavioral analytics that establish baselines and detect deviations from normal patterns
- Threat intelligence feeds providing current information about known attack vectors
- Automated alerting systems that notify security teams of high-priority incidents
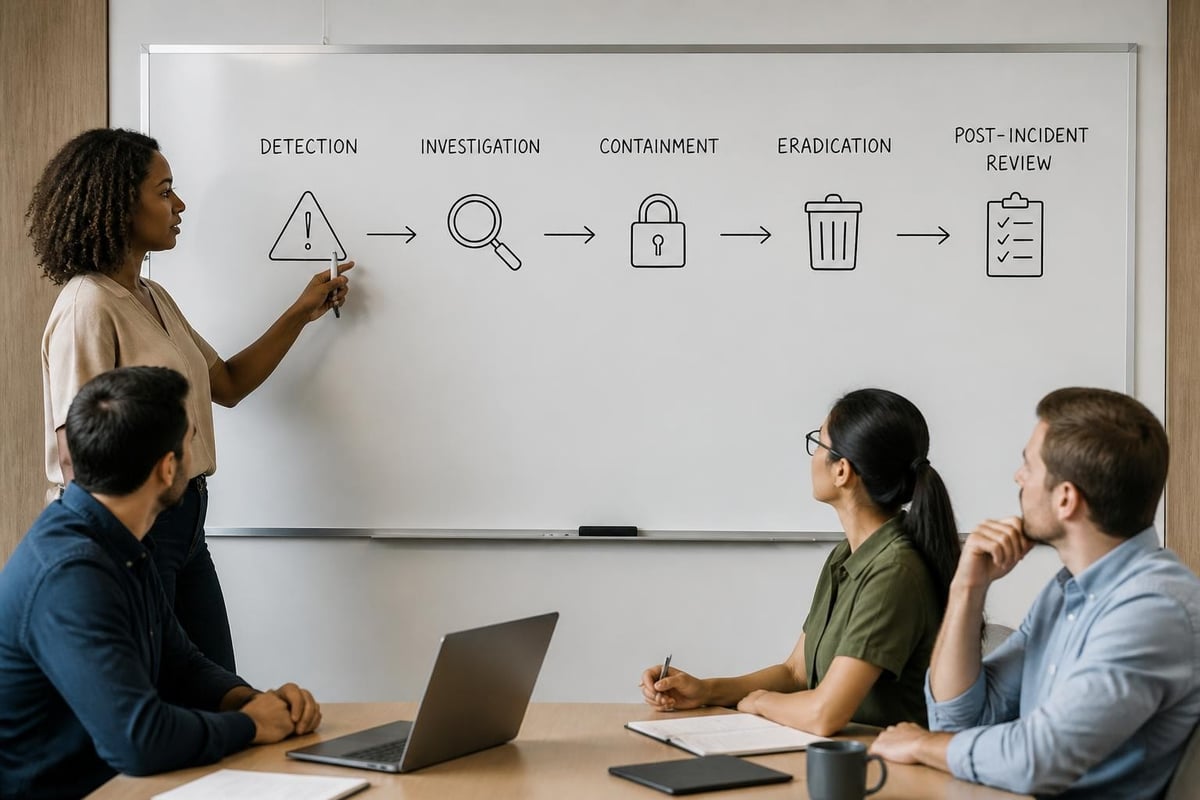
- Incident response workflows enabling rapid containment and remediation
Each component contributes unique value. Log aggregation creates the raw material for analysis, while correlation engines transform isolated events into actionable intelligence. Behavioral analytics represent a particularly powerful capability, as they can identify zero-day threats that signature-based detection might miss.
Threat Detection Methodologies and Approaches
Organizations employ multiple methodologies to identify threats within their environments. Each approach offers distinct advantages and addresses different aspects of the threat landscape.
Signature-Based Detection
This traditional method compares observed activities against databases of known malicious patterns. When a file, network packet, or process matches a stored signature, the system triggers an alert. While highly effective against documented threats, this approach struggles with novel attacks and sophisticated adversaries who modify their tactics specifically to evade known signatures.
Anomaly-Based Detection
Anomaly detection establishes a baseline of normal behavior for users, devices, and applications. The system then flags activities that deviate significantly from these patterns. For example, if an employee account suddenly begins accessing sensitive files at 3 AM or attempting to connect to servers in unfamiliar geographic locations, anomaly-based systems raise alerts.
This methodology excels at identifying insider threats and compromised credentials. According to ENISA’s 2024 Threat Landscape, availability attacks and data-related threats continue to evolve, making behavioral monitoring increasingly critical for early detection.
Heuristic Analysis
Heuristic engines analyze code and behavior patterns to identify suspicious characteristics even when exact signatures don't exist. These systems evaluate factors such as attempted privilege escalation, unusual system calls, or attempts to disable security tools. When multiple suspicious indicators appear together, the system assigns a risk score and generates alerts accordingly.
| Detection Method | Strengths | Limitations | Best Use Cases |
|---|---|---|---|
| Signature-based | Fast, accurate for known threats | Ineffective against new attacks | Commodity malware, known exploits |
| Anomaly-based | Detects unknown threats, insider risks | Higher false positive rates | Account compromise, data exfiltration |
| Heuristic | Identifies suspicious behavior patterns | Requires tuning and refinement | Zero-day threats, advanced malware |
Building a Security Monitoring Infrastructure
Establishing effective cyber security monitoring requires careful planning and strategic technology selection. The infrastructure must scale with organizational growth while maintaining performance and accuracy.
Determining Monitoring Scope
Begin by identifying all assets requiring surveillance. This inventory should include:
- All network perimeters and internal segments
- Server infrastructure (physical, virtual, and cloud-based)
- Endpoint devices including workstations, laptops, and mobile devices
- Applications and databases containing sensitive information
- Identity and access management systems
- Cloud services and third-party integrations
Comprehensive asset visibility forms the foundation of effective monitoring. Blind spots create opportunities for attackers to operate undetected.
Selecting Monitoring Tools
The market offers numerous monitoring solutions ranging from open-source platforms to enterprise-grade security information and event management (SIEM) systems. Selection criteria should emphasize:
- Integration capabilities with existing security tools and infrastructure
- Scalability to handle current and projected data volumes
- Analysis speed for real-time threat detection
- Usability enabling security teams to investigate alerts efficiently
- Automation features reducing manual triage burden
For individual users and small businesses, consolidated security solutions eliminate the complexity of managing multiple disparate tools. Modern all-in-one platforms integrate multiple security functions while maintaining the comprehensive visibility necessary for effective monitoring.
Implementing Continuous Monitoring Practices
Successful cyber security monitoring extends beyond technology deployment. It requires disciplined operational practices and continuous refinement.
Establishing Logging Standards
Comprehensive logging provides the data foundation for all monitoring activities. The OWASP Logging Cheat Sheet offers practical guidance on implementing security-focused logging practices, including proper sanitization and secure log transport.
Essential logging requirements include:
- Authentication and authorization events (successful and failed attempts)
- Privileged operations and administrative actions
- Configuration changes to critical systems
- Data access patterns, especially for sensitive information
- Network connections and data transfers
- Application errors and security exceptions
Logs must capture sufficient detail for forensic analysis while avoiding excessive verbosity that creates storage challenges and obscures critical events. Standardized formats facilitate correlation across diverse systems.
Alert Tuning and False Positive Management
Initial monitoring deployments typically generate overwhelming alert volumes, many representing false positives. Effective programs implement systematic tuning processes:
- Categorize alerts by severity, asset importance, and threat type
- Analyze false positives to understand root causes
- Refine detection rules to reduce noise while maintaining sensitivity
- Document exceptions for legitimate activities that trigger alerts
- Measure and track false positive rates over time
The goal balances sensitivity (detecting real threats) with specificity (avoiding false alarms). Teams should aim for manageable alert volumes that enable thorough investigation of each incident.
Threat Hunting Operations
Beyond automated detection, proactive threat hunting involves security analysts actively searching for indicators of compromise that automated systems might miss. The SANS 2024 Threat Hunting Survey demonstrates that organizations with mature hunting programs detect threats significantly faster than those relying solely on automated alerts.
Effective hunting methodologies include:
- Hypothesis-driven investigations based on threat intelligence
- Baseline analysis identifying subtle deviations in normal patterns
- Stack ranking to find statistical outliers across large datasets
- Guided hunting using frameworks like MITRE ATT&CK to systematically search for adversary techniques
Operationalizing Monitoring Programs
Translating monitoring capabilities into measurable security outcomes requires structured operational processes and clear metrics.
Incident Response Integration
Cyber security monitoring provides value only when detection leads to effective response. Monitoring systems should integrate directly with incident response workflows, automatically creating tickets, enriching alerts with contextual data, and suggesting appropriate containment actions.
Response playbooks define standardized procedures for common alert types. When behavioral analytics detect a compromised credential, for example, the playbook might specify immediate password reset, session termination, and review of recent account activity.
Metrics and Performance Measurement
Organizations should track key performance indicators that demonstrate monitoring program effectiveness:
| Metric | Definition | Target Range |
|---|---|---|
| Mean Time to Detect (MTTD) | Average time from initial compromise to detection | < 24 hours |
| Mean Time to Respond (MTTR) | Average time from detection to containment | < 1 hour for critical incidents |
| Alert-to-Incident Ratio | Percentage of alerts representing actual incidents | > 20% (after tuning) |
| Coverage Percentage | Proportion of assets with active monitoring | > 95% |
| False Positive Rate | Alerts investigated but determined benign | < 30% |
These metrics identify improvement opportunities and demonstrate program maturity to stakeholders.
Staffing and Skill Requirements
Effective monitoring requires appropriately skilled personnel. Depending on organizational size and complexity, teams might include:
- Security analysts who investigate alerts and conduct initial triage
- Threat hunters who proactively search for sophisticated threats
- Detection engineers who develop and refine monitoring rules
- Incident responders who contain and remediate identified threats
- Forensic specialists who conduct detailed post-incident analysis
Smaller organizations often outsource monitoring to managed security service providers (MSSPs) or rely on automated platforms that reduce technical skill requirements.
Advanced Monitoring Capabilities
As programs mature, organizations can implement sophisticated monitoring techniques that provide deeper visibility and enhanced threat detection.
Behavioral Analytics and Machine Learning
Modern monitoring platforms leverage machine learning algorithms to establish dynamic baselines and identify subtle anomalies. These systems adapt as environments evolve, maintaining accuracy without constant manual tuning. User and entity behavior analytics (UEBA) can detect compromised credentials, insider threats, and advanced persistent threats that evade traditional detection methods.
Machine learning excels at identifying patterns across massive datasets. Algorithms can recognize that while individual actions appear benign, their combination or timing suggests malicious intent.
Deception Technology
Honeypots, honeynets, and decoy credentials create attractive targets for attackers while providing early warning of intrusion attempts. When an attacker interacts with deception assets, security teams receive high-confidence alerts requiring immediate investigation. Since legitimate users never access these resources, false positive rates approach zero.
Threat Intelligence Integration
Incorporating external threat intelligence enriches monitoring capabilities by providing context about current attack campaigns, known threat actor tactics, and emerging vulnerabilities. Feeds from commercial providers, information sharing organizations, and open-source intelligence help prioritize alerts and guide hunting activities. Our guide to cyber intelligence feeds explains how to choose and use them effectively in 2026.
The Verizon Data Breach Investigations Report offers empirical data about prevalent attack patterns, informing which monitoring controls provide maximum value against real-world threats.
Cloud and Hybrid Environment Monitoring
Cloud adoption introduces unique monitoring challenges requiring specialized approaches and tools.
Cloud-Native Security Monitoring
Cloud platforms provide extensive logging and monitoring capabilities through native services. Microsoft Azure Architecture guidance for monitoring and Google Cloud security best practices offer framework-specific recommendations for implementing comprehensive cloud monitoring.
Key considerations include:
- Monitoring control plane activities (who creates, modifies, or deletes resources)
- Tracking data access patterns across storage services
- Analyzing identity and access management configurations
- Monitoring serverless function executions and API gateway traffic
- Correlating events across multiple cloud services and regions
Unified Monitoring Across Hybrid Environments
Organizations operating hybrid infrastructures must correlate events across on-premises systems, multiple cloud providers, and edge locations. This requires centralized log aggregation, unified threat intelligence, and consistent detection rules that account for environmental differences while identifying coordinated attacks spanning multiple platforms.
Regulatory Compliance and Monitoring Requirements
Many regulatory frameworks mandate specific monitoring capabilities and retention periods. Understanding these requirements ensures monitoring programs satisfy compliance obligations while providing security value.
Common Compliance Requirements
Different regulations emphasize various monitoring aspects:
- PCI DSS requires file integrity monitoring, access logging, and security event tracking
- HIPAA mandates audit controls and access logging for protected health information
- GDPR emphasizes monitoring for unauthorized data access and breach detection
- SOC 2 requires logging, monitoring, and incident response capabilities
CISA’s Continuous Diagnostics and Mitigation program provides federal guidance on automated sensors and continuous monitoring that many organizations adapt for their own risk management programs.
Log Retention and Evidence Preservation
Compliance requirements often specify minimum log retention periods, typically ranging from 90 days to seven years. Beyond regulatory mandates, extended retention supports threat hunting, forensic investigations, and trend analysis. Organizations must balance retention requirements against storage costs and privacy considerations.
Simplifying Monitoring for Non-Technical Users
While enterprise monitoring systems require specialized expertise, individual users and small businesses need accessible solutions that provide comprehensive protection without demanding technical knowledge.
Modern security platforms address this need by consolidating multiple security functions into unified interfaces. Rather than managing separate tools for antivirus, firewall monitoring, intrusion detection, and behavioral analysis, integrated solutions present a single, coherent view of security status. These platforms leverage the same advanced technologies (behavioral analysis, threat intelligence, anomaly detection) used by enterprise systems while presenting findings in clear, actionable terms.
NetGuardian Pro exemplifies this approach, with 14 security modules working together through a self-learning defense system that understands normal computer behavior and identifies anomalies. Rather than overwhelming users with technical alerts, the platform presents findings in plain language with clear, single-click remediation options.
Monitoring Program Evolution and Continuous Improvement
Cyber security monitoring is not a static implementation but an evolving capability that must adapt to changing threats, technologies, and business requirements.
Regular Assessment and Optimization
Quarterly reviews should evaluate:
- Detection coverage across the current threat landscape
- Alert quality and investigation efficiency
- Response effectiveness and containment speed
- Technology performance and scalability
- Staff skill development and training needs
Organizations should conduct periodic red team exercises and purple team activities where offensive security specialists attempt to evade detection while monitoring teams refine their capabilities.
Staying Current with Evolving Threats
Threat actors continuously develop new techniques and exploit emerging technologies. Monitoring programs must evolve accordingly by:
- Subscribing to threat intelligence feeds and security research
- Participating in information sharing communities
- Attending security conferences and training programs
- Testing detection capabilities against current attack frameworks
- Implementing lessons learned from security incidents
The OWASP Developer Guide emphasizes embedding security monitoring requirements into development processes, ensuring new applications include appropriate logging and observability from inception.
Building Security Culture
Technology alone cannot ensure effective monitoring. Organizations must cultivate security awareness where employees understand their role in threat detection and promptly report suspicious activities. Regular training, simulated phishing exercises, and clear reporting channels transform the entire workforce into an extended monitoring network.
Emerging Trends Shaping Future Monitoring
Several technological and operational trends will significantly impact cyber security monitoring practices over the coming years.
Extended Detection and Response (XDR)
XDR platforms consolidate security telemetry from endpoints, networks, cloud workloads, and applications into unified analytics engines. This convergence improves threat detection by correlating events across previously siloed security tools, reducing blind spots and accelerating investigation workflows.
Automation and Orchestration
Security orchestration, automation, and response (SOAR) platforms handle routine tasks, enabling human analysts to focus on complex investigations. Automated playbooks can contain threats, gather forensic evidence, and initiate remediation without human intervention, dramatically reducing response times.
Zero Trust Architecture
Zero trust principles (never trust, always verify) reshape monitoring priorities. Rather than focusing primarily on perimeter defenses, monitoring programs emphasize continuous authentication verification, micro-segmentation enforcement, and detailed access logging regardless of network location.
Effective cyber security monitoring provides the visibility, detection capabilities, and rapid response necessary to protect digital assets in 2026's threat landscape. By implementing comprehensive logging, leveraging behavioral analytics, integrating threat intelligence, and maintaining disciplined operational practices, organizations can significantly reduce their exposure to cyber threats. For individuals and small businesses seeking comprehensive protection without technical complexity, NetGuardian Pro delivers enterprise-grade monitoring through an accessible platform that learns normal behavior patterns and presents clear, actionable alerts whenever anomalies appear. Investing in robust monitoring capabilities today prevents the devastating consequences of undetected breaches tomorrow.