Computer Network Attack: What It Is and How to Stay Safe
A computer network attack happens when someone tries to access, disrupt or damage your computer through its network connections. Unlike a virus that spreads through files, these attacks exploit the way your Windows 11 PC talks to the internet, your home Wi-Fi or other devices. Understanding how these attacks work helps you recognise suspicious activity and respond before damage occurs.
What is a computer network attack
A computer network attack is any deliberate attempt to compromise a computer or network by exploiting its connections. Attackers use your Wi-Fi, Bluetooth, USB or internet connection to gain unauthorised access, steal information or disrupt your system.
These attacks differ from traditional malware because they target the communication channels between devices rather than infected files. An attacker might scan your home network looking for open ports, intercept data travelling over public Wi-Fi or exploit a vulnerability in how your PC handles network requests.
The MITRE ATT&CK framework documents hundreds of specific techniques attackers use, from initial access through network connections to data theft and system control. This knowledge base shows how computer network attack methods have evolved beyond simple intrusion attempts into sophisticated, multi-stage operations.
Common types targeting Windows 11 users
Port scanning attacks probe your PC looking for open network ports that might accept connections. Attackers scan thousands of ports in seconds, identifying which services your computer is running and whether any have known vulnerabilities.
Man-in-the-middle attacks intercept data between your PC and websites or services you use. On public Wi-Fi, an attacker can position themselves between you and the network, reading or modifying everything you send and receive.
Denial of service attempts flood your connection with traffic, making your internet unusable. While large-scale attacks target businesses, smaller attempts can disrupt home networks or individual PCs.
Lateral movement happens after initial compromise. Attackers move through your home network from one device to another, looking for valuable data or systems to control.
How attackers target home and small business networks
Most computer network attacks start with reconnaissance. Attackers scan IP address ranges looking for accessible devices, much like checking doors in a neighborhood to find unlocked ones.
Your home router and Windows 11 PC constantly announce their presence to the internet. Attackers use automated tools to identify your network type, operating system and running services. This information helps them choose which attack methods are most likely to succeed.
Exploitation phase
Once attackers identify a target, they attempt exploitation. This might involve:
- Sending specially crafted network packets that trigger vulnerabilities in Windows services
- Attempting to guess or crack Wi-Fi passwords using known weaknesses
- Exploiting outdated firmware in routers or network devices
- Using social engineering to trick you into allowing network access
The ENISA Threat Landscape 2024 reports that network-based attacks remain among the top threats, with attackers increasingly targeting home offices and small businesses that lack enterprise-grade protection.
Persistence and control
After gaining initial access, attackers establish persistence by creating backdoors, hidden network connections that let them return even after you restart your PC. These connections often use encrypted channels that blend with normal HTTPS traffic, making them difficult to spot without proper monitoring.
Recognising suspicious network activity on your PC
You can identify potential computer network attacks by watching for unusual network behavior on your Windows 11 system.
Unexpected outbound connections appear when programs try to communicate with servers you do not recognize. While many legitimate applications connect to update servers, ransomware and spyware create connections to attacker-controlled systems.
Unusual data transfer volumes might indicate someone is exfiltrating your files. If your network upload activity spikes when you are not backing up data or sharing large files, investigate immediately.
Failed connection attempts filling your security logs suggest someone is probing your PC's defenses. Repeated attempts from the same IP addresses or during specific times often indicate automated attack tools.
Monitoring tools and techniques
Windows 11 includes basic network monitoring through Task Manager and Resource Monitor. Press Ctrl+Shift+Esc, then click the Performance tab and select Wi-Fi or Ethernet to see current network activity.
For deeper insight, the netstat command shows active connections. Open Command Prompt and type netstat -ano to list all connections with their destination addresses and associated programs.
| Tool | What it shows | When to use it |
|---|---|---|
| Task Manager | Current network usage by app | Quick daily checks |
| Resource Monitor | Detailed connection list | Investigating suspicious activity |
| Event Viewer | Network security logs | After suspected intrusion |
| netstat command | Active connections and ports | Technical troubleshooting |
However, these built-in tools require technical knowledge to interpret and do not provide context about whether connections are legitimate or threatening.
Protecting your Windows 11 PC from network attacks
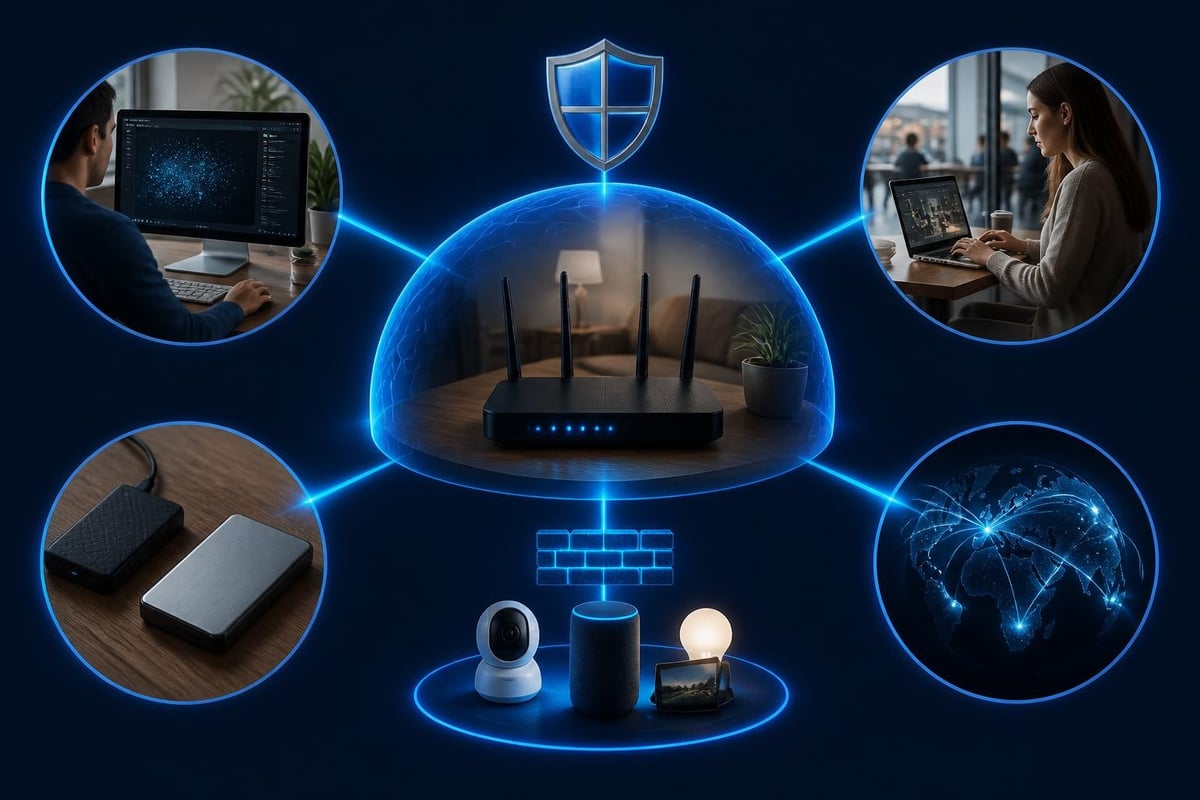
Effective protection requires multiple layers working together. No single tool stops every computer network attack, but combining defenses significantly reduces your risk.
Router and network hardening
- Change your router's default administrator password to something unique and strong
- Enable WPA3 encryption on your Wi-Fi network (or WPA2 if WPA3 is unavailable)
- Disable WPS (Wi-Fi Protected Setup), which has known security weaknesses
- Turn off remote management unless you specifically need it
- Update your router firmware regularly
Your router forms the first line of defense. The CISA guidance on communications infrastructure emphasizes that hardening network devices prevents many attacks before they reach individual PCs.
Windows 11 system configuration
Enable Windows Firewall on all network profiles (Domain, Private, Public). Windows 11 includes a capable firewall that blocks most unsolicited inbound connections by default.
Turn on network discovery only when needed. Open Settings, Network & Internet, Advanced network settings, then Advanced sharing settings. Disable network discovery and file sharing on public networks.
Review which apps have network access. Settings, Privacy & security, App permissions, then scroll to Network to see which applications can use your internet connection.
Active network monitoring
NetGuardian Pro provides real-time network intrusion detection specifically designed for Windows 11 PCs. Its 14 detection modules monitor Wi-Fi, USB and Bluetooth connections, identifying suspicious patterns that suggest a computer network attack is underway. The system includes ransomware behavior monitoring that watches for the network signatures typical of encryption attacks, such as rapid file access patterns combined with connections to command-and-control servers. Unlike antivirus software, which focuses on file-based threats, NetGuardian Pro complements your existing security by analyzing network behavior and giving you clear alerts when suspicious connections occur.
Travel and public Wi-Fi protection
Public Wi-Fi networks present the highest risk for man-in-the-middle attacks. An attacker on the same coffee shop network can intercept your traffic or create a fake access point that mimics the legitimate network.
Use a VPN whenever connecting to public networks. A virtual private network encrypts all traffic between your PC and the VPN server, preventing interception. The built-in WireGuard VPN included with some network security tools provides strong encryption with minimal performance impact.
Verify network names with staff before connecting. Attackers create networks with names like "Free Airport WiFi" or "Hotel Guest Network" to trick travelers into connecting.
Avoid accessing sensitive accounts on public networks when possible. Save banking, shopping and work tasks for trusted networks or times when you have VPN protection active.
The NIST guidance on data confidentiality attacks provides detailed recommendations for protecting data in transit, particularly relevant for business travelers handling sensitive information.
Responding when you suspect an attack
Quick action limits damage when you detect a computer network attack in progress. Follow these steps in order.
Immediate response
Disconnect from the network by turning off Wi-Fi or unplugging your Ethernet cable. This stops the attack immediately, though it also prevents you from accessing online resources.
Document what you observed before symptoms disappear. Take screenshots of suspicious connections, note unfamiliar IP addresses and record when you first noticed problems. This information helps during investigation and recovery.
Run a full antivirus scan while disconnected. Although network attacks differ from file-based malware, attackers often install additional threats after gaining access. Update your antivirus definitions before scanning if possible.
Investigation and recovery
Check recent Windows security logs. Open Event Viewer, expand Windows Logs, then select Security. Look for failed logon attempts, unusual account activity or security policy changes you did not authorize.
Review installed programs and startup items. Press Windows+R, type msconfig, then click the Startup tab to see what launches when your PC boots. Remove anything unfamiliar or suspicious.
Change passwords for important accounts, starting with your Windows login and email. If an attacker gained access to your PC, they might have captured passwords through keylogging or by reading saved credentials.
The CISA incident response playbooks outline structured approaches to investigating and recovering from network intrusions, adaptable for home and small business environments.
When to seek professional help
Contact a security professional if you find evidence of:
- Data theft or unauthorized access to sensitive files
- Ransomware encryption demands
- Banking or financial account compromise
- Persistent infections that survive antivirus scans
- Attacks targeting your business operations
Small businesses should also report serious incidents to relevant authorities. In the United States, the FBI's Internet Crime Complaint Center accepts reports at ic3.gov. South African businesses can report to the South African Police Service's cybercrime division.
Building long-term network security practices
Sustained protection against computer network attacks requires ongoing attention rather than one-time fixes.
Regular maintenance schedule
Weekly tasks include checking Windows Update for security patches and reviewing your most resource-intensive network connections through Task Manager. This quick review helps you establish a baseline of normal activity.
Monthly tasks should cover router firmware updates, reviewing connected devices on your network and verifying your firewall remains active across all network profiles.
Quarterly reviews provide time to audit user accounts, remove unused programs and assess whether your security tools still meet your needs as threats evolve.
Staying informed about threats
The SANS comparative analysis of network forensic tools demonstrates how detection capabilities improve as security tools learn from new attack patterns. Keeping your security software updated ensures you benefit from the latest threat intelligence.
Subscribe to security advisories from Microsoft and your security tool vendors. These alerts notify you of newly discovered vulnerabilities that require immediate patches or configuration changes.
Family and employee education
Everyone using your network needs basic security awareness. Teach household members or employees to:
- Recognize phishing attempts that trick users into allowing network access
- Verify requests for remote assistance or connection permissions
- Report suspicious network behavior promptly
- Understand why security updates and scans matter
Even sophisticated network monitoring cannot prevent attacks that succeed through social engineering, where attackers manipulate people rather than exploiting technical vulnerabilities.
Network security for specific scenarios
Different situations present unique computer network attack risks requiring tailored approaches.
Home office security
Working from home blurs the line between personal and professional networks. Your employer's sensitive data shares network space with your children's gaming devices and smart home gadgets.
Create a separate network for work devices if your router supports guest networks or VLANs. This isolation prevents a compromise on personal devices from spreading to work systems.
Use your employer's VPN whenever accessing company resources. This encrypts work traffic and routes it through your company's security infrastructure rather than exposing it to your home network.
Schedule security-focused network reviews. Small businesses can explore the latest posts on network security best practices through NetGuardian’s security resources to stay current on emerging threats.
Traveling with Windows 11 laptops
Business and leisure travelers face heightened computer network attack risk, especially in hotels, airports and cafes where attackers specifically target travelers handling sensitive information.
Assume all public networks are hostile. Use VPN connections for all activity, not just accessing sensitive sites. Attackers can monitor general browsing habits to build profiles for targeted attacks later.
Disable automatic Wi-Fi connections. Windows 11 normally reconnects to known networks automatically, but an attacker can create a fake network with the same name as your home or office Wi-Fi. Configure Windows to ask before connecting.
Enable network location awareness. Windows 11 adjusts firewall rules based on whether you mark a network as Public or Private. Always select Public for networks outside your home or office.
Multi-device households
The average home now contains a dozen or more network-connected devices. Each represents a potential entry point for computer network attacks.
Inventory your connected devices. You cannot protect what you do not know exists. List every smartphone, tablet, PC, smart TV, printer and IoT gadget on your network.
Segment IoT devices when possible. Many smart home gadgets have poor security and never receive updates. Keeping them on a separate network limits damage if they become compromised.
Consider the academic research on adversarial challenges in network intrusion detection, which examines how attackers deliberately craft network traffic to evade detection systems. This research informs the development of more resilient monitoring tools that adapt to evasion techniques.
Legal and ethical dimensions of network security
Understanding computer network attacks also means recognizing their legal implications and the broader cybersecurity landscape.
When network security becomes national security
State-sponsored attackers conduct computer network attacks as part of intelligence gathering or offensive cyber operations. The Tallinn Manual on international cyber law explores when network attacks rise to the level of armed conflict under international law.
While home users and small businesses rarely face state-level threats, the techniques developed for sophisticated attacks eventually filter down to criminal tools. Understanding this progression helps anticipate emerging threats.
Your rights and responsibilities
You have the right to protect your own network and devices from computer network attacks. Running security tools, monitoring your connections and blocking suspicious traffic are all legal protective measures.
However, "hacking back" or launching counter-attacks against attackers is illegal in most jurisdictions. When you identify an attack source, report it to authorities rather than attempting retaliation.
Understanding computer network attacks transforms you from a passive user into an active defender of your digital space. By monitoring your Windows 11 PC's network connections, maintaining strong router security and responding quickly to suspicious activity, you create multiple barriers against intrusion. NetGuardian Pro helps you detect and respond to network-based threats with 14 specialized modules that monitor Wi-Fi, USB and Bluetooth connections in real time, giving you clear alerts and practical controls without requiring deep technical knowledge.